Tips From a Hacker on License Checking
Explore techniques used by crackers and learn how to design more secure license checking schemes for audio software, improving protection against piracy.
AI in Healthcare - Integrating AI Solutions for Patient Engagement and Data Management
Explore AI's impact on healthcare with Eric Landry, discussing patient engagement, data management, and privacy concerns. Learn about benchmarking LLMs and developing innovative solutions to improve health outcomes.
Controversy and Clarity Around Cyber Insurance
Explore legal issues, benefits, and pitfalls of cyber insurance with attorney Rich Gatz, and learn best practices to minimize risk in this emerging market.
How Using Open Source Code Can Leave You Exposed to Hackers
Explore the security risks of open-source code, focusing on the Log4Shell vulnerability and its widespread impact on applications.
Ransomware: To Pay or Not to Pay - Legal and Business Perspectives
Explore legal perspectives on ransomware, cyber insurance, data recovery strategies, and law enforcement engagement in cybersecurity incidents.
The Legality and Constitutionality of Banning TikTok
Explore the legal and constitutional implications of TikTok bans, examining freedom of speech rights and assessing potential national security threats.
Shifting Cybersecurity Liability to Vendors and Suppliers - DragonCon 2023
Explore supply chain security breaches, vendor obligations, liability issues, and the effectiveness of certifications in protecting upstream customers.
Ransomware Attacks on Small Businesses - Protective Measures
Explore strategies for small businesses to protect against ransomware attacks, focusing on cost-effective security measures and best practices.
Is Embarrassing a Public Official via Security Disclosures a Hacking Crime?
Explore the legal and ethical implications of disclosing security vulnerabilities in government systems and the potential consequences for whistleblowers.
Data Scraping - Clearview AI, HiQ, and Other Controversies
Explore legal and ethical implications of data scraping through case studies like Clearview AI and HiQ, examining privacy concerns and TOS violations.
Automating Incident Response: Scalable and Fast, Within Minutes
Discover how to automate incident response using open-source tools, combining digital forensics with DevOps for faster, more efficient security incident handling at scale.
Logos: Where Privacy, Censorship-Resistance and Permissionlessness Meet
Explore the evolution of decentralized, censorship-resistant infrastructure for preserving digital privacy and free speech, focusing on open-source projects like Waku, Codex, and Nomos.
Security Certification Insights: Analyzing the Global Certification Ecosystem
Explore sec-certs, a tool for analyzing security certifications, providing unique insights into the certification ecosystem through automated data processing and open-source research.
Open-source Projects in Cyber Security
Explore open-source cybersecurity projects, including YARA-related tools like GenRex, YARI, and YLS. Gain insights into innovative developments enhancing malware analysis and industry protection.
Implementing DevSecOps in Production with Stackrox and Tekton
Implement robust DevSecOps pipelines using Stackrox and Tekton. Eliminate security risks, secure the software supply chain, and provide automated guardrails for developers.
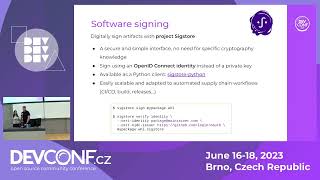
Securing Python Projects Supply Chain
Explore best practices and tools for securing Python projects' supply chain, from development to distribution. Learn about cryptographic signatures, SBOMs, and SLSA attestations.
Unveiling the Mysteries of Digitally Storing the Human Mind
Explore the intricacies of digitally storing human consciousness, delving into mind storage technologies, ethical considerations, and the space required to capture a human mind's essence.
We Are Doing It Wrong: Threat Modeling
Explore common pitfalls in threat modeling and learn how to avoid them. Gain insights from real-world breaches and discover effective strategies for securing software development.
Life beyond FIPS 140-3 - Identity Tales
Explore FIPS 140-3 impact on identity management, focusing on FreeIPA and Samba AD DC. Uncover hidden issues and challenges for Linux administrators in compliance implementation.
Secure Workload Identities with SPIFFE, Cert-Manager, and Trust-Manager
Secure cloud-native workloads using SPIFFE, cert-manager, and trust-manager for robust identity management and authentication in distributed systems.

DevSecOps: Dynamic Application Security Testing for Identifying Vulnerabilities
Explore security practices in DevSecOps and learn DAST testing to identify vulnerabilities in deployed applications.