Securing Software Repositories
Explore strategies for securing software repositories, focusing on best practices and tools to protect against vulnerabilities and ensure code integrity.
Mobilizing for the Open Source Security Mobilization Plan
Learn how OpenSSF's 10-point plan aims to improve open source software security and discover ways to contribute to this crucial initiative.
Trials, Tribulations and Triumphs - An End User's Perspective on Software Supply Chain Security
Explore enterprise challenges, initiatives, and future vision for open source software supply chain security from an end user perspective. Learn about threat mitigation strategies and collaborative efforts.
Securing Software Repositories - EMEA Friendly
Explore best practices for securing software repositories, focusing on EMEA-specific considerations and strategies to enhance code protection and integrity.
Secure Software Supply Chain Framework (S2C2F) Guide - OpenSSF SIG Meeting
Explore secure open source software consumption practices and improve your software supply chain integrity with the S2C2F guide.
Secure Software Supply Chain at IBM
Explore IBM's approach to securing the software supply chain, focusing on key strategies and best practices for enhancing cybersecurity in development processes.
Sigstore: Using Transparent Digital Signatures to Help Secure the Software Supply Chain
Explore transparent digital signatures with Sigstore to enhance software supply chain security and learn practical implementation strategies.
Securing Software Repositories - EMEA Friendly
Explore best practices for securing software repositories, focusing on strategies tailored for EMEA regions and addressing global cybersecurity challenges.
Securing Software Repositories - EMEA Friendly
Explore strategies for securing software repositories, focusing on best practices and tools to protect against vulnerabilities and ensure code integrity.
Securing Software Repositories - EMEA Friendly
Explore strategies for safeguarding software repositories, focusing on EMEA-specific considerations and best practices for enhanced security measures.
Securing Software Repositories - EMEA Friendly
Explore best practices for securing software repositories, focusing on strategies tailored for EMEA regions to enhance overall project security.
Memory Tagging Extension: Delivering More Robust and Secure Games
Explore Memory Tagging Extension to enhance game robustness and security. Learn how this technology improves memory safety and protects against vulnerabilities in game development.
New Methods of Recon - Enhancing Reconnaissance Techniques
Refine and expand your reconnaissance toolkit with top hacker OrwaGodfather's precise tactics, enhancing your bug hunting capabilities.
Intellectual Property with GenAI: What LLM Developers Need to Know
Explore intellectual property issues in AI development, covering US IP laws, challenges in using and training models, and future legal trends affecting AI products and businesses.
Supply Chain Security with KubeClarity: Introduction and Implementation
Explore supply chain security fundamentals, historical attacks, and KubeClarity tool. Learn about SBOMs, their benefits, and see KubeClarity in action for enhanced software security.
AI and Cybersecurity - Insights from Industry and Academia
Explore the intersection of AI and cybersecurity, examining threats, applications, and management strategies in complex information systems.
AI and Cybersecurity - Challenges and Opportunities
Explore the intersection of AI and cybersecurity, examining threats, challenges, and solutions in complex information systems and AI applications.
AI and Cybersecurity - Challenges and Opportunities in Complex Information Systems
Explore AI's role in cybersecurity and its impact on complex information systems, with insights from industry and academia on managing cyber threats.
AI and Cybersecurity - Challenges and Opportunities in Complex Information Systems
Explore AI's role in cybersecurity and its impact on complex information systems. Gain insights from industry and academia on managing cyber threats in AI-related environments.
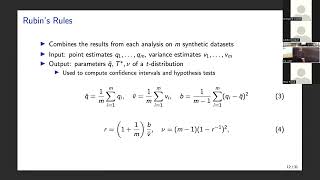
Noise-Aware Statistical Inference with Differentially Private Synthetic Data
Explore noise-aware statistical inference techniques for differentially private synthetic data, combining multiple imputation and Bayesian modeling to produce accurate uncertainty estimates for population-level quantities.
Sustainability in the Consumer Goods Value Chain and the Role of AI
Explore AI's role in sustainable logistics and supply chain management, focusing on reducing emissions, improving efficiency, and enhancing resilience and security.