SQL Injection Explained - Understanding Attacks and Prevention
Comprehensive guide to SQL injection attacks: types, vulnerabilities, and prevention techniques. Learn to identify, exploit, and protect against database security threats through practical examples and best practices.

The Arrest of Telegram CEO Pavel Durov and Its Implications for Tech Oversight and Free Speech
Eli Pariser discusses Pavel Durov's arrest, exploring implications for tech oversight and free speech. This live conversation delves into the future of digital platforms and online democracy.
Seven Things About API Security - NDC Oslo 2024
Explore API security best practices, OWASP top vulnerabilities, live demo, and real-world case studies to enhance your API protection strategies and prevent potential breaches.
The Final Frontier - Security APIs in Modern Browsers
Explore modern browser security APIs and mechanisms that protect against common web attacks, enhance authentication, and restrict browser behavior, with code demonstrations and future insights.
Cyber Security Afloat - Securing Very Big Iron
Explore vulnerabilities in maritime cybersecurity, potential impacts on supply chains and safety, and current protective measures for ships and offshore units.
Tales from Incident Response - Unmasking the Threat Actor's Inner Sanctum
Unmasking threat actors' inner workings through incident response tales. Gain insights into cybersecurity challenges and strategies from a principal advisor's real-world experiences at a major hacking conference.
Hacking Satellite, Aerospace, Avionics, Maritime and Drone Systems
Explore vulnerabilities in satellite, aerospace, avionics, maritime, and drone systems. Learn about potential security risks and hacking techniques in these critical infrastructures.
Saving the Post-Quantum World with Neural Networks
Explore neural networks' role in post-quantum cryptography and cybersecurity. Learn about cutting-edge research and applications in this emerging field of information security.
War Stories from the SOC - Cybersecurity Incident Response Lessons
Cybersecurity expert shares real-world experiences from Security Operations Center, offering insights into threat detection, incident response, and best practices for defending against cyber attacks.
Echoes of Deception - Fake Content, Ads, and Promises
Explore deceptive online content, ads, and promises in cybersecurity. Learn to identify and combat fake information for enhanced digital safety and awareness.
CIAPO - Code Injection via Arbitrary Pointer Overwrite
Explore code injection via arbitrary pointer overwrite in this cybersecurity presentation. Learn about vulnerabilities, hacking techniques, and defensive strategies from a Bitdefender security researcher.
The Double-Edged Sword of AI in Cybersecurity
Explore AI's dual impact on cybersecurity: enhancing defenses while posing new threats. Gain insights from expert Alexander Benoit on navigating this complex landscape in the digital age.
Driving Forward: Automotive Security in the Digital Era
Explore automotive cybersecurity challenges and solutions in the digital age. Learn about emerging threats, protective measures, and industry trends for safer connected vehicles.
NIS 2 Directive Overview - Cybersecurity Regulations and Implications
Comprehensive overview of the NIS 2 Directive, exploring its impact on cybersecurity regulations and practices across Europe, presented by a national cyber security expert.
Social Engineering with AI and Defending Against It with Human Intelligence
Explore AI-powered social engineering tactics and human-centric defense strategies in this cybersecurity talk. Gain insights on protecting against evolving threats in the digital landscape.
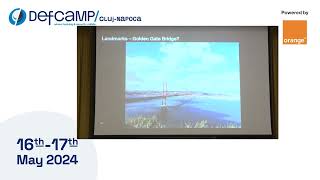
Geolocation and Its Implications
Explore geolocation's impact on cybersecurity with expert Simona David at DefCamp Cluj-Napoca. Gain insights into location-based vulnerabilities and their implications for digital security.
Ransomware as a Service - Are You Prepared?
Explore Ransomware as a Service and its implications for cybersecurity preparedness in this DefCamp Cluj-Napoca 2024 presentation by Alexander Benoit, CEO of Water IT Security & Defense.
Surviving Cyber Attacks - 2024 Edition
Explore cutting-edge strategies for surviving cyber attacks in 2024, presented by Tudor Damian at DefCamp Cluj-Napoca. Learn from industry experts and stay ahead of evolving threats.
Step-by-Step: Application Security Architecture
Comprehensive guide to application security architecture, covering threat modeling, security controls, and best practices for robust software design and implementation.
z/OS Penetration Testing Workflow - When Computers Were Big
Explore z/OS penetration testing workflow in this DefCamp Cluj-Napoca 2024 talk by Denis Stepanov. Learn about cybersecurity techniques for mainframe systems and their modern applications.
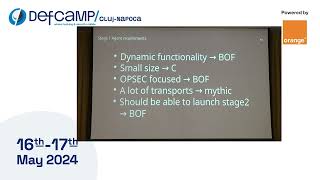
Stage 1 C2 in 3 Days - DefCamp Cluj-Napoca 2024
Explore rapid C2 infrastructure setup for penetration testing in this DefCamp presentation. Learn efficient techniques for Stage 1 Command and Control deployment within tight timeframes.