
SQL Injection Explained - With Free Labs
Comprehensive guide to SQL injection vulnerabilities, featuring expert insights and hands-on practice labs for enhancing web security skills and bug bounty hunting techniques.
How AI Impacts Reconnaissance and Bug Bounties in Cybersecurity
Exploring AI's impact on cybersecurity, this interview covers its role in bug bounties, potential risks, job market effects, and defensive strategies against malicious AI use.
Differential Privacy: Protecting Data Privacy in the Era of Big Data
Explore Differential Privacy, a cutting-edge cybersecurity technique that preserves individual privacy while enabling data analysis. Learn its applications and implementation using PyDP in Python.
Is Apple Intelligence Safe?
Explore the safety and implications of Apple Intelligence, examining its potential benefits and risks when implemented correctly.

Microsoft Justifies Recording Your Screen - Controversy Over Windows Recall Feature
Análisis crítico de Microsoft Recall: su funcionamiento, controversias y posibles implicaciones para la privacidad del usuario en Windows.
Secure Boot Vulnerabilities and Private Key Leaks - Implications and Solutions
Explore recent security breaches, their implications, and learn how to protect yourself online using two-factor authentication and tools like YubiKey.
Securing Trust in the Global Digital Economy - Cyber, Fraud, and Emerging Threats
Experts discuss cybersecurity challenges, fraud prevention, and emerging threats in the global digital economy, exploring strategies to build trust and protect against evolving risks.
The World at Risk - Navigating Modern Threat Landscapes
Experts discuss global security challenges, analyzing modern threats and strategies for navigating complex geopolitical landscapes. Gain insights into risk assessment and mitigation in today's interconnected world.
The Evolving Threat Landscape
Explore global security challenges with former defense and homeland security leaders, discussing emerging threats and strategic responses for a safer world.
Phishing, Fakes, and Fraud - Tackling Transnational Crime and Enhancing Global Security
Experts discuss strategies to combat transnational cybercrime, focusing on phishing, fraud, and counterfeit goods. They explore global cooperation and technological solutions to enhance international security and financial integrity.
The Geopolitics of AI - Global Conference 2024
Explore the global competition, power dynamics, and cooperation opportunities in AI development and deployment, addressing geopolitical implications and regulatory challenges.
Identifying Syscall-Guard Variables for Data-Only Attacks
Innovative technique for detecting critical variables in programs, enabling identification of potential data-only attack vulnerabilities and enhancing cybersecurity defenses against sophisticated threats.
Faults in Our Bus - Novel Bus Fault Attack to Break Trusted Execution Environments in Embedded Systems
Uncover novel bus fault attacks on Trusted Execution Environments in embedded systems, exploring vulnerabilities in SoC system buses and their implications for IoT security and TEE implementations.
Physical Emissions - CHES 2024
Explore cutting-edge research on physical emissions in cryptographic hardware at CHES 2024, chaired by Patrick Schaumont. Gain insights into latest developments and implications for secure system design.

What is JWT and Why - Understanding JSON Web Tokens
Explore JSON Web Token (JWT): its purpose, structure, and benefits for secure information transmission between parties in web development.
Ransomware in Action - MedusaLocker ReadText34
Explore MedusaLocker ransomware's behavior and tactics through dynamic analysis, gaining insights into its encryption process and file manipulation techniques.
I Can't Scan This Website - Cybersecurity Challenges with Cloaking Firewalls
Explore website scanning challenges and cybersecurity techniques with John Hammond. Learn about protective measures like Cloaking Firewall and gain insights into infrastructure security.
Self-Extracting Executables for Hackers
Explore self-extracting executables for hackers: creation, analysis, and implications. Gain insights into this cybersecurity technique for enhanced understanding and protection.
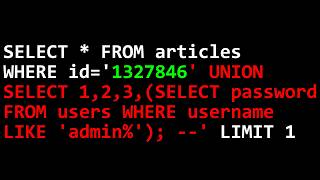
Interactive SQL Injection
Hands-on practice with SQL injection techniques in a safe environment. Learn to identify and exploit vulnerabilities, enhancing your cybersecurity skills and understanding of database security.
The Mark of the Web - Understanding Internet Security Zones
Explore the Mark of the Web security feature, its impact on file downloads, and how it affects system protection and user experience in Windows operating systems.
Recover Quarantined Malware
Explore techniques to safely recover and analyze quarantined malware, enhancing cybersecurity skills and understanding of malicious software behavior.