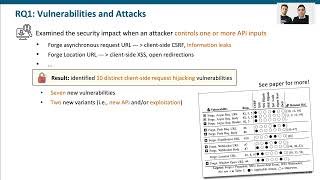
The Great Request Robbery
Explore web security vulnerabilities and attack techniques with a focus on request forgery and injection flaws in modern applications.

BULKOR: Enabling Bulk Loading for Path ORAM
Explore BULKOR, an innovative technique for efficient bulk loading in Path ORAM, enhancing data privacy and security in cloud storage systems.
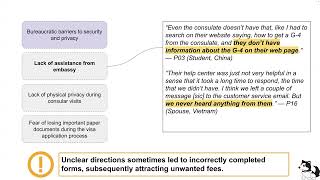
Security, Privacy, and Data Sharing Challenges When Moving to the US - Insights from a Qualitative Study
Explore security, privacy, and data sharing challenges faced by individuals relocating to the US, based on qualitative research findings and expert insights.
Everyone for Themselves: A Qualitative Study About Individual Security Setups of Open Source Software Developers
Explore individual security practices of open-source software developers through qualitative research, uncovering insights into personal setups and strategies.
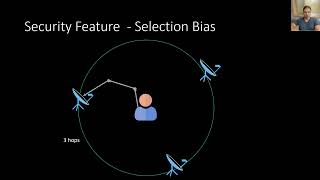
Don't Shoot the Messenger - Localization Prevention of Satellite Internet Users
Explore techniques to prevent localization of satellite internet users, enhancing privacy and security in global communications networks.
New and Early Career Faculty Members in Cybersecurity - May 17, 2024
Explore cybersecurity fundamentals with experts from University of Washington and University of Western Florida. Gain insights and knowledge to kickstart your career in this critical field.
Advanced Network Security Concepts
Comprehensive exploration of advanced network security, covering VPNs, PKI, cloud threats, SDN, and automation. Prepares for various cybersecurity certifications with practical examples and hands-on training.
Nintendo DSi Hacking: Extracting Boot ROMs and New Jailbreak Methods - 37C3 2023
Exploración profunda del hackeo de Nintendo DSi: extracción de boot ROMs, nuevos jailbreaks y revivir consolas con chips NAND desgastados. Análisis técnico de explotación, inyección de fallos y criptografía.
Improving Collaboration and Reducing Risk in Security Operations - Part 2
Explore strategies for enhancing IT-business collaboration and risk management in organizations of all sizes, with insights from security leaders on SOC challenges and solutions.
Writing Secure Software - Applying Security Principles in Practice
Practical application of security principles in web app development, showcasing architectural decisions for enhanced security using a blog as an example.

SMTP Smuggling: A Novel Technique for Email Spoofing
Explore SMTP smuggling, a novel e-mail spoofing technique that exploits protocol interpretation vulnerabilities, allowing unauthorized sending from trusted domains while bypassing security checks.
A Beginner's Guide to Code Review
Learn essential code review techniques to identify vulnerabilities, practice with labs, and discover resources for finding code to review. Improve your skills in detecting and fixing security issues.
Productivity Monitoring, Surveillance, Automation, and Big Tech Harms in Trucking Industry
Explore how truck drivers combat technological surveillance, automation, and industry challenges, focusing on empowering female drivers and addressing Big Tech's impact on the workforce.
When to Report a Bug - Best Practices for Bug Bounty Hunters
Learn essential steps to take after discovering a bug, ensuring proper verification and documentation before submitting an official report. Maximize your bug bounty success with expert guidance.
Implicit and Mutation-Based Serialization Vulnerabilities in .NET
Explores novel .NET serialization attacks bypassing current mitigations, demonstrating vulnerabilities in popular platforms and offering detection and mitigation techniques for developers.
Investigating Hackers - Stories from Norway's National Cybercrime Center
Insights from police cybercrime investigators on forensic challenges and custom code solutions for extracting crucial data when standard tools fall short.
DevSecOps Insights and Exciting Horizons
Explore DevSecOps trends and future strategies with RSAC 2024 Program Committee members, discussing standout sessions and emerging cybersecurity approaches.
Why Railway Is Safe But Not Secure - Security of Railway Communication Protocols
Exploring railway communication protocols' security challenges, highlighting the contrast between safety and security in rail systems and discussing vulnerabilities in GSM-R, RaSTA, and ETCS/ERMTS.
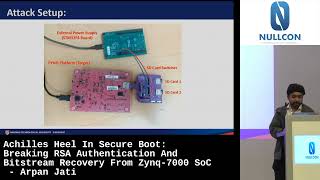
Breaking RSA Authentication and Bitstream Recovery From Zynq-7000 SoC
Uncovers critical vulnerability in Zynq-7000 SoC's secure boot, allowing RSA authentication bypass. Explores implications for embedded device security and trusted computing.
Automating Security Monitoring
Explore efficient security monitoring through automation techniques to handle increasing data volumes, complex architectures, and sophisticated threats while reducing alert fatigue.
The Hidden Risk in Undocumented API Behavior
Explore undocumented Win32 API risks affecting AV and EDR vendors. Learn how overlooked behaviors can lead to security vulnerabilities and gain insights on mitigating these hidden threats.