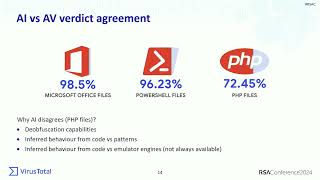
How AI Is Changing the Malware Landscape
Explore AI's impact on malware detection, including insights from VirusTotal's AI engines, strengths and weaknesses in analysis, and emerging AI-evasion techniques in cybersecurity.
How Sworn Enemies Found a Truce to Achieve NIST Compliance
Explore a startup's journey to NIST compliance, focusing on aligning cyber and engineering teams, translating security controls, and achieving third-party attestation in the SaaS industry.
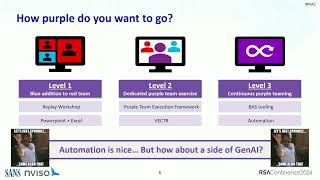
The Always-On Purple Team: Automated CI/CD for Detection Engineering
Innovative architecture for automated detection engineering CI/CD pipeline, merging SOC technologies, SIEM/XDR, SOAR, BAS, and ChatGPT. Includes live demo of creating, testing, and deploying detection analytics.
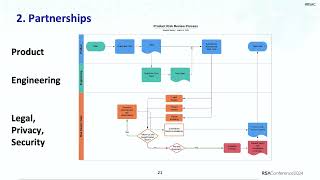
Headspace's Privacy Operations Center and Vault Architecture
Explore Headspace's innovative approach to scaling privacy programs, including their Privacy Operations Center and patented Vault architecture for global mental healthcare services.
Creating an AI Security and Incident Response Team
Learn to establish and operate an AI Security and Incident Response Team (AISIRT) to address AI/ML system issues, detect problems, and differentiate between various threats.
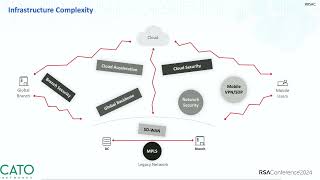
The Price is Wrong - An Analysis of Security Complexity
Explore how security complexity impacts data breaches, analyzing real-world attacks and organizational blind spots through extensive research on network flows and visibility limitations.
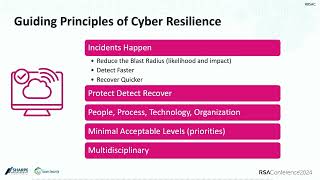
Building Your Roadmap to Cyber Resilience - Five Things You Can Do Today
Learn proven strategies to develop a cyber resilience roadmap, demonstrate progress, and guide investments. Gain insights on maturity models and practical steps for enhancing organizational security.
Leveraging macOS Networking Frameworks for Heuristic Malware Detection
Explore open-source methods for building network state enumerators and advanced monitors on macOS to detect sophisticated malware through unauthorized network access detection.
CISOs Under Indictment - Case Studies, Lessons Learned, and Future Implications
Explore CISO legal risks, indictment stories, and industry shifts through expert interviews. Gain insights on evolving responsibilities and the changing legal landscape for cybersecurity leaders.
AppSec Tool Selection, Procurement, and Implementation Walkthrough
Comprehensive guide to selecting, procuring, and implementing Application Security tools in the SSDLC, offering strategies for successful integration and follow-through.
Hiding in Plain Sight - Hunting Volt Typhoon Cyber Actors
Explore Chinese cyber actors' tactics and defense strategies with experts from FBI, NSA, CISA, and Microsoft. Learn to identify and protect against Volt Typhoon's stealthy network infiltrations.
Your Cybersecurity Budget - Optimizing Risk and Resource Allocation
Explore how historical influences impact cybersecurity budgeting. Learn to apply machine learning and mathematical concepts to optimize risk and design effective programs with limited resources.
Strengthening the Industrial Ecosystem: Free OT Cybersecurity Resources
Discover free OT cybersecurity resources to mitigate risks in industrial environments, addressing financial and expertise gaps for small/medium organizations.
Modern WAF Bypass Techniques on Large Attack Surfaces
Explore advanced WAF bypass techniques for large attack surfaces with insights from top security researcher Shubham Shah, focusing on complex vulnerabilities and security automation.
Day in the Life of an Ethical Hacker and Penetration Tester
Explore the daily routine of an ethical hacker, uncovering the exciting and challenging aspects of penetration testing. Gain insights into this dynamic cybersecurity career path.
GUAC 101 - Introduction to Graph for Understanding Artifact Composition
Explore GUAC, a tool for generating software bills of materials (SBOMs) and vulnerability scanning in cloud-native environments, enhancing security and compliance.
Vulnerable to Vigilant - Social Engineering in the Digital Age
Explore social engineering threats and learn practical strategies to enhance your online security with insights from a young cybersecurity expert.
Detection Engineering without Alert Fatigue - Correlating Minor Detections
Explore innovative approaches to balance detection coverage and alert fatigue in SOC operations, leveraging custom platforms and indicator correlation for effective threat hunting and investigation assistance.
Eliminating Vulnerabilities with Memory Safe Languages
Explore how memory-safe languages can enhance software security by eliminating common vulnerabilities, improving reliability, and reducing potential attack vectors in cloud-native applications.
Optimizing the Bugcrowd Platform for Hardware and IoT Hacking
Expert hacker Brandon Reynolds demonstrates optimizing the Bugcrowd Platform for hardware and IoT security testing, offering insights for both novice and experienced bug bounty hunters.
Mapping CI/CD Attack Surfaces - Strategies and Insights
Explore CI/CD attack surface mapping with insights on problem areas, blind spots, and actionable strategies. Learn about future advancements in reducing vulnerabilities in CI/CD ecosystems.