From an OSS-Fuzz Report to LKML Patch Submission - A Hands-on Journey
Hands-on guide to fixing vulnerabilities using OSS-Fuzz reports, from debugging to submitting patches to the Linux Kernel Mailing List. Learn to contribute to open source projects and improve software quality.
Beyond Guidelines - Designing and Implementing Robust Build Pipelines
Learn to design and implement secure build pipelines beyond standard guidelines. Explore practical tools and methods to enhance supply chain security and protect against rising attacks.
The 'S' in IoT Stands for Security - Securing Connected Devices
Explore IoT security challenges, recent breaches, and how containerization can enhance device protection. Learn best practices for building secure IoT devices and managing their lifecycle.

Securing TPM Secrets with TXT and Kernel Signatures
Explore securing TPM2 NVRAM data using Intel TXT and tboot extensions for kernel signature verification, enhancing protection while maintaining usability during kernel updates.

Writing Viruses for Fun, Not Profit
Explore virus creation techniques, including self-replication and obfuscation, to understand how they evade detection and infect systems. Learn to anticipate vulnerabilities and strengthen application security.
Curtail Coercive Control Using Open Source Applications and Services
Explore strategies to combat technology-enabled coercive control using open-source solutions. Learn design principles, privacy considerations, and challenges in addressing digital abuse.
Why Is There No Free Software Vulnerability Database?
Explore the need for a free software vulnerability database, its challenges, and potential solutions. Learn about Package URL, data models, and future plans for improved cybersecurity.
Everything-as-Code: Pushing the Boundaries of SAST
Explore the evolution of SAST in the "everything as code" era, examining challenges in analyzing infrastructure, contracts, and circuits, with focus on Bicep and Solidity languages.
Infostealer Malware - Understanding the Threat and Impact
Explore the dangers of infostealer malware and learn effective defense strategies. Gain insights into its mechanisms, potential impacts, and ways to protect your digital assets.
Zero Trust Threat Modeling - Implications for Application Security
Explore zero trust's impact on application security and threat modeling. Learn new design principles, threats, and approaches for effective zero trust threat modeling in modern environments.
Scaling Content Security Policy: Enterprise Compliance and Third-Party Resource Management
Learn to implement Content Security Policy and monitor web resources at scale, addressing supply chain attacks and PCI requirements for enhanced frontend security in enterprise applications.
Open Software Supply Chain Attack Reference (OSC&R) - OWASP Foundation
Explore the OSC&R framework for software supply chain security, analyzing real-world attacks and improving DevSecOps programs to enhance overall security posture.
Reversing Robots and Bypassing Security: Hacking Vacuum and Lawn Robots
Explore reverse engineering and security vulnerabilities in Ecovacs robots, uncovering potential privacy risks and methods to gain root access for custom software implementation.
Enterprise Ready Workshop - Automate with No-Code Okta Workflows
Automate customer-specific reporting for SaaS apps using Okta Workflows. Learn to enhance identity maturity and streamline enterprise systems through no-code automation techniques.
IoT Hacking 101 - Reverse Engineering the Xiaomi Ecosystem
Explore IoT hacking and reverse engineering techniques focused on the Xiaomi ecosystem, covering hardware methods, ecosystem analysis, and key findings in cybersecurity.

The Human Element in Cybercrime and Cybersecurity
Explore the human factor in cybersecurity through encounters with hackers and pentesters. Learn why understanding attacker motivations is crucial for developing effective defenses beyond usable security.
Rough Seas and Ships in Storms - A 2023 Retrospective from an MSSP Perspective
Cybersecurity expert reviews 2023 challenges for Managed Security Service Providers, offering insights on navigating threats and protecting organizations in an evolving digital landscape.
Attacking Developer Environments Through Drive-by Localhost Attacks
Explore drive-by localhost attacks on developer environments, uncovering vulnerabilities and defense strategies in this cybersecurity presentation from DefCamp 2023.
Using RPA for Fast, Reliable and Repeatable Incident Response
Explore how Robotic Process Automation enhances incident response in cybersecurity, offering speed, reliability, and repeatability for improved threat management and operational efficiency.
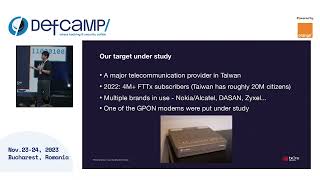
Backdooring 4 Million Modems with 6 Bugs in a Week - Cybersecurity Case Study
Explore how a researcher exploited vulnerabilities to potentially compromise millions of modems, highlighting the critical importance of cybersecurity in telecommunications infrastructure.
Finding Vulnerabilities in Your Codebase Using Open Source Tools
Explore open-source tools for identifying vulnerabilities in your codebase. Learn effective techniques to enhance software security and protect against potential threats.