Advancements in JavaScript Engine Fuzzing - OffensiveCon 2023
Explore advancements in JavaScript engine fuzzing, covering techniques like splicing, code coverage, and hybrid engines to enhance bug discovery and security testing.
New Phones, Software and Chips - New Bugs?
Explore cutting-edge vulnerabilities in modern smartphones, examining software and hardware innovations that introduce new security challenges.
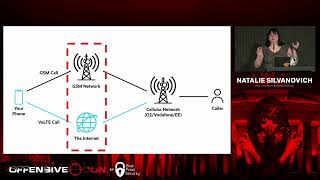
How to Hack Shannon Baseband from a Phone
Explore techniques for hacking Shannon baseband from a phone, uncovering vulnerabilities and potential exploits in mobile communication systems.
ASN.1 and Done: A Journey of Exploiting ASN.1 Parsers in the Baseband
Explore ASN.1 parser vulnerabilities in cellular baseband, uncovering security risks and exploitation techniques in mobile communication systems.
Abusing Linux In-Kernel SMB Server to Gain Kernel Remote Code Execution
Explore Linux kernel vulnerabilities and gain insights into exploiting the in-kernel SMB server for remote code execution.
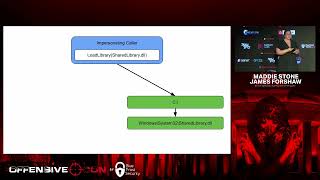
The Print Spooler Bug that Wasn't in the Print Spooler
Explore a unique Windows vulnerability discovery, from initial bug report to full exploit chain, with insights on Microsoft's patch process and security implications.
Embedded Threats: A Deep Dive into the Attack Surface and Security Implications of eSIM Technology
Explore the attack surface and security implications of eSIM technology through a comprehensive deep dive into embedded threats.
Securing Content Distribution with RSTUF, an Incubating OpenSSF Project
Explore RSTUF, an OpenSSF project for securing content distribution. Learn about its implementation, adoption by PyPI and RubyGens, and use in private repositories and Archivista for in-toto attestation storage.
Web Developer Security: Best Practices and Beyond
Explore latest web security developments, technologies, and best practices for developers, including insights from recent workshops and W3C initiatives.
The Current State of Open Source Security Compliance Tooling Is Well, Sad
Explore practical approaches to improve software supply chain security using OpenSSF projects, open source tools, and open data for automated compliance and robust processes.
German National Guideline on SOSS-Lifecycle: Community Outreach
Explore Germany's guideline for secure open source software development lifecycle and provide input on challenges, goals, and ideas for enhancing security without burdening the community.
Managing Vulnerabilities in Open-Source Dependencies
Learn strategies to secure open-source dependencies, evaluate software composition analysis tools, and shift from reactive to proactive security postures in product development.
Automated End-to-End VEX Streams You Can Trust
Explore automated VEX streams for trusted vulnerability communication. Learn to build end-to-end systems using OpenVEX, enhancing software security without human intervention.
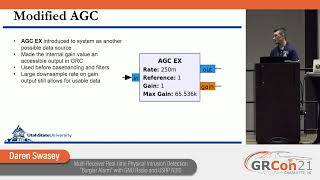
Multi-Receiver Real-time Physical Intrusion Detection "Burglar Alarm" with GNU Radio and USRP N310
Explore real-time indoor intrusion detection using Wi-Fi signals and GNU Radio. Learn about leveraging internal radio receiver signals for physical channel monitoring and system implementation.

How to Implement Keycloak Authentication in React
Implement Keycloak authentication in React applications for enhanced security and access management in web-based projects.
CVEs are Alive, but Do Not Panic! - Kernel Security Update 2024
Explore the world of CVEs in kernel security, understanding their impact and learning how to approach them without unnecessary alarm.

Securing Web Applications: Integrating OWASP with Burp Suite
Integrate OWASP tools with Burp Suite to identify vulnerabilities, conduct security assessments, and implement effective mitigation strategies for web applications.
Securing Digital Frontiers: Leveraging Keycloak for Comprehensive Application Security
Explore Red Hat's Keycloak for robust identity and access management in diverse deployment environments, ensuring application security and mitigating financial risks.
Increase Security Posture in Software Delivery with Red Hat Trusted Software Supply Chain
Enhance software security with Red Hat's Trusted Supply Chain: protect components, predict vulnerabilities, and improve resilience through advanced tools and practices.
Hunting Down the Monsters Hidden in Your Software Supply Chain
Uncover and mitigate hidden threats in your software supply chain. Learn effective strategies to enhance security and protect against vulnerabilities.
Secure Your App: DevSecOps Trusted Application Supply Chain
Explore DevSecOps principles and implement a trusted application supply chain to enhance app security and streamline development processes.