NVMe: New Vulnerabilities Made Easy - Exploiting Cloud Storage Protocols
Exploring pre-auth remote vulnerabilities in NVMe implementation, emphasizing the importance of SCA tools in production pipelines and showcasing discoveries in Linux kernel and NVIDIA.
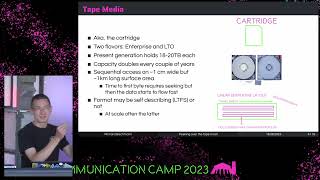
Peeking Over the Tape Moat - Magnetic Tape Storage Security
Explore magnetic tape storage as a defense against ransomware, its unique properties, and potential vulnerabilities. Learn about data center usage and security considerations from an operator's perspective.
Scarlet OT: Adversary Emulation for Industrial Control Systems - HITB 2023
Explore Scarlet OT, an open-source tool for ICS security testing. Learn about OT adversary emulation, protocol support, and real-world applications in industrial environments.

A Deep Dive Into Maritime Cybersecurity
Explore maritime cybersecurity challenges, threats, and solutions in this comprehensive analysis of the shipping industry's digital vulnerabilities and defense strategies.
Using Apple Sysdiagnose for Mobile Forensics and Integrity Checks - Hack.lu 2023
Explore Apple Sysdiagnose's potential in mobile forensics and integrity checks, uncovering valuable insights for digital investigations and device analysis.
The Rise of Malicious MSIX Files
Explore the emerging threat of malicious MSIX files, their impact on cybersecurity, and strategies for detection and prevention in this insightful conference presentation.
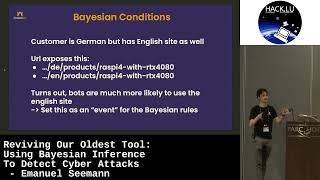
Using Bayesian Inference to Detect Cyber Attacks
Explore Bayesian inference techniques for detecting cyber attacks, enhancing your ability to identify and respond to security threats in real-time.
Open Wounds: The Last 5 Years Have Left Bluetooth to Bleed
Explore critical Bluetooth vulnerabilities from the past 5 years, their impact on device security, and potential mitigation strategies in this eye-opening cybersecurity analysis.
Raiders of the Lost Arts - Cybersecurity Techniques and Strategies
Explore cutting-edge cybersecurity techniques and strategies in this talk by Stefan Hager, focusing on rediscovering and applying forgotten or underutilized security methods.
Permissionless Universal Overlays - Hack.lu 2023
Explore permissionless universal overlays in blockchain technology, focusing on their potential applications and impact on decentralized systems.

Are The Lessons on Security Incident and Vulnerability Management Learned?
Explore lessons learned in security incident and vulnerability management, examining current practices and potential improvements in cybersecurity strategies.
Analyzing Cellular Basebands with FirmWire
Explore FirmWire, an open-source platform for analyzing cellular basebands. Learn about baseband vulnerabilities, emulation techniques, and how to uncover security flaws in LTE and GSM stacks.
Ethical Hacking: Good Intentions and Questionable Outcomes
Explore ethical boundaries in security testing, from fuzzing servers to buying dark web credentials. Discuss grey areas and the need for beneficial practices that maintain moral high ground.
Weaponizing Technology: Examining the Importance of Privacy in an Era of Digital Surveillance
Exploring the impact of digital surveillance on privacy and reproductive rights post-Dobbs, emphasizing the vulnerability of marginalized communities and the need for protective measures.
Youth Understandings of Online Privacy and Security - A Dyadic Study of Children and Parents
Explores youth and parent perspectives on online privacy and security, revealing insights into children's knowledge and parental influence methods for safer internet practices.
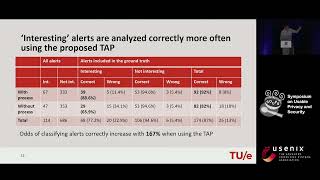
Synthesis and Evaluation of a Network Threat Analysis Process for Tier 1 SOC Investigations
Evaluation of a structured 4-stage threat analysis process for SOC tier-1 analysts, showing improved accuracy and discussing implications for security operations.
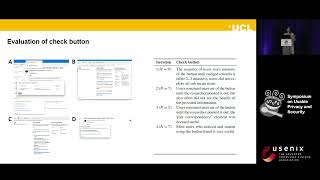
Evaluating Email User Security Tools: Checking, Nudging, and Scoring - SOUPS 2023
Evaluates three e-mail security tools to improve phishing detection, finding "suspicion score" nudge and "check" button most effective for professional users without hindering productivity.
Fight Fire with Fire: Hacktivists' Take on Social Media Misinformation
Explore hacktivists' perspectives on combating social media misinformation through interviews, revealing strategies like deplatforming, doxing, and promoting information literacy.
How People in 10 Countries Expect AI to Affect Privacy - SOUPS 2023
Explores global perceptions of AI's impact on privacy, revealing concerns about data vulnerability, personal inference, consent issues, and surveillance across 10 countries.
AI and Data Security Innovation Showcase
Experts discuss risks and benefits of generative AI in companies, focusing on compliance, privacy, and security. Includes presentations from emerging AI and data security firms.
Threat Model Report: Security Considerations for Hardening Declarative GitOps on Kubernetes with Argo CD
Explore security considerations for hardening Argo CD deployments in Kubernetes, focusing on mitigating misconfigurations and implementing best practices to enhance GitOps workflows.