OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.
The Rise of SaaS-Targeted Malware - Zeus Variant Attacking Salesforce Users
Demonstration of a new Zeus malware variant targeting Salesforce users, showcasing its stealthy data exfiltration capabilities and discussing implications for SaaS security.
OWASP Media Project: Functionality and Implementation
Explore OWASP Media platform's functionality, tools, and framework integration. Learn content creation tips and team management strategies to support OWASP's mission.
New Frameworks, Old Problems: Web Security Challenges in Modern Development
Exploring security challenges in modern web frameworks like Play! and Node.js, comparing solutions from established frameworks, and offering practical code examples to address common vulnerabilities.
Android and iPhone Risks and Solutions
Explore mobile security risks and effective solutions for Android and iPhone devices, enhancing your understanding of smartphone vulnerabilities and protection strategies.
Privacy vs Security Intricacies - Balancing Expectations and Realities
Explore the complex relationship between privacy and security, examining their definitions, societal impacts, and technological implications in the digital age.

Content Security Policy (CSP) - Understanding and Implementing Web Protection
Learn about Content Security Policy (CSP), a powerful browser security feature that mitigates cross-site scripting attacks. Discover its benefits, implementation strategies, and future impact on web security.
Application Security at DevOps Speed and Portfolio Scale
Explore a revolutionary approach to application security using passive sensors for real-time visibility across an organization's portfolio, enabling proactive collaboration and value generation.
Attack-Driven Defense: Countering Real-World Attack Behaviors
Explore new network defense techniques from an attacker's perspective, focusing on detecting initial compromise, persistence, and lateral movement. Learn practical methods for effective alerting and traffic analysis.
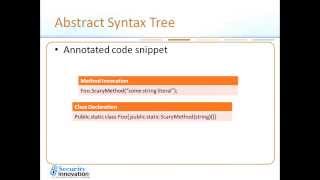
Adventures in Reviewing Mountains of Code
Explore strategies for efficiently reviewing large codebases, including experiments, tools, and unexpected challenges encountered during a 2.6 million line code assessment.
Seven Deadly Sins of Mobile Application Development - Unlocking Mobile Hacking Vulnerabilities
Unlock mobile app security secrets: Learn common development mistakes, session management vulnerabilities, and best practices to protect against attacks and impersonation.
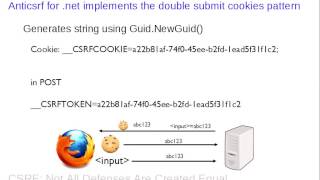
CSRF Defense Strategies - Not All Are Created Equal
Explore CSRF vulnerabilities, defense mechanisms, and their implementations. Learn about synchronizer token patterns, double submit cookies, and challenge-response systems for effective protection against CSRF attacks.
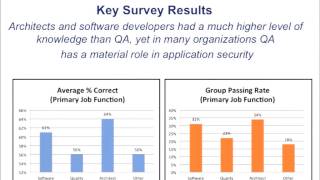
Can AppSec Training Really Make Developers Security-Smart?
Explore the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and practical application in software security programs.
DIY Command and Control for Fun and No Profit
Hands-on exploration of Command & Control botnets, providing insight into cybercriminal operations. Includes live malware demonstration for a realistic glimpse into this dark corner of the internet.
The Cavalry Is Us - Cybersecurity Activism in the Internet of Things Era
Exploring cybersecurity challenges in IoT and the need for collective action. Calls for researchers and professionals to shape the future of digital security and address emerging threats.
Surviving an Application DoS - Strategies and Open Source Defense Framework
Explore strategies to defend against Application-Level DoS attacks using a new open-source Node.js framework. Learn to identify threats, analyze traffic patterns, and implement active defense measures.
Libinjection: From SQLi to XSS Detection - New Algorithm Introduction
Explore advanced techniques for detecting SQLi and XSS attacks using libinjection, a fast and accurate algorithm. Learn about its implementation, benefits, and future developments in web security.
Next Generation Red Teaming - Integrating Application-Centric Attacks
Explore advanced red teaming techniques integrating application-specific attack surfaces for more realistic and effective security assessments across multiple domains.
Intelligence-Led Cybersecurity - Balancing Global Operations, Risk, and Speed
Experts discuss global cybersecurity challenges, balancing risk and speed in intelligence-led operations, and the interplay between public and private sectors in addressing cyber threats.
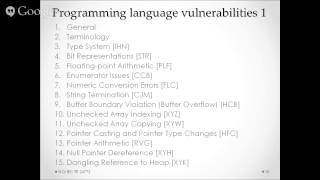
Guidance on Avoiding Programming Language Vulnerabilities - TR24772 Explanation
Overview of ISO/IEC TR 24772:2010, guiding programmers on avoiding vulnerabilities through language selection and use. Insights from a contributor on enhancing software security.
The Perilous Future of Browser Security
Explore browser security challenges, tradeoffs, and solutions. Learn about critical vulnerabilities, secure browser design, and balancing security with user experience in the face of evolving threats.