OWASP SEDATED - Preventing Sensitive Data Disclosure in GitHub Commits
Prevent sensitive data leaks to GitHub with SEDATED, an analyzer that catches and blocks commits containing user credentials or tokens before they're pushed.
Can Our Democracy Survive the Internet? - Challenges and Solutions
Exploring the Internet's impact on democracy, polarization, and information warfare, with insights on combating disinformation and adapting to evolving digital challenges.
OWASP Glue Tool: Security Automation Made Easier
Learn about OWASP Glue Tool, a Ruby gem for security automation that coordinates multiple analysis tools and generates reports, simplifying the process of integrating security into development workflows.
OWASP Amass Project: DNS Enumeration and Network Mapping
Explore DNS enumeration and network mapping with OWASP Amass, a powerful tool for uncovering organizational internet presence and exposure using multiple data sources.
Defensible Application Security for the Artificial Intelligence Era
Exploring trust in the digital world, neuroscience insights, and the impact of AI on application security. Discusses designing scalable, real-time controls to combat intelligent adversaries in the AI era.
OWASP Leaders Workshop - Future Directions and Operational Strategies - Part 2
Explore OWASP leadership strategies, event planning, and community engagement. Learn about future directions, project connections, and operational improvements to enhance local chapters and global initiatives.
(In)Security is Eating the World - Speed and Autonomy for Defense
Explore the future of cybersecurity with Michael Coates as he discusses the need for automation, scale, and speed in addressing critical security failures in our technology-driven world.
WAF Bypass Techniques Using HTTP Standard and Web Servers' Behavior
Explore creative techniques to bypass web application firewalls using HTTP standards and server behaviors. Learn to smuggle and reshape requests for penetration testing and bug bounty hunting.
Building a Security Culture - Digital Transformation and Breach Prevention
Explore strategies for creating a robust security culture amid digital transformation, addressing cloud risks, BYOD challenges, and persistent breaches despite technological investments.
The Bug Hunter's Methodology 2.0 - Advanced Web Application Security Testing
Explore cutting-edge techniques and tools for discovering vulnerabilities in web applications, including XSS, SSTI, SSRF, code injection, and more. Learn from expert Jason Haddix's updated methodology for effective penetration testing.
Robots with Pentest Recipes - Automating Security Testing in DevOps
Explore automated security testing using Robot Framework to integrate tools like OWASP ZAP and Nmap. Learn to create easy-to-write test recipes for continuous delivery pipelines, enabling cross-team collaboration in application security.
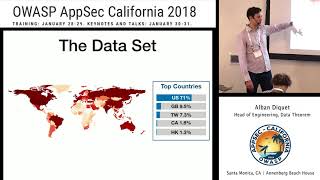
SSL Traffic Interception on Mobile Devices - Analysis and Protection
Análisis detallado de incidentes SSL en aplicaciones móviles, revelando patrones globales, casos notables y soluciones para desarrolladores contra la interceptación de tráfico.
Hard to Port - A Snapshot of the Vulnerability Landscape in 2015
Explore the 2015 vulnerability landscape through anonymized data, discussing trends, challenges, and the shift towards continuous application security and risk management.
Visualizing Security via LANGSEC
Explore LANGSEC as an alternative to pattern matching in web security. Learn about lexers, tokenizers, and parsers, and discover how to implement LANGSEC for analyzing and preventing security attacks.
Software Security Metrics - Developing Key Indicators for Executives
Techniques for effective communication with executives about software security, focusing on developing meaningful metrics to demonstrate progress and maturity in security capabilities.

Integrating Mobile Devices into Penetration Testing Programs
Explore techniques for assessing mobile device security risks in enterprise environments, including phishing, undermining controls, and using compromised devices as pivot points.
Radio Hacking - Cars, Hardware, and More
Explore radio hacking techniques for wirelessly controlled devices like gates, garages, and cars. Learn about tools, vulnerabilities, and protective measures in this comprehensive introduction to RF security.
Attack Tree Vignettes for Containers as a Service Applications - Risk-Centric Threat Modeling
Explore attack tree vignettes and risk-centric threat models for Containers as a Service applications, focusing on security challenges in cloud adoption and containerization.
HTTPS Everywhere: Improving Web Security and Usability
Exploring Chrome's efforts to enhance HTTPS adoption: tools for debugging, reporting mechanisms for safe rollout, and strategies to improve web security.
Design Approaches for Security Automation
Explore criteria for designing and evaluating security automation tools, including build vs. buy decisions, deployment strategies, and effective implementation for organizational needs.
ClickOnce Exploitation: One-Click Network Foothold - AppSec California 2016
Explore ClickOnce deployment vulnerabilities and learn a new methodology for establishing network footholds through minimal user interaction and phishing techniques.