OWASP Coraza: The Way to WAF in 2023
Explore OWASP Coraza, a cutting-edge Web Application Firewall (WAF) solution, and learn how it enhances web security in 2023 through advanced features and implementation strategies.
Incorporating Software Assurance with OWASP SAMM V2.1
Enhance software assurance practices using OWASP SAMM V2.1, a comprehensive framework for implementing and measuring security activities throughout the development lifecycle.
Supply Chain Security with Dependency Track
Explore supply chain security using Dependency Track with experts Anandan, Bhargava, and Duster. Learn strategies to mitigate risks and enhance software security in this informative session.
Shifting Security Everywhere
Explore strategies for integrating security throughout the software development lifecycle, emphasizing proactive measures and collaboration between development and security teams.
Reducing Permissions Management Time While Protecting Users
Learn strategies to streamline permissions management, enhance user protection, and optimize security processes in application development.
Threat Modeling In and For Your Organization
Comprehensive guide to implementing threat modeling practices within organizations, enhancing security strategies and fostering a proactive approach to identifying potential vulnerabilities.
Is the U.S. Losing the Cyber Battle?
Explore the current state of cybersecurity in the U.S., examining potential vulnerabilities, threats, and strategies to enhance digital defense capabilities.
A Weakness in Chrome and a New Hacking Technique
Explore a critical Chrome vulnerability and innovative hacking method presented by security experts. Gain insights into cutting-edge web security threats and defense strategies.
Developer Driven Security in High-Growth Environments
Explore strategies for implementing developer-driven security practices in rapidly expanding tech environments, focusing on scalable and efficient approaches.
How to Have Visibility and Security of a CI/CD Pipeline
Discover strategies for enhancing visibility and security in CI/CD pipelines, focusing on best practices and tools to safeguard your software development lifecycle.
Overcoming the Inundation of Noisy Security Alerts
Learn strategies to manage and prioritize security alerts effectively, reducing noise and focusing on critical vulnerabilities in application security.
The Power of DevSecOps in Web3 and Blockchain
Explore DevSecOps principles in Web3 and blockchain, focusing on security integration for decentralized applications and smart contracts development.

Hacking and Defending APIs - Red and Blue Make Purple
Learn techniques for both attacking and defending APIs, combining offensive and defensive security perspectives to enhance overall API protection.
Vulnerabilities as Ingredients and OWASP Top 10 as Seasoning
Explore how vulnerabilities and OWASP Top 10 interact in application security, using a culinary analogy to demystify complex concepts and enhance understanding of secure development practices.
Docker for Pentesters
Learn essential Docker techniques for penetration testing, enhancing your cybersecurity skills and improving your ability to identify vulnerabilities in containerized environments.
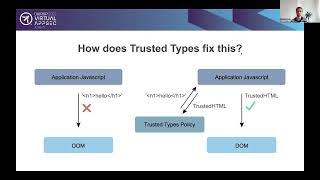
Trusted Types: A World Without XSS
Explore cutting-edge web security with Trusted Types, a powerful defense against XSS attacks. Learn implementation strategies and best practices from industry experts.
OWASP WrongSecrets - We Have a Secret for Everyone
Explore common pitfalls in secret management and learn best practices for securing sensitive information in various environments, from local setups to cloud deployments.
Layered Threat Modeling: An Architectural Approach
Explore architectural threat modeling techniques to identify and mitigate security risks in complex systems, enhancing overall application and infrastructure protection.
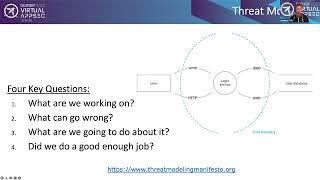
Shift Left Security with the Security Test Pyramid
Explore the concept of shifting security testing left in the development process using the Security Test Pyramid, enhancing software security from the early stages.
Landmines in the API Landscape
Explore potential security vulnerabilities in API development and learn strategies to mitigate risks in this insightful talk by a cybersecurity expert.
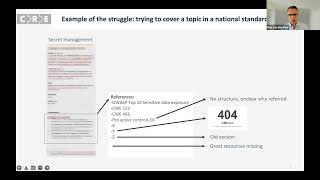
Understanding the Complete Chain of Application Security Using OpenCRE.org
Explore a comprehensive approach to application security using openCRE.org, covering key concepts and best practices for robust software protection.