The Evolution of Hackers for Charity
Explore the evolution of Hacking for Charity (HFC) and its impact on using technology for social good, as presented by Johnny Long at Derbycon 2012.
Building the Next Generation IDS with OSINT
Explore innovative techniques for enhancing intrusion detection systems using open-source intelligence, improving network security and threat detection capabilities.
Pwned in 60 Seconds - From Network Guest to Windows Domain Admin
Discover rapid network exploitation techniques to escalate from guest access to Windows Domain Admin in under a minute, with insights from a cybersecurity expert.
Introducing the Smartphone Pentest Framework
Explore the Smartphone Pentest Framework, a cutting-edge tool for mobile security testing, and learn how to assess vulnerabilities in smartphone applications and networks.
Application Security Testing and SDLC for Developers
Learn app security testing techniques and tools for the software development lifecycle, including reconnaissance, mapping, vulnerability assessment, and exploitation.
InfoSec Stress and Community - Managing Challenges in Information Security
Explore the impact of stress on InfoSec professionals and the importance of community support in managing challenges within the cybersecurity industry.
Data Hiding in Your Application - Securing Sensitive Information
Learn techniques for concealing sensitive data in applications, including garbage collection, marshalling, and the "Secret Highway" method. Explore practical examples and solutions.
Grey Hats and Bug Bounties
Explore ethical hacking, bug bounty programs, and the role of grey hat hackers in improving cybersecurity. Learn about responsible disclosure and the benefits of participating in vulnerability research.
Wielding Katana - A Live Security Suite
Explore Katana, a live security suite, with experts JP Dunning and Chris Silvers as they demonstrate its capabilities and applications in real-time.
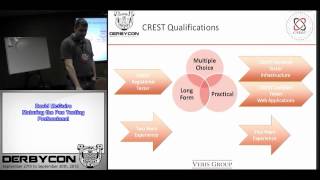
Maturing the Pen Testing Professional - Challenges and Solutions
Explore the evolution of penetration testing, its challenges, and future directions. Learn about industry standards, methodologies, and qualifications to enhance your professional skills in cybersecurity.
Windows Command Line Incident Response - Outerz0ne 2011
Explore Windows command line tools for effective incident response, enhancing your ability to investigate and mitigate security breaches efficiently.
Search and Seizure in the US - Constitutional Rights and Legal Precedents - Part 1
Explore constitutional rights, search and seizure laws, and privacy issues in the digital age. Learn about recent legal cases and their implications for personal freedoms and technology.
Irongeek Outerz0ne and Notacon 2009 Conference Highlights
Explore hacking techniques and cybersecurity insights from the Outerz0ne and Notacon 2009 conferences, featuring expert presentations and demonstrations.

Filter Evasion Techniques - Houdini on the Wire
Explore advanced techniques for bypassing network filters and evading detection, enhancing your understanding of network security and penetration testing methodologies.
Embedded Malicious JavaScript - Outerz0ne 2009
Explore techniques for embedding malicious JavaScript in web applications, understanding potential vulnerabilities and security risks in modern web development.
Anti-Forensics: Occult Computing Class
Learn techniques to conceal digital activities, including data hiding, encryption, and steganography. Explore methods for thwarting forensic investigations and protecting privacy in the digital realm.
Password Exploitation Techniques - Class 1
Learn techniques for password exploitation, including cracking methods and security vulnerabilities, from expert speakers in this comprehensive cybersecurity session.
Password Exploitation Techniques - Class 2
Learn advanced techniques for password exploitation, including cracking methods and security measures, from industry experts in this comprehensive cybersecurity session.
OSInt, Cyberstalking, Footprinting and Recon: Getting to Know You - Part 3 Metadata and Miscellaneous Topics
Explore metadata, file formats, and EXIF information for effective digital footprinting and reconnaissance. Learn practical tools and techniques for gathering valuable intelligence.
Pen-Testing Practice in a Box: Assembling a Virtual Network
Learn to set up a virtual network for penetration testing practice, covering VirtualBox installation, VM configuration, networking options, and installing essential tools and environments.
Why Your Password Policy Sucks - Improving Security Through Better Practices
Explore password policy flaws, real-world examples, and advanced cracking techniques. Learn to leverage this knowledge for better security practices and solutions.