Legal Privacy Trends from 1984 to 2012 - Lecture 2.2.4
Explore legal privacy trends from 1984 to 2012, examining key developments and their impact on personal data protection and digital rights.
Network Security - It's A Trap
Explore network security vulnerabilities and traps, learning to identify and mitigate potential threats in digital environments.
I'm a Hacker and I'm a QSA - Notacon 9 Presentation
Explore the intersection of hacking and QSA roles, examining ethical considerations and professional responsibilities in information security.
Baking in Security - Lecture 1.2.5
Explore essential security practices for software development, emphasizing the importance of integrating security measures from the start of the development process.
What If Max Zoran Succeeded Living Without Silicon Valley - Notacon 9
Explore living without Silicon Valley tech, examining open-source hardware, reverse engineering, and alternative approaches to technology development. Challenges intellectual property norms and discusses creating fresh hardware solutions.
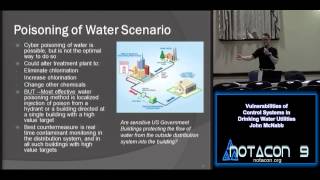
Vulnerabilities of Control Systems in Drinking Water Utilities - Notacon 9
Explore vulnerabilities in drinking water control systems, potential cyber threats, and necessary security measures to protect critical water infrastructure.
Empirical Exploitation in Cybersecurity - HD Moore
Explore empirical exploitation techniques with HD Moore, delving into cutting-edge cybersecurity research and practical applications for identifying vulnerabilities.
How I Learned to Stop Worrying and Love the Smart Meter
Explore smart meter technology, its vulnerabilities, and potential security implications in this insightful presentation on modern energy infrastructure.
Is Lock Sport a Sport? - Exploring Competitive Lock Picking
Explore the world of lock sport, its competitive nature, and ethical considerations in this intriguing discussion on the intersection of security and recreational lock picking.
Mirror Mirror - Reflected PDF Attacks Using SQL Injection
Explore innovative techniques for exploiting SQL injection vulnerabilities to launch reflected PDF attacks, enhancing your understanding of web application security.
Introducing the Smartphone Penetration Testing Framework
Explore smartphone penetration testing with Georgia Weidman's framework, covering vulnerabilities, jailbreaking, and mobile security challenges in the workplace.
Breaking Microsoft Dynamics Great Plains - An Insider's Guide
Insider's guide to exploiting vulnerabilities in Microsoft Dynamics Great Plains, revealing security weaknesses and potential attack vectors in this enterprise resource planning software.
RFID Security Vulnerabilities and Exploits - Lecture 7
Explore RFID technology's vulnerabilities and security implications in this insightful presentation, uncovering potential risks and mitigation strategies.
Ambush - Catching Intruders at Any Point
Learn advanced techniques for detecting and intercepting network intruders using the Ambush system, enhancing your cybersecurity skills and defensive capabilities.
Business Ramifications of the Internet's Unclean Conflicts
Explore business impacts of internet conflicts: data protection, innovation, brand security, policy challenges, and adaptability strategies for modern organizations.
Threat Model Express - Rapid Security Assessment Techniques
Learn efficient threat modeling techniques to identify and mitigate security risks in software development, enhancing your ability to create more secure applications.
Size Does Matter - Password Tools and Data Analysis
Explore password security tools and data analysis techniques to enhance cybersecurity practices and protect sensitive information effectively.
Conference Kickoff and Cybersecurity Challenges - OISF 2012
Explore cybersecurity challenges, from digital doomsday scenarios to overlooked vulnerabilities. Gain insights on user behavior, smart technology risks, and potential economic impacts in this thought-provoking discussion.
Focusing on the Fool - Building an Awareness and Training Program
Discover strategies for creating effective security awareness programs that target human vulnerabilities and foster a culture of cybersecurity within organizations.
Pentesting ASP.NET - Injection and Cross-Site Scripting Attacks
Explore ASP.NET vulnerabilities and security techniques with expert Bill Sempf. Learn about injection, XSS, authentication management, and cryptography to enhance web application security.
Netflow for Incident Response
Learn to leverage Netflow data for effective incident response, enhancing network security and threat detection capabilities.