Hacking JavaScript Desktop Apps with XSS and RCE
Explore techniques for auditing Electron apps, understanding XSS in desktop environments, and exploiting vulnerabilities to achieve remote code execution in JavaScript-based applications.
Building Secure ASP.NET Core MVC Applications
Explore ASP.NET Core MVC security features, including XSS and CSRF protection. Learn to build robust web applications with modular architecture and cross-platform compatibility.
Differences Between Web Application Scanning Tools When Scanning for XSS and SQLi
Investigates differences between web application scanning tools for XSS and SQLi, addressing challenges in modern web architectures and suggesting improvements for effective vulnerability detection.
Client-Side Protection Against DOM-Based XSS Done Right
Comprehensive overview of client-side protection against DOM-based XSS attacks, covering vulnerabilities, prevention techniques, and practical solutions for web security professionals.
#Eko2020 Bounty Hunters | Adrian Pedrazzoli: XSS de -1 a 0
Aprende técnicas básicas para detectar XSS, tipos, recursos necesarios y ejemplos de hallazgos en programas de Bug Bounty. Incluye recomendaciones prácticas para cazadores de recompensas.
Fixing XSS with Content Security Policy
Explore Content Security Policy (CSP) as a defense against XSS attacks, comparing CSP 1.0 and 2.0, and learn implementation strategies for enhanced web application security.
Don't Trust the DOM - Bypassing XSS Mitigations via Script Gadgets
Explores novel XSS attack technique using script gadgets to bypass mitigations, demonstrating vulnerabilities in modern JavaScript libraries and advocating for preventive security measures.
XSS is Dead - We Just Don't Get It
Exploración crítica de la persistencia del XSS, analizando su historia, fracasos en su mitigación y factores que contribuyen a su continuidad. Se cuestiona su relevancia actual y se proponen reflexiones sobre el futuro de la seguridad web.
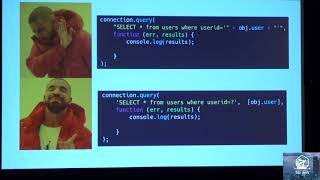
OWASP Top 10 for JavaScript Developers
Explore JavaScript vulnerabilities in OWASP Top 10, covering client and server-side issues with focus on modern frameworks and NodeJS. Learn prevention techniques for secure web development.
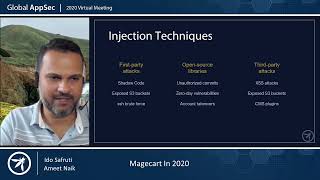
Magecart 2020 - The New Face of XSS
Explore Magecart's evolution, injection techniques, and threat complexity. Learn from real-world case studies and discover strategies to prevent these sophisticated web skimming attacks.
Evaluating the Effectiveness of Content Security Policy in the Wild
Evaluación de la efectividad de la Política de Seguridad de Contenido en la práctica, analizando su adopción, configuración y debilidades frente a ataques XSS.
Defensive Security Research is Sexy Too - Real Sign of Skill
Explore defensive security research's importance, goals, and applications across tech levels. Discover past challenges, current solutions, and future opportunities in this critical field.
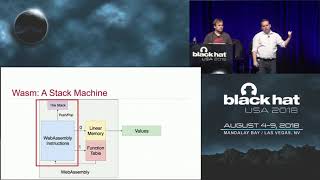
WebAssembly - A New World of Native Exploits on the Browser
Explore WebAssembly's security risks, low-level semantics, and potential vulnerabilities in browser-based applications. Learn about linear memory, function tables, and mitigation strategies.
Breaking XSS Mitigations Via Script Gadgets
Explore a novel web hacking technique that bypasses XSS mitigations using script gadgets. Learn about HTML sanitizers, CSP, and practical demonstrations of this powerful attack method.
HTTP Security Headers You Need To Have On Your Web Apps
Explore essential HTTP security headers to protect web apps from vulnerabilities. Learn implementation techniques and see live demos of their impact on site security.
Cross-Site Escape - Pwning macOS Safari Sandbox the Unusual Way
Explore a novel attack on macOS Safari sandbox using Cross-Site Scripting, achieving native code execution outside the sandbox without re-exploiting WebKit twice.
XSS Mitigation - The State of the Art
Comprehensive overview of XSS attacks and modern defense strategies, covering browser-based, server-side, and framework-specific mitigations for web developers and security professionals.
No More XSS - Deploying CSP with Nonces and Strict-Dynamic
Learn to implement Content Security Policy with nonces and strict-dynamic to prevent XSS attacks. Discover practical deployment strategies for Pinterest and Instapaper, and understand potential vulnerabilities.
Revisiting XSS Sanitization
Explore XSS vulnerabilities in popular WYSIWYG editors and learn an effective sanitization technique using minimal characters and regular expressions to prevent attacks across various contexts.
Session Identifier are for Now, Passwords are Forever - XSS-Based Abuse of Browser Password Managers
Explore XSS-based attacks on browser password managers, their vulnerabilities, and potential solutions. Learn about password field usage on popular websites and get recommendations for protection.
Going Auth The Rails On A Crazy Train
Explore common authentication and authorization pitfalls in Rails applications, and learn about a new dynamic analysis tool for penetration testing and securing large-scale Rails projects.