Hacking - Intro to Cross Site Scripting
Learn about Cross Site Scripting (XSS), its types, and prevention techniques. Understand the risks of this common web vulnerability and how to secure your applications against potential attacks.
Browser Exploitation - Max Zinkus
Explore JavaScript-based browser exploitation techniques, including XSS, JIT compilation vulnerabilities, and shellcode execution. Learn about browser security measures and how to find and chain exploits.
Cross-Site Scripting
Learn about cross-site scripting vulnerabilities, their impact, and suitability for beginner hackers. Gain insights into this common web security flaw and its relevance in bug bounty programs.
Remediating XSS in GitHub Open Source Projects - Lessons Learned
Insights on scaling XSS remediation across GitHub open source projects, focusing on risk reduction, adding security controls, and automating code modification for diverse applications.
New Methods in Automated XSS Detection - Dynamic Testing Without Static Payloads
Explore innovative dynamic methods for automated XSS detection without static payloads, including techniques for Stored XSS and custom exploit generation. Learn to overcome limitations of traditional approaches.
Copy Pest - A Case Study on the Clipboard, Blind Trust, and Invisible Cross-Application XSS
Explore clipboard vulnerabilities and cross-application XSS in this case study on invisible security threats and blind trust in web applications.
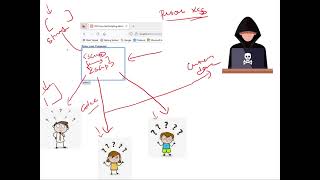
Persistent XSS (Cross-Site Scripting) Attack: What It Is and How to Prevent It
Explore persistent XSS attacks, witness a live demo, and learn effective prevention strategies to enhance web application security.
GraphQL CTF and XSS Challenge Walkthrough - Hacker101 and Bug Bounty Notes
Explore GraphQL CTF challenges and XSS vulnerabilities in this hands-on session. Learn practical hacking techniques and improve your bug bounty hunting skills.
New Web Platform Security Features to Protect Modern Web Applications
Explore modern web browser security features to protect against XSS, CSRF, and clickjacking. Learn about CSP3, Trusted Types, Fetch Metadata Request Headers, CORP, and COOP for enhanced application security.
Breaking and Fixing Web Application Security
Explore web application security challenges, attack vectors, and proactive measures. Learn to identify vulnerabilities, implement secure coding practices, and safeguard user data in the digital realm.
Beginner to Advanced Bug Bounty Hunting Course - 2022
Comprehensive ethical hacking course covering web application vulnerabilities, penetration testing techniques, and programming skills for aspiring bug bounty hunters and security professionals.
The Power of Guardrails - How to Slash Your Risk of XSS in Half
Learn effective strategies to significantly reduce XSS vulnerabilities in web applications through powerful guardrails, enhancing overall security and protecting against common attack vectors.
Ghosts of XSS Past, Present & Future
Explore the evolution of Cross-Site Scripting (XSS) vulnerabilities, their impact on web security, and strategies for mitigation in this comprehensive presentation by a leading industry expert.
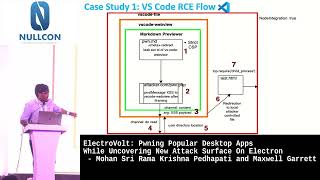
ElectroVolt - Pwning Desktop Apps Built On Electron
Explore vulnerabilities in Electron-based desktop apps, including novel attack vectors for remote code execution, with demonstrations on popular applications like Discord and VSCode.
Hacking Modern Desktop Apps with XSS and RCE
Discover essential techniques for auditing Electron applications, exploring XSS vulnerabilities in desktop environments, and leveraging them for remote code execution. Gain insights into attacking preload scripts and IPC.
Detecting & Exploiting XSS Vulnerabilities
Learn techniques for detecting and exploiting Cross-Site Scripting (XSS) vulnerabilities, enhancing your web security skills and understanding of common attack vectors.
Locking the Throne Room - ECMA Script 5, a Frozen DOM and the Eradication of XSS
Innovative approach to prevent XSS attacks using ECMA Script 5 features, sealing DOM properties and creating client-side IDS/IPS systems for modern browsers.
Hacking Android & iOS Apps with Deep Links & XSS - Mobile Hacking
Explore practical techniques for hacking Android and iOS apps using deep links and XSS attacks. Learn about user impersonation, bypassing authorization, and data exfiltration through real-world case studies.

Raining CVEs on WordPress Plugins with Semgrep
Leveraging Semgrep to identify vulnerabilities in WordPress plugins, reducing false positives, and automating XSS validation. Includes demos on custom rule creation and the XSSBomb tool.
Nothing New About XSS in Impress.js
Demonstrating XSS vulnerabilities in impress.js presentations, showcasing innovative features like a 3D cockpit view and dynamic slide content manipulation for enhanced interactivity and visual appeal.
Journey to Command Injection - Hacking the Lenovo ix4-300d
Demonstration of chaining vulnerabilities to remotely exploit a Lenovo NAS device, showcasing command injection, XSS, and CSRF techniques for full system compromise.