The Final Frontier - Security APIs in Modern Browsers
Explore modern browser security APIs and mechanisms that protect against common web attacks, enhance authentication, and restrict browser behavior, with code demonstrations and future insights.
Modern Web Application Defense with OWASP Tools
Learn to defend web applications using OWASP tools. Explore XSS, CSRF, and other vulnerabilities through live demos. Gain practical skills to prevent attacks and secure your applications effectively.
HTML5 Security Features - Advantages Over Traditional Web Technologies
Exploring HTML5's security features and comparing them to traditional techniques. Demonstrates how HTML5 APIs offer improved security for cross-domain communication, client-side persistence, and protection against common web vulnerabilities.
Headers for Hackers - Understanding and Optimizing HTTP Headers
Explore HTTP headers' impact on web performance, security, and functionality. Learn practical techniques to optimize your site using powerful header configurations.
Cookie Infrastructure at Meta - Managing Consent and Compliance
Explore Meta's cookie management system, featuring a central schema, enforced API, and Content-Security-Policy headers for robust control and compliance with user preferences.
Web Security and Encryption: From Browser Telemetry to Enterprise TLS - Guest Lecture
Explore web security with expert Scott Helme, covering encryption, privacy, DNS, and content security policy. Gain insights on browser telemetry and enterprise TLS.
HTTP Security Headers - A Technology History Through Scar Tissue
Explore HTTP security headers, their evolution, and best practices. Learn to leverage browser-built security controls, with a focus on implementing effective content-security-policy for enhanced web application protection.
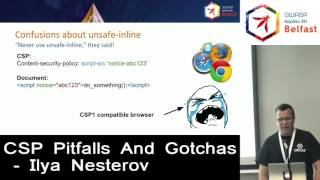
CSP Pitfalls and Gotchas
Explore common pitfalls and gotchas in Content Security Policy implementation, focusing on whitelist issues, SameOrigin policy, and unsafe inline practices. Learn strategies for building a robust security framework.
Restricting the Scripts, You're to Blame, You Give CSP a Bad Name
Explore Content Security Policy's role in web security, covering script restrictions, TLS enforcement, and framing control. Learn best practices and developer insights for effective CSP implementation.
CSP is Dead, Long Live CSP! - On the Insecurity of Whitelists and the Future of the Content Security Policy
Explore the evolution and challenges of Content Security Policy, analyzing its effectiveness, vulnerabilities, and future directions in web security.
Evaluating the Effectiveness of Content Security Policy in the Wild
Evaluación de la efectividad de la Política de Seguridad de Contenido en la práctica, analizando su adopción, configuración y debilidades frente a ataques XSS.
CSPAutoGen - Black-box Enforcement of Content Security Policy upon Real-world Websites
Explore black-box enforcement of Content Security Policy on websites, covering deployment, training, rewriting, and evaluation of CSPAutoGen for enhanced web security.
Breaking XSS Mitigations Via Script Gadgets
Explore a novel web hacking technique that bypasses XSS mitigations using script gadgets. Learn about HTML sanitizers, CSP, and practical demonstrations of this powerful attack method.
CSP Oddities
Explore Content Security Policy intricacies, common pitfalls, and innovative solutions. Learn to deploy effective CSP policies and discover potential vulnerabilities in web application security.
A Successful Mess Between Hardening and Mitigation
In-depth analysis of Content Security Policy for XSS prevention, exploring its effectiveness, debunking myths, and sharing real-world data on successful XSS mitigation in sensitive applications.
XSS Mitigation - The State of the Art
Comprehensive overview of XSS attacks and modern defense strategies, covering browser-based, server-side, and framework-specific mitigations for web developers and security professionals.
No More XSS - Deploying CSP with Nonces and Strict-Dynamic
Learn to implement Content Security Policy with nonces and strict-dynamic to prevent XSS attacks. Discover practical deployment strategies for Pinterest and Instapaper, and understand potential vulnerabilities.
Bypassing Browser Security Policies for Fun and Profit
Explore mobile browser vulnerabilities and security policy bypasses, including Same Origin Policy and Content Security Policy. Learn testing methodologies and see real-world examples of Android browser exploits.
Your Scripts In My Page - What Could Possibly Go Wrong?
Explore the security risks of cross-domain script inclusion, including potential data leaks and account compromises. Learn detection methods and defensive measures to protect against these vulnerabilities.
Next Gen Web Pen Testing - Handling Modern Applications in a Penetration Test
Explore modern web application security with insights on WebSockets, REST APIs, and Content Security Policy. Learn practical penetration testing techniques for next-gen web technologies.
Abusing Bleeding Edge Web Standards for Appsec Glory
Explore risks and mitigation strategies for modern web security standards like SRI, CSP, and HPKP. Learn about implementation challenges, trade-offs, and potential exploits in legacy applications.