Policy-as-Code Across the Stack
Explore Policy-as-Code implementation using open-source frameworks for enhanced security and compliance across the technology stack, reducing manual intervention and improving risk management.
Secure Container Management with Podman - Installation and Usage Guide
Learn to use Podman for secure, rootless container management. Covers installation, running containers, security features, Podman Compose, building images, handling privileged ports, and setting up Podman services.
Logs Collection with eBPF - A Super-Powered Approach for Kubernetes
Explore eBPF's potential to revolutionize Kubernetes log collection, offering efficient, context-rich observability by extracting data directly from the kernel, surpassing traditional methods.
Shifting Left in Podman with Copr, Packit and TMT
Explore Podman's CI workflow evolution using Packit, CoPR, and TMT for efficient development and testing across Red Hat distributions.
Working with Multi-Platform Container Images - OCI Index and Manifest List
Explore multi-platform container images, OCI Index, and Manifest List. Gain insights into cross-platform compatibility and see a Golang example for better understanding of image pulling and running.
Managing Micro-Containers Without DNF or Microdnf
Explore alternative methods for managing micro-containers without DNF or Microdnf, focusing on servicing containers and efficient package management for Fedora and RHEL.
Containers in Automobiles - Current Plans and Future Potential
Explore containerization in automotive edge devices, focusing on Podman improvements and functional safety in interference-free environments.
A Journey Through Supporting VMs with Dedicated CPUs on Kubernetes - Lecture
Explore dedicated CPU support for VMs on Kubernetes, delving into resource allocation models, cgroups, and the challenges of implementing true CPU pinning in Kubevirt.
Seitan: A Plant-Based Recipe Against Syscall Anxiety
Explore a unified approach to privilege separation in containers and VMs using Seitan. Learn to write JSON recipes for filtered system calls and enhance security for untrusted workloads.
Root is Less: Container Networks Get in Shape with Pasta
Explore pasta, a new usermode networking approach for rootless containers. Learn about its integration with Podman, advantages over Slirp, and emerging use cases for containerizing legacy applications.
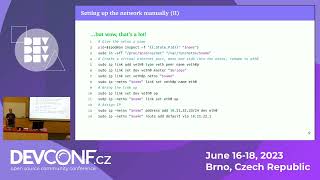
Rootful Networking with Rootless Podman Containers
Explore rootful networking with rootless Podman containers, uncovering network namespace intricacies and enhancing container security without sacrificing functionality.
Podman Desktop: From Containers to Kubernetes
Simplify container development and migration to Kubernetes with Podman Desktop. Learn its benefits, user-friendly interface, and steps for preparing containers for Kubernetes deployment.
SQL Server Containers and Kubernetes - Going to Production
Modernize your data estate with SQL Server containers in Kubernetes. Learn to build a hybrid data estate for flexible deployment options.
AI-Enabled Chatbot to Production MLOps Application - Red Hat AI Portfolio Demo
Explore Red Hat's AI portfolio: from simple chatbots to full-scale MLOps applications for enterprise. Learn about Podman AI Lab, RHEL AI, and OpenShift AI for building and deploying AI solutions.
Podman Desktop for Working with Containers and Kubernetes
Explore Podman Desktop's features for managing containers and Kubernetes locally, streamlining development and testing of containerized applications.
Serverless Compute for Event-Driven Architecture - Using AWS Lambda and ECS on Fargate
Explore serverless compute options for event-driven architectures. Learn to leverage AWS Lambda and ECS on Fargate for scalable, efficient business logic execution in response to events.
From Void to Monje Newbie - Containers no son Docker pero Docker es un container
Explora las mejores prácticas de seguridad en DevSecOps, enfocándose en contenedores y Docker. Aprende sobre tecnologías cloud y cómo implementar seguridad en el ciclo de vida de las aplicaciones.
Fileless Attack in Containers
Explore fileless attacks in containers, their detection using eBPF tools, and implications for cloud-native security. Learn about this growing threat and defense strategies from an expert developer.
AppSec’s Future and the Rise of the Chief Product Security Officer
Explore the evolution of application security and the emerging role of Chief Product Security Officers in addressing modern digital infrastructure challenges.
Managing Secrets in Your Cloud Environment - AWS, GCP, and Containers (and Beyond)
Comprehensive guide to managing sensitive data in cloud environments, covering storage options, common mistakes, identity considerations, evaluation criteria, and solutions for AWS, GCP, and Azure containers.
OpenShift Advanced Management with Red Hat CloudForms
Explore advanced OpenShift management using CloudForms for enhanced visibility, metrics analysis, chargeback, and security in container environments.