Kubernetes Namespaces Unleashed: Unlocking the Full Potential of Your Infrastructure
跨云多租户Kubernetes平台构建经验分享:探讨Adobe五年来的平台开发历程,包括指导理念、挑战和经验教训,以及如何平衡速度和可靠性。
Enhancing Node Stability Through Containerd and Kata Containers Interface Evolution
探讨containerd和Kata Containers的接口演进,解析两者的区别与协作,展示如何通过架构变化提升容器运行时性能和节点稳定性,并介绍最新改进。
Efficient Storage Handling for Sandboxed Runtimes in Kubernetes
Exploring efficient storage solutions for sandboxed runtimes like Kata Containers, focusing on direct storage assignment for improved IO performance and security in containerized environments.
Build Serverless with Kubernetes, Kata Containers and Bare Metal Cloud - Alibaba's Approach
Explore Alibaba's serverless infrastructure using Kubernetes, Kata Containers, and bare metal instances. Learn about multi-tenancy, isolation, and performance optimizations in cloud environments.
Confidential Containers: The Next Episode in Workload Isolation
Explore advanced container isolation using Kata-CC, leveraging Trusted Execution Environment features for enhanced security in multi-tenant environments through workload attestation and memory encryption.
From Secure Container to Secure Service
Explore advancements in secure container technologies and their integration with ServiceMesh for enhanced Kubernetes security. Learn about performance improvements, lightweight hypervisors, and end-to-end service protection strategies.
Confidential Containers for GPU Compute - Incorporating LLMs in AI Lift-and-Shift Strategy
Explore confidential containers for GPU-accelerated AI, integrating LLMs and Kubernetes for secure, high-performance computing while maintaining data privacy in cloud-native environments.
Kata Containers 4.0 - Full Lifecycle GPU Management for AI/ML Workloads
Discover how Kata Containers 4.0 revolutionizes GPU management for AI/ML workloads through CDI framework integration, enhanced security features, and streamlined resource allocation in Kubernetes environments.
A Controlled, Secure Vsock Tunnel for High-speed Data Transfer Between Guest and Host
Discover how to implement fast data transfer between guest and host systems using vsock tunnels, with focus on security controls, kernel-level implementations, and performance optimization techniques.
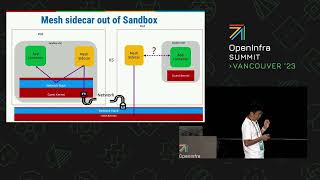
Towards Kata Containers 4 - When Kata Containers Meet Service Mesh
Explore security challenges and solutions for Kata Containers in service mesh environments, focusing on threat models, infrastructure sidecar designs, and performance benchmarks.
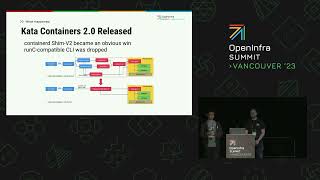
Re-enabling Kata Containers with Moby - A History of Integration and Solutions
Discover how to integrate Kata Containers with Moby runtime, exploring the evolution, challenges, and solutions for seamless container virtualization implementation.
Kata Containers 3.0 - Virtualization Optimized for Cloud Native Environments
Discover the latest evolution of Kata Containers 3.0, featuring the new Dragonball hypervisor and async rust runtime for enhanced container virtualization and cloud-native performance.
Zero Trust Architecture for Containers with Kata and Confidential Computing
Dive into advanced container security using Kata and Confidential Computing to implement zero-trust architecture, protect sensitive workloads, and achieve attestable pod integrity in Azure environments.
Experience with Hard Multi-Tenancy in Kubernetes Using Kata Containers
Explore Databricks' implementation of hard multi-tenancy in Kubernetes using Kata Containers, addressing challenges, trade-offs, and cloud provider heterogeneity for secure serverless platforms.
Running Isolated VirtualClusters with Kata and Cluster API
Explore hard multi-tenancy in Kubernetes using Cluster API Nested, VirtualCluster, and Kata runtime for workload isolation and virtual networking, reducing maintenance while enhancing security.
Beyond the Cluster: Harnessing the Power of Kubernetes Namespaces
Explore Adobe's journey in building a cross-cloud, multi-tenant Kubernetes platform. Learn about tools, challenges, and lessons for balancing velocity and reliability in modern developer ecosystems.
CNCF Live Webinar - Kata and Arm, a Secure Alternative in the 5G Space
Explore Kata Containers and Arm technology as secure alternatives for 5G infrastructure, covering deployment, security, and integration with Kubernetes and Docker.
Introducing SPDK Vhost FUSE Target for Accelerated File Access in VMs and Containers
Explore SPDK userspace vhost-user-fs solution for accelerating virtio-fs in VMs and containers. Learn about performance gains using blobfs and various storage protocols.
KVM Status Update and Kata Containers - Keynote Sessions
Explore KVM's latest developments and the intersection of Kata, containers, and KVM in these insightful keynote sessions from industry experts.
Kata Containers - Security and Containers Without Compromise
Explore Kata Containers: an open-source runtime offering enhanced security through virtualization while maintaining container-like performance. Learn about its integration with Confidential Containers and real-world applications.
Trust No One - Bringing Confidential Computing to Containers
Explore confidential computing for containers, leveraging hardware-based Trusted Execution Environments to protect cloud data and code without relying on third-party trust.