Auditing Kubernetes Users: Tracking Security Holes
Discover how to implement effective Kubernetes auditing mechanisms, track user activities, and detect security vulnerabilities through RBAC analysis and audit API implementation.
Defending AI on Kubernetes - A Red Team Security Playbook
Explore offensive security strategies and defense mechanisms for AI systems on Kubernetes, focusing on vulnerability assessment and protective measures from an attacker's viewpoint.
From EC2 to Kubernetes - Takeaways from a Brownfield Migration
Discover the real-world journey of migrating 1800 EC2 instances to Kubernetes, exploring strategies for customer migration, resource optimization, and overcoming deployment challenges in a SaaS environment.
Supercharge Your Kubernetes DevOps - Achieving Observability Maturity with OpenTelemetry
Master OpenTelemetry implementation for enhanced Kubernetes observability, focusing on performance monitoring, security tracking, and operational stability in containerized environments.
10 Years of Kubernetes History: Evolution, Impact, and Future Perspectives
Explore the decade-long evolution of Kubernetes through firsthand insights from a tech veteran who worked at Google, Red Hat, and VMware, gaining perspective on its impact and future.
Harnessing Kubernetes - The Paradigm Shift to Code Provisioned Clusters and Pods
Master Infrastructure as Code principles for Kubernetes, exploring tools like Terraform and Pulumi to efficiently provision, deploy, and manage containerized applications and clusters.
Building a Complete Infrastructure Ecosystem with Kubernetes Ready for Production
Master the rapid deployment of production-ready infrastructure using Docker, Kubernetes, and Rancher through hands-on practice, enabling efficient and scalable application management.
Watching the Watchers - The Hidden Risks of Container Scanning Tools
Explore critical security risks and mitigation strategies for container vulnerability scanning tools, focusing on system protection, secure configurations, and defense-in-depth approaches.
Navigating the Quantum Readiness Journey - Open-Source Cryptography, PKI and Signing Tools
Explore post-quantum cryptography standards and their implementation in open-source tools, focusing on IoT, container security, and software supply chain protection through quantum-resistant solutions.
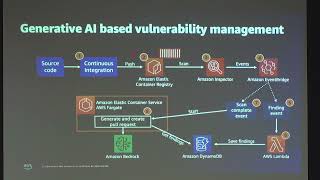
Applying Generative AI to Container CVE Remediation in CI Pipelines
Discover how to leverage generative AI for automating container vulnerability remediation in CI pipelines, with practical demonstrations and implementable solutions for efficient security management.
Container Image Workflows at Scale with Buildpacks
Discover how Buildpacks transform source applications into cloud-ready images, enabling efficient container workflows, enhanced security through SBOM, and scalable deployment for web apps, batch processing, and FaaS platforms.
Designing and Implementing a Cloud Native Framework for Farm Data Analytics
Discover how cloud-native frameworks revolutionize farm data analytics, exploring a real-world implementation managing 1500 cows through KubeStellar and Software-Defined Farm paradigms for optimized agricultural operations.
A Mad Scientist's Guide to Automating Container Networking Interface with Generative AI
Explore automating Kubernetes networking through hands-on experimentation with generative AI, using Ollama for containerized LLM to configure CNI, with practical examples and a dash of mad scientist humor.
GitOps System Security - Protecting Against Privilege Escalation
Discover critical security insights for GitOps systems, including vulnerability analysis, misconfiguration prevention, and practical protection strategies against privilege escalation and cluster takeover threats.
Microsegment Your Network Like Mastercard with AdminNetworkPolicy
Discover how to implement cluster-wide network security using AdminNetworkPolicy in Kubernetes, featuring Mastercard's approach to enforcing granular controls and achieving PCI compliance through multi-tenant isolation.
Video Storage Toolkit with Metropolis Microservices for Jetson - Overview and Installation
Comprehensive guide to NVIDIA's Video Storage Toolkit for Jetson, covering installation, usage, code samples, and debugging. Ideal for developers working on edge AI applications with video management needs.

Components - WebAssembly's Docker Moment
Explore how WASI .2 and WebAssembly Component Model revolutionize cloud-native tech, enabling secure, portable, and interoperable software components across diverse computing environments.
Common Kubernetes Attack Vectors and How to Secure Your Cluster
Discover essential security strategies for Kubernetes deployments, covering authentication, network policies, pod security, and threat detection techniques for robust cluster protection.
Demystifying Kubernetes Networking for Enterprise and Service Providers
Dive into Kubernetes networking fundamentals, exploring container connectivity, load balancing, and Gateway API for enterprise and service provider environments. Learn key concepts for managing modern cloud-native infrastructure.
Kubernetes Networking Fundamentals for Network Professionals
Discover essential Kubernetes networking concepts, from network namespaces and pods to CNI plugins, security policies, and emerging trends in network orchestration for modern infrastructure deployment.
Keyboards, Kiosks, and Kubernetes - Containerizing HID Workloads
Discover how to containerize GUI applications and kiosks in Kubernetes, enabling efficient device management, resource sharing, and enhanced security while maintaining host/workload decoupling.