10 Kubernetes Security Mistakes to Avoid
Discover critical security vulnerabilities in Kubernetes deployments and learn practical fixes for common misconfigurations, based on real-world data analysis from 10K+ clusters.
A Day in the Life of a Base Image - Evolution of Vulnerabilities in Popular Containers
Explore container security evolution through data-driven analysis of popular DevOps images, vulnerability scanning challenges, and practical solutions for maintaining secure development workflows.
Kubernetes Attack Simulation - The Definitive Guide to Security Monitoring and Detection
Master Kubernetes security monitoring and attack simulation techniques for effective threat detection and defense in containerized environments.
Sécuriser les Secrets Kubernetes avec Vault et GitOps - Protection Contre les Accès Non Autorisés
Découvrez comment sécuriser vos secrets Kubernetes avec GitOps, en utilisant Vault et ArgoCD pour protéger votre infrastructure contre les accès non autorisés tout en maintenant l'efficacité de vos pipelines CI/CD.
Cracking the Code of Cloud Security - DevSecOps and Container Security
Explore cloud security challenges, container vulnerabilities, and DevSecOps strategies. Learn automated vulnerability management, configuration best practices, and network segmentation for enhanced protection.
Secure FIPS Containers for Government Services
Secure government services with FIPS-compliant containers. Learn to implement OpenSSL, Java, Python, and Go security measures for enhanced protection.
External Secrets Operator and Secrets Store CSI Driver - A Practical Comparison
比較 External Secrets Operator 和 Secrets Store CSI Driver 的實際應用,探討 Kubernetes 中秘密管理的最佳實踐。
Navigating the Quantum Readiness Journey: Open-Source Cryptography, PKI and Signing Tools
Explore quantum-resistant cryptography for IoT, containers, and software supply chains using open-source tools. Gain hands-on insights into FIPS-certified APIs, PKI software, and signing solutions for enhanced cybersecurity.
Exploring Essential Security Checks for Open Source Go Projects
Discover essential security tools for Go projects: gosec, govulncheck, and sigstore/cosign. Learn to enhance code security, scan vulnerabilities, and secure the supply chain.

Secret Management for Azure AKS Cluster
Explore AKS workload integration with Azure Key Vault and optimize secret consumption for enhanced security in your Azure Kubernetes Service environment.
Unlocking Security Policies and Guardrails - The Bridge Between Dev, Sec and Ops in Kubernetes Deployments
Explore security policies and guardrails in Kubernetes deployments, bridging the gap between development, security, and operations teams for enhanced collaboration and protection.
Secure Kubernetes Manifests with Cosign and Kyverno
Explore open-source tools Cosign and Kyverno to secure container images and Kubernetes manifests. Learn implementation strategies for production clusters and essential use cases.
Kubernetes Goat - Interactive Kubernetes Security Learning Playground
Explore Kubernetes security through hands-on scenarios, attack simulations, and real-world vulnerabilities. Learn to identify and mitigate risks using open-source tools for secure code and container deployment.
Building an EKS Kubernetes Cluster with Ubuntu 20.04 on FIPS Mode
Learn to create EKS Kubernetes clusters using Ubuntu 20.04 in FIPS mode. Discover how to meet compliance requirements, use certified crypto libraries, and leverage Ubuntu Pro features for secure container deployments on AWS.
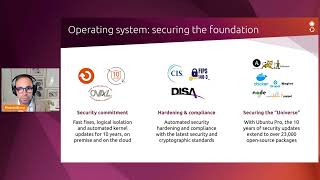
Canonical's Role in Security for Cloud Native Landscapes
Explore Canonical's comprehensive security approach for cloud-native environments, covering host OS, containers, and infrastructure to deliver defense-in-depth protection against evolving threats.
Securely Managing Open Source on AWS - Ubuntu and Beyond
Dive deep into open-source vulnerabilities and learn how Canonical Ubuntu secures applications across output, runtime, messaging, data, and observability on AWS.
Building and Deploying Ubuntu FIPS Containers on EKS
Create, publish, and deploy FIPS container images on AWS EKS using Ubuntu Pro and ECR. Learn secure containerization practices for compliance-sensitive workloads.
Accelerate .NET Development and Deployment on Ubuntu
Optimize .NET development on Ubuntu with expert guidance, explore chiselled containers, and enhance security for seamless integration and deployment processes.
Copacetic - Patch Your Container Images Seamlessly with COPA
Explore Copa, a Go-based CLI tool for patching container images using vulnerability scanning results from tools like Trivy. Learn to address critical security vulnerabilities efficiently.
Building Zero CVE Docker Images - Strategies and Solutions
Explore strategies for building zero-CVE Docker images, focusing on Chainguard images and discussing potential improvements in supply chain security. Includes resources for further learning.
Creating Zero-CVE Base Images for Dockerfiles
Create CVE-free base images for Dockerfiles using BuildSafe. Search and add required packages easily. Simplify the process of building secure artifacts with zero vulnerabilities.