Verifying and Signing EBPF Programs with Inspektor Gadget
Enhance eBPF program security with Inspektor Gadget. Learn to sign and verify OCI images using cosign, improving overall system safety by running only authenticated eBPF programs.
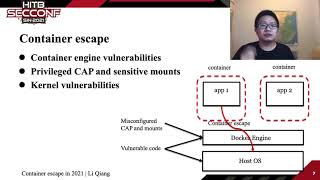
Container Escape in 2021
Explore new methods for escaping privileged runc containers, focusing on cloud security vulnerabilities and innovative exploit techniques in container environments.
Defensa en Profundidad para Aplicaciones en Contenedores
Estrategias de defensa en profundidad para aplicaciones en contenedores, desde el código hasta la interfaz de usuario, en entornos cloud o locales. Enfoque en controles automatizados y mejores prácticas de seguridad.
My App Is Running With Kubernetes - Am I Aware of the Potential Exploits That I've Embedded Inside?
Explora las vulnerabilidades potenciales en aplicaciones Kubernetes y aprende prácticas de DevSecOps para mejorar la seguridad en entornos cloud nativos.
The Next Disruption - Security Beyond the Perimeter and Endpoint
Explore evolving cybersecurity challenges and innovative solutions beyond traditional perimeters, focusing on cloud, containers, and APIs in the context of recent global events.
Containers - Your Ally in Improving Security
Explore built-in security tactics for Kubernetes and Docker, including automated configurations, read-only filesystems, and limiting cross-container communications to enhance service security.
Outside the Box - Breakouts and Privilege Escalation in Container Environments
Explore real-world container escapes and privilege escalation techniques in popular solutions like Docker and Kubernetes. Learn methodologies for assessing containerized environments and implementing secure configurations.
Security-Oriented OpenShift Within Regulated Environments
Explore how a major bank implemented OpenShift to modernize deployment, enhance security, and meet regulatory standards. Learn about building secure pipelines and isolating containers in production environments.
A Wander Through the World of Container Security
Explore container security, from Docker to Kubernetes, covering breakout vulnerabilities, networking challenges, and RBAC. Gain insights into potential threats and future attack vectors in containerized environments.
Controlled Mayhem With Cloud Native Security Pipelines
Explore cloud-native security pipelines, comparing traditional and modern approaches, while addressing challenges in container orchestration, access control, and CI/CD processes.
Cilium - Container Security and Networking Using BPF and XDP
Explore Cilium's innovative use of BPF for container networking and security, covering performance, DDoS mitigation, and microservices protection in cloud-native environments.
Container Security 101
Aprende sobre amenazas, vulnerabilidades y mejores prácticas de seguridad en contenedores, incluyendo herramientas para proteger imágenes y entornos de ejecución.
The Golden Ticket - Docker and High Security Microservices
Explore Docker security for microservices: container design, network protection, secrets management. Learn practical techniques for building robust, secure architectures using Docker's latest features.
An Ounce of Prevention - Curing Insecure Container Images
Discover best practices for securing container images and learn about Docker Scan, a powerful tool for identifying vulnerabilities in your containerized applications.
Hacking into Your Containers, and How to Stop It
Explore container security vulnerabilities and learn proactive DevSecOps practices to protect your deployments. Live hack demonstration and practical steps for hardening clusters against attacks.
Lack of Self Isolation - Inside a Container Exploit
Explore container vulnerabilities, focusing on lack of self-isolation. Learn about potential exploits, their causes, and solutions for improved container security.
Running KubeVirt Workloads with No Additional Privileges
Explore running VMs on Kubernetes without root privileges using KubeVirt. Learn about security practices, SELinux integration, and the journey to achieve rootless VM execution.
Container Security - Theory & Practice at Netflix
Explore Netflix's container security journey, covering theory, architecture, and practical lessons learned as container usage rapidly expanded across the organization.
Building Your Development Pipeline
Explore containerized application pipelines: build minimal images, scan and sign, enforce compliance, and learn best practices for enterprise container registries and Kubernetes orchestration.
Hacked! Run Time Security for Containers
Explore container security challenges, runtime monitoring, policy enforcement, and forensics using system call signals. Learn to detect threats and implement robust security measures for containerized environments.
Hardware-Secured Docker with Intel Clear Containers
Explore hardware-secured Docker containers using Intel Clear Containers, enhancing security through virtualization while maintaining performance and compatibility with container ecosystems.