Tracing Struct Accesses with Struct Stalker
Explore Struct Stalker, an LLDB script for tracing struct/object accesses in C/C++ apps. Learn about LLDB scripting and innovative memory access tracking techniques.
Static Instrumentation Based on Executable File Formats
Static instrumentation techniques for executable files without modifying code or system environment. Enables architecture-independent injection and hooking without privileged access, suitable for integrity checking and non-rooted environments.
Discovering the iOS Instruments Server
Reverse-engineering of iOS privileged server providing sensitive data to Apple's debugging tools. Explores techniques used to uncover and analyze this critical system component.
Exploiting Userland Vulnerabilities to Get Rogue App Installed Remotely on iOS 11
Exploiting iOS11 vulnerabilities to remotely install rogue apps, bypassing security enhancements and code signing requirements without kernel exploits. Techniques for sandbox escape and persistent installation demonstrated.
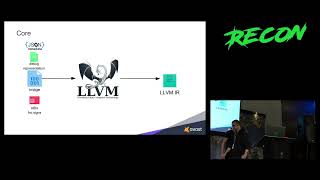
An Open-Source Machine-Code Decompiler
Explore RetDec, an open-source machine-code decompiler for analyzing binary applications. Learn about its components, applications in reverse engineering, and real-world examples demonstrated by Avast developers.
Malware Analysis and Automation using Binary Ninja
Explore malware analysis automation using Binary Ninja platform. Learn to adapt quickly to evolving threats, perform basic analysis, and utilize API for configuration data extraction from real-world samples.
Reverse Engineering of Blockchain Smart Contracts
Explore reverse engineering of blockchain smart contracts, focusing on Ethereum, Neo, and EOS platforms. Learn about virtual machines, assembly languages, and tools for security analysis.
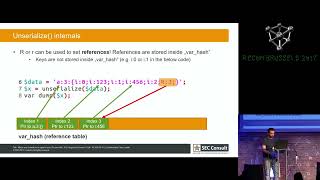
When Your Firewall Turns Against You
Explore how firewalls can become security vulnerabilities, with insights on potential exploits and mitigation strategies for network administrators and security professionals.
Keeping Your Tools Safe IDA
Explore techniques for safeguarding IDA tools and enhancing reverse engineering security in this concise presentation from REcon Brussels 2017.
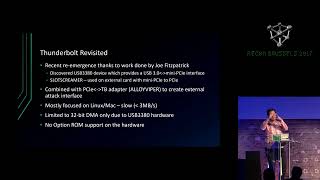
Getting Physical with USB Type-C - Windows 10 RAM Forensics and UEFI Attacks
Explore embedded microcontrollers in modern devices, focusing on the Surface Aggregator Module. Learn about security, firmware updates, and potential hardware implants in this deep dive into low-level system architecture.
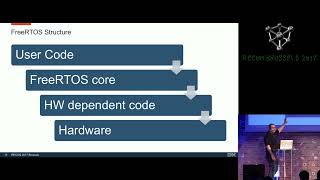
Embedded Devices Reverse Engineering
Explore reverse engineering techniques for embedded devices using FreeRTOS. Learn about memory organization, task handling, and security features. Gain insights into automating the process with IDA scripts for efficient firmware analysis.
Contributor Analysis
Learn a simple cryptanalysis technique to detect and attack flawed cryptographic algorithms. Explore contributor analysis, its theoretical principles, and practical applications in breaking ciphers.
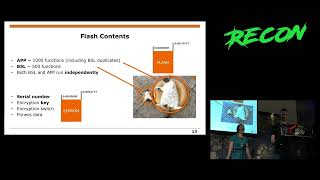
Create Your Own Fitness Tracker Firmware
Reverse-engineering Fitbit Flex firmware: exploring encryption, BLE communication, and protocols. Demonstrating wireless custom firmware flashing and enabling raw accelerometer readings.
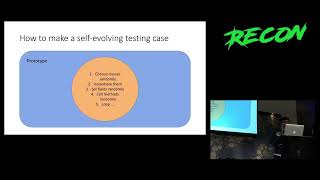
PWN Flash with Reflection and HashTables
Explore advanced Flash exploitation techniques using reflection and HashTables. Learn about fuzzing tools, vulnerability discovery, and bypassing modern mitigations in Windows 10.
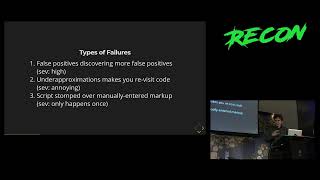
Sum Total of ISA Knowledge - Analyzing Your Binary Analysis Tools
Explore techniques to measure and verify architecture support in binary analysis tools, enhancing firmware reverse engineering through selective application of dynamic analysis methods.
Analyzing TRISIS - The First Safety Instrumented System Malware
Detailed analysis of TRISIS malware targeting safety systems, blending hardware and software reverse engineering. Explores PowerPC payloads, Triconex firmware, and discusses implications for industrial control security.
Taint-Based Return Oriented Programming
Explore an intermediate approach to return oriented programming using taint-based analysis, balancing speed and query expressiveness for efficient gadget discovery and chaining.
Recovering Software Architecture from Embedded Binaries
Discover techniques for recovering software architecture from large binaries using CodeCut and local function affinity, with applications in automated module-to-module call graphs and section naming.
Sandbagility - Reverse Engineering Framework for Windows Dynamic Analysis
Hybrid framework for Windows malware analysis combining dynamic and sandbox approaches. Offers stealthy, adaptive solution to reduce analysis time, demonstrated with WannaCry case study.
This Dump is a Puzzle - Reconstructing J2ME Firmware from an Unknown Fragmented File System
Explore techniques for reconstructing embedded Java firmwares from fragmented file systems, developing puzzle-solving algorithms to piece together unknown J2ME fragments.
Rattle - An Ethereum EVM Binary Analysis Framework
Explore Rattle, an innovative framework for analyzing Ethereum smart contracts, enhancing auditability and security in blockchain interactions through advanced binary analysis techniques.