Exploiting XXE Vulnerabilities in File Parsing Functionality
Techniques for exploiting XXE vulnerabilities in file parsing, focusing on XML-supported formats like docx and xlsx. Includes real-world examples and introduces a tool for creating 'XXE backdoored' files.
Mobile Point of Scam - Attacking the Square Reader
Explores vulnerabilities in Square Reader devices, revealing potential for fraudulent transactions and credit card skimming through software flaws and hardware modifications in mobile point-of-sale systems.
Distributing the Reconstruction of High-Level Intermediate Representation
Explore distributed reverse engineering techniques using intermediate representation in a clustered environment to analyze malware, extract characteristics, and improve threat intelligence initiatives.
Reverse Engineering Flash Memory for Fun and Benefit
Explore Flash memory reverse engineering techniques, including direct interaction, reprogramming, and file system analysis. Learn to handle meta information, deal with bad blocks, and leverage journaling file systems for deeper insights.
Advanced Windows NT - 2K Security
Explore advanced Windows NT/2K security, including payloads, buffer overflows, and kernel mode injection techniques for enhanced system protection.
National Information Assurance Partnership
Explore the National Information Assurance Partnership and its impact on cybersecurity standards and practices in this insightful presentation from Black Hat USA 2000.
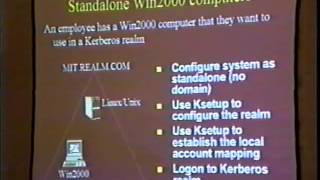
Defending Your Network with Active Directory Services
Explore advanced network defense strategies using Active Directory Services, focusing on cutting-edge techniques to enhance security and protect against evolving threats.
Compromising Web Servers and Defensive Techniques
Explore web server vulnerabilities and learn defensive strategies to protect against common attacks and security breaches in this comprehensive cybersecurity presentation.
Real-World Techniques in Network Security Management
Explore practical network security management techniques, focusing on real-world applications and strategies to enhance organizational cybersecurity posture.
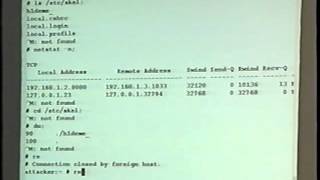
Getting Rooted and Never Knowing It
Explore advanced hacking techniques and stealthy rootkit deployment methods to understand and defend against sophisticated cyber threats.
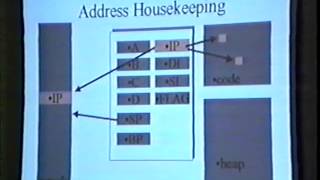
Advanced Buffer Overflow Techniques
Explore advanced buffer overflow techniques, including stack injection, heap exploitation, and protection bypassing. Learn about payload crafting, injection vectors, and dynamic function loading.
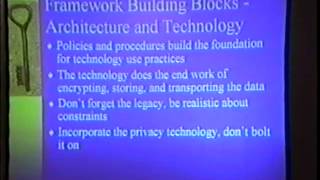
Policy to Technology - Translating U.S. Privacy Regulations for Implementation
Explore U.S. privacy regulations and their practical implementation in technology, bridging the gap between policy and technical solutions for data protection.
The Internet and the Death of Security
Explore the impact of the Internet on security paradigms with cryptography expert Bruce Schneier, examining evolving threats and challenges in the digital age.

The Return of Stack Overflows in the Linux Kernel
Exploiting Linux kernel vulnerabilities: techniques for bypassing security controls, leveraging nftables bugs, and achieving code execution. Includes mitigation strategies and a novel per-softirq stack randomization implementation.
Feeding Gophers to Ghidra
Improve Golang binary analysis in Ghidra with Java-based scripts. Recover strings, functions, and types for efficient malware research and vulnerability detection.
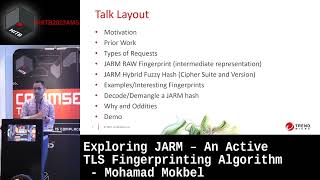
Exploring JARM – An Active TLS Fingerprinting Algorithm
Exploring JARM: An active TLS fingerprinting algorithm for clustering servers, identifying default settings, and detecting malicious servers. Includes C++ implementation, technical analysis, and improvements to enhance fingerprint confidence.
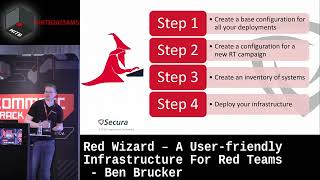
Red Wizard – A User-friendly Infrastructure For Red Teams
Introducing Red Wizard: An open-source tool for automated, OPSEC-safe Red Team infrastructure deployment. Streamlines setup with user-friendly wizards, self-documentation, and resilient architecture for efficient cybersecurity testing.
Nomadic Honeypots - How To Create Actionable CTI
Explore Automated Moving Target Defense using nomadic honeypots to create actionable Cyber Threat Intelligence. Learn deception techniques, attacker behaviors, and how to reduce attack surfaces while generating valuable threat insights.
Evolution of Learning - What Cyber Security Training Looks Like in 2023
Explore the evolution of cybersecurity training with expert trainers discussing market changes, pandemic impact, specialized courses, and tips for career advancement in this insightful panel discussion.
The Myths of Software Security
Exposé of common software security myths, debunking industry surveys, best practices, and popular concepts like "shift left" and SBOMs. Challenges conventional wisdom with evidence-based insights.
Everything Is Awful - And You're Not Helping
Humorous exploration of security failures and cynicism in the tech industry, highlighting common pitfalls and the challenges of creating truly secure systems.