PWNIE Awards
Celebrating excellence in information security with humor and recognition for groundbreaking achievements and epic fails in the cybersecurity industry.
Information Access and Information Sharing - Where We Are and Where We Are Going
Exploring DHS's vision for rapid, widespread cybersecurity information sharing across sectors. Discusses challenges and the goal of making threat indicators a public good for enhanced network defense.
Untangling the DOM for More Easy-Juicy Bugs
Explore dynamic JavaScript analysis with Hookish!, an open-source Chrome extension for penetration testing. Learn to uncover DOM-based vulnerabilities and enhance web app security assessments.
Breaking Payloads With Runtime Code Stripping and Image Freezing
Innovative defensive strategy to break attack payloads by removing unused code and APIs from application processes, enhancing security without runtime overhead or file modifications.
Review and Exploit Neglected Attack Surfaces in iOS 8
Explores overlooked iOS 8 vulnerabilities through fuzzing and code auditing, revealing system daemon crashes and memory corruption errors triggerable via XPC, plus an iOS kernel 0day.
BGP Stream
Explore BGP Stream: real-time detection of potentially malicious BGP/ASN changes for enhanced network security and traffic flow monitoring.
The Kali Linux Dojo Workshop - Kali USB Setups With Persistent Stores And LUKS Nuke Support
Learn to set up Kali Linux on USB with persistent storage and LUKS Nuke support. Explore live boot options, create persistence files, and handle emergency situations for secure, portable penetration testing.
The Kali Linux Dojo Workshop - Rolling Your Own - Generating Custom Kali Linux ISOs
Learn to generate custom Kali Linux 2.0 ISOs, tailoring the powerful penetration testing platform to your specific needs and preferences.
Taxonomic Modeling of Security Threats in Software Defined Networking
Comprehensive analysis of security threats in Software Defined Networking, exploring vulnerabilities, potential attack scenarios, and providing recommendations for effective countermeasures.
Tracking App Behaviors With - Nothing Changed - Phone For Evasive Android Malware
Explore advanced techniques for tracking and analyzing evasive Android malware behaviors, including obfuscation, dynamic code loading, and native-level monitoring, without modifying the phone's OS.
Behind The Mask - The Agenda, Tricks, And Tactics Of The Federal Trade Commission As They Regulate Cybersecurity
Insider's expose of FTC's cybersecurity regulation tactics, revealing government overreach and bullying practices. Highlights whistleblower case, Congressional investigation, and implications for businesses facing federal scrutiny.
Stranger Danger - What Is The Risk From 3rd Party Libraries
Explore the risks of third-party libraries in software, analyzing vulnerability metrics and exposure times. Learn strategies to mitigate risks and improve security practices in your organization.
These Are Not Your Grand Daddy's CPU Performance Counters - CPU Hardware Performance Counters For Security
Explore advanced CPU performance counters for enhanced platform security, including RowHammer defense and ROP mitigation. Learn practical techniques with real-world exploit demonstrations and performance impact analysis.
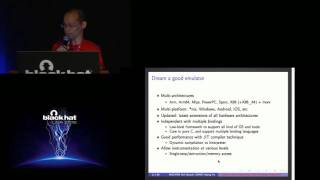
Unicorn - Next Generation CPU Emulator Framework
Versatile CPU emulator framework supporting multiple architectures and platforms. Offers clean API, thread-safety, and language bindings for building advanced security tools and research.
Understanding and Managing Entropy Usage
Explore cryptographic entropy usage, sources, and management across systems. Learn to analyze and improve random number generation for enhanced security in modern IT infrastructures.
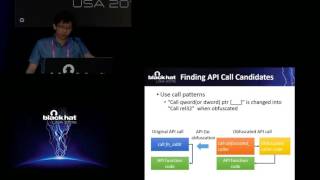
API Deobfuscator - Resolving Obfuscated API Functions in Modern Packers
Uncover obfuscated API functions in modern packers using memory access analysis and iterative run-until-API methods. Learn techniques to deobfuscate Themida 32/64 packed binaries for effective malware analysis.

Using Static Binary Analysis to Find Vulnerabilities and Backdoors in Firmware
Explore techniques for detecting vulnerabilities and backdoors in embedded device firmware using static binary analysis, focusing on challenges and automated solutions for complex binary blobs.
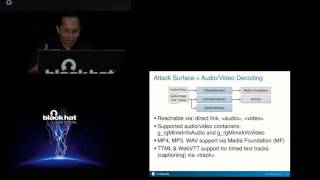
Understanding the Attack Surface and Attack Resilience of Project Spartan's New EdgeHTML Rendering Engine
Explore EdgeHTML's attack surface, compare it with MSHTML, and analyze exploit mitigations in Windows 10's new rendering engine for enhanced web security understanding.
Breaking Honeypots for Fun and Profit
Explore techniques to detect, bypass, and exploit honeypot technologies, turning defensive tools against defenders. Includes global honeypot mapping and vulnerability analysis.
Staying Persistent in Software Defined Networks
Explore vulnerabilities in software-defined networks, focusing on ONIE and network operating systems. Learn about potential exploits, malware persistence, and strategies for securing control plane networks.
Bypass Surgery - Abusing Content Delivery Networks
Exploring vulnerabilities in CDNs, this talk reveals attack patterns against high-availability websites, demonstrating potential risks and exploit development with far-reaching consequences.