Enterprise Security Architecture - Is It Time for a Booster Shot?
Explore evolving enterprise security architecture beyond traditional layered defense, addressing modern challenges like advanced hacking, cloud adoption, and remote work to enhance organizational cybersecurity.
Extract Data from Damaged Android Mobile Device - Version 7.X.X
Comprehensive workshop on extracting data from damaged Android devices, covering soldering, retrieval of device information, and extraction of various data types for forensic analysis.
Machine Learning for Intrusion Attempt Detections
Explore machine learning for real-time intrusion detection in cybersecurity. Learn to build a system using AI techniques, featuring insights from Google's Lead Security Engineer Varun Kohli.
Exploiting Android Messengers with WebRTC
Explore WebRTC vulnerabilities in Android messaging apps, their exploitation, and mitigation strategies. Learn about security research techniques and mobile application security.
Operationalizing Threat Intelligence for Collective Defense
Explore automated threat intelligence for proactive cybersecurity. Learn to collect, analyze, and share actionable insights in real-time, enhancing organizational defense against evolving threats.
The Great Sandbox Escape
Explore novel ransomware techniques, including virtual machine deployment for attacks. Learn about attacker strategies, detection methods, and cybersecurity insights from a malware specialist.
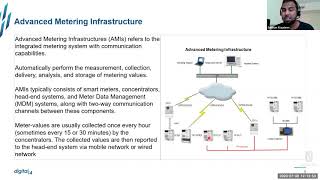
Insecurity of Smart Energy Meters - A Hardware Security Perspective
Explore hardware security vulnerabilities in smart energy meters, covering threat classifications, current trends, and testing methodologies for advanced metering infrastructure and grid security.
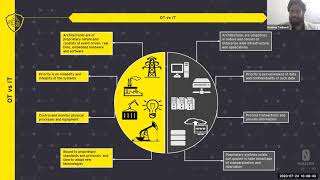
Security Compliance in the ICS Environment
Explore ICS/OT security compliance beyond vulnerability assessment. Learn to build a comprehensive security program integrating external and internal regulations for critical industrial environments.
Cyber Insurance - What Makes a Good Fit for You
Explore cybersecurity insurance essentials, including policy components, data elements for risk assessment, and key security controls. Learn to determine appropriate coverage and understand industry standards.
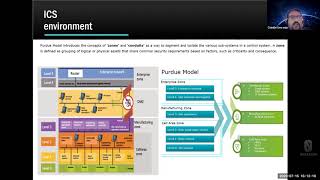
Assessing the Security Posture of ICS Infrastructure Using ISA 62443 Standard
Explore industrial cybersecurity, ICS threats, and resilience strategies using ISA-62443. Learn to assess and protect critical infrastructure from cyber attacks in the Energy, Resources, and Industrials sector.
Crouching Hacker, Killer Robo? Removing Fear from Cyber-Physical Security
Exploring cyber-physical security beyond fear-mongering, this talk examines root causes of vulnerabilities and proposes better approaches to embed security analysis in system design.
InfoSec Deep Learning in Action
Explore deep learning applications in cybersecurity, including use cases, data pipelines, algorithms, and real-world deployment challenges. Learn how AI can combat ransomware and other cyber threats.
XNU Heap Exploitation - From Kernel Bug to Kernel Control
Exploración detallada de la explotación del heap XNU, analizando dos vulnerabilidades del kernel y tres exploits. Cubre internos de XNU, técnicas de explotación y cambios entre versiones de iOS.
The One Weird Trick SecureROM Hates - Vol. 2
Exploring checkm8 vulnerability in iOS SecureROM, its exploitation for jailbreaking, and updates on pongoOS development. Insights into cross-platform challenges and future plans for iOS security research.
Don't Ruck Us Too Hard - Owning All of Ruckus AP Devices
Explore vulnerabilities in Ruckus AP devices, including pre-authentication remote code execution exploits. Learn about research methods, discovered CVEs, and a framework for cross-architecture analysis.
Rage Against the IDOR's - Using Machine Learning Models to Detect and Stop Authorization Bypass Vulnerabilities
Explore ML techniques to detect and prevent authorization bypass vulnerabilities in web applications, focusing on successful attacks and minimizing false positives.
Bug Bounty - Why Is This Happening
Explore bug bounty programs' challenges and realities from multiple perspectives, offering insights into their evolution, limitations, and potential for improvement in cybersecurity.
Basic Security Analysis on Data and Information
Learn essential digital security techniques for analyzing data and information, focusing on threat identification, communication safety, and practical tools for journalists and civil society groups.
HackIM CTF - Do's and Don'ts
Explore CTF competitions: learn security through challenges in web, crypto, reverse engineering, and more. Gain insights on dos and don'ts for successful participation in HackIM CTF.
Early Detection of Malicious Patterns in Event-Streaming Data
Explore advanced techniques for detecting malicious patterns in event streams using behavioral indicators and machine learning, focusing on early detection and automated pattern discovery.
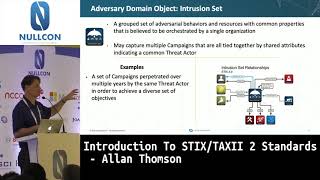
Introduction to STIX - TAXII 2 Standards
Comprehensive overview of STIX/TAXII 2 standards for Cyber Threat Intelligence, covering key concepts, data models, and interoperability challenges in threat intelligence sharing.