Making Security Approachable for Developers and Operators
Explore strategies to make security more accessible for developers and operators through APIs, secure-by-default platforms, and policy as code, enhancing overall security posture.
Perimeter-less - Engineering the Future of Defense
Explore modern defense strategies for complex digital ecosystems, focusing on designing defensible systems beyond traditional perimeter security to protect platforms, applications, and services at internet scale.
Exploiting Unknown Browsers and Objects
Discover hidden browser vulnerabilities with the Hackability Inspector, a new offensive toolkit for security researchers to explore and exploit unknown entities in embedded browsers.
FIESTA - An HTTPS Side-Channel Party
Explore HTTPS side-channel vulnerabilities and a new tool, FIESTA, for testing and exploiting these issues. Learn about a novel side-channel affecting major tech companies and its implications for online security.
Building Secure Software With OWASP Tools and Guides
Explore OWASP's comprehensive tools and guides for building secure software throughout the development lifecycle, from policy creation to implementation and verification.
What's New in TLS 1.3
Explore TLS 1.3's security enhancements, new protocol handshakes, and 0-RTT resumption. Learn about potential deployment pitfalls and how to avoid them in this comprehensive overview of the latest TLS version.
Optimize Your Pentesters Time
Optimize pentesting resources with Hunter, an open-source tool grading websites for low-risk security issues. Learn how eBay saved 10-15% of their pentesting budget and improved efficiency.
Lessons From the Threat Modeling Trenches
Insights from building threat modeling practices across organizations, focusing on reducing design errors. Explores lessons learned, challenges faced, and strategies for effective implementation in software security.
Digital Disease - How Healthcare Cybersecurity Challenges Can Claim or Save Lives
Explore healthcare cybersecurity challenges and their impact on patient safety. Learn how integrating clinicians with software developers can address risks in an increasingly connected medical landscape.
A Tour of API Underprotection
Explore API security threats, protection techniques, and advanced strategies. Learn about OAuth2, static API keys, mobile security, certificate pinning, and emerging technologies to strengthen your API security posture.
Threat Modeling Toolkit
Explore threat modeling techniques for software security using a cryptocurrency ecosystem example. Learn to analyze potential attacks, actors, and countermeasures early in development.
SecDevOps - Current Research and Best Practices
Explore current research and best practices in SecDevOps, covering static and dynamic analysis, security scaling, and infrastructure best practices for improved application security.
Applied Deception Beyond the Honeypot - Moving Past 101
Explore advanced deception techniques beyond honeypots for cybersecurity, drawing insights from military and political strategies to enhance defensive capabilities against diverse adversaries.
Prevention as a Business Strategy
Explore how prevention-focused cybersecurity strategies using AI and machine learning can protect businesses from evolving threats, reducing risks and costs associated with traditional detect-and-respond approaches.
ReproNow - Save Time Reproducing and Triaging Security Bugs
Discover ReproNow, an open-source tool streamlining security bug reproduction and triage. Learn how this browser extension captures vulnerability walkthroughs, saving time for security engineers and enhancing bug bounty programs.
Leveraging Cloud SDNs to Solve OWASP Top Ten
Explore cloud SDN implementation for OWASP Top Ten security, featuring virtualized controls, service chains, and open-source technologies. Learn practical solutions for web security in virtual networks.
Unpoisoned Fruit - Seeding Trust into a Growing World of Algorithmic Warfare
Exploración de los desafíos éticos y de seguridad en la inteligencia artificial y el aprendizaje automático, enfocándose en la necesidad de transparencia y confianza en los sistemas algorítmicos para prevenir conflictos y desastres humanitarios.
Costs of Coding to Compliance
Explore the challenges of coding for compliance, learn strategies to address security gaps, and discover how to prioritize initiatives for better risk management in application security.
Authentication Without Authentication
Explore IoT app authentication without user interaction. Learn innovative solutions for secure device communication, demonstrated on a Raspberry Pi.
We Come Bearing Gifts - Enabling Product Security with Culture and Cloud
Explore innovative approaches to product security, emphasizing automation, cloud deployment, and engineering enablement. Learn how Netflix balances security impact with developer productivity.
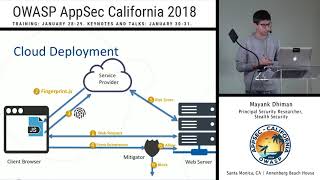
Breaking Fraud and Bot Detection Solutions
Demystifying browser fingerprinting and user behavior tracking in fraud detection, exploring vulnerabilities, and demonstrating proof-of-concept attacks against these defense mechanisms.