Cloud Forensics - Putting The Bits Back Together
Explore cloud forensics challenges and solutions in AWS, focusing on server breaches, disk imaging, and incident response techniques for various EC2 instance types and EBS volumes.
Remediate The Flag - Practical AppSec Training Platform
Hands-on platform for developers to find and fix security vulnerabilities in code. Offers real-time feedback, scoring, and customizable exercises to improve application security skills.
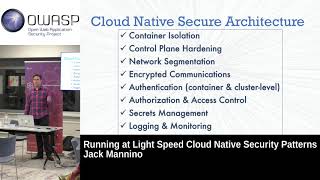
Running at Light Speed - Cloud Native Security Patterns
Explore cloud-native security patterns, including container isolation, control plane hardening, and network segmentation. Learn about authentication, authorization, and secrets management in cloud environments.
How to Get the Best AppSec Test of Your Life
Learn strategies to maximize the value of AppSec testing, from tailoring tests to your needs to ensuring actionable reports, for both defenders and breakers in application security.
Authentication as a Microservice - Portable Customer Identity Management
Explore microservice-based authentication, portable identity management, and JWT security. Learn advantages, pitfalls, and best practices for decoupling user data in modern applications.
Human Factors That Influence Secure Software Development
Explores human factors influencing secure software development, including environmental conditions, developer characteristics, and team dynamics. Discusses strategies to identify and mitigate vulnerability-prone code before issues arise.
Battle Tested Application Security
Insights on building effective Application Security programs, focusing on security culture, defensive capabilities, and organizational empowerment across different environments.
Flying Above the Clouds - Securing Kubernetes
Explore Kubernetes security, from container isolation to authentication and authorization. Learn to build resilient cloud-native systems and deploy secure services in a distributed environment.
Breaking Fraud and Bot Detection Solutions
Demystifying browser fingerprinting and user behavior tracking in fraud detection, exploring vulnerabilities, and sharing real-world implementation flaws in bot prevention systems.
Serverless Infections - Malware Just Found a New Home
Explore serverless security risks through a live demo of RCE attacks, data infiltration, and self-duplicating malware in cloud environments. Learn best practices for securing serverless architectures.
Deserialization - What, How and Why Not
Explore insecure deserialization risks, vulnerabilities, and prevention techniques through code examples and live demos, focusing on Java but applicable to other languages.
A New Framework to Automate MSTG and MASVS in Your CI/CD Pipeline
Automate mobile app security testing using BDD and UI automation frameworks. Integrate OWASP MASVS/MSTG into CI/CD pipelines for faster, repeatable security checks at DevOps speed.
Web Application Compromise Mitigation with Crypto Anchoring - AppSecUSA
Explore crypto anchoring as a solution to protect sensitive data from breaches, paired with effective monitoring for enhanced web application security.
My Journey Through Building an Advanced Bot Detection Product
Explore the evolution of bot detection and management, focusing on fraudulent activities, detection techniques, and best practices for protecting e-commerce and finance websites.
Scratching the Surface of Your CD - Continuous Delivery and Application Security Challenges
Explore strategies for integrating continuous security testing into fast-paced Continuous Delivery environments, addressing challenges and streamlining processes for modern development workflows.
The Anatomy of a Secure Web Application in Java Using Spring Security and Apache Fortress
Practical guidance on implementing secure Java web applications using Spring Security and Apache Fortress. Covers authentication, authorization, and confidentiality controls with hands-on demos and code examples.
Security as a Service - Work Where You Engineers Live
Integrating security into existing development workflows for efficient vulnerability management and faster response times. Learn how to leverage automation and project tracking tools to enhance security practices.
Open Source Security Tools for Kubernetes Applications
Explore open-source tools for securing Kubernetes applications, covering image scanning, runtime security, and anomaly detection. Learn practical strategies for maintaining a secure cloud-native environment.
Lessons from Integrating Third Party Library Scanning in DevOps Workflow
Integrating third-party library scanning in DevOps: automation strategies, architectural choices, and best practices for secure development at scale. Tips for seamless implementation and measuring success.
SCORE Bot - Shift Left, at Scale!
Automated security code review tool for early detection of organization-specific vulnerabilities, integrated with GitHub PR process. Provides real-time feedback and actionable guidance for developers.
Value Driven Threat Modeling
Learn efficient, value-driven threat modeling techniques to embed secure design in products from the start. Discover how to integrate security into agile development and prioritize vulnerabilities effectively.