Microsoft IT - Secure Journey to IPv6-Only
Explore Microsoft's transition to IPv6-only networks, covering industry pressures, implementation challenges, and key lessons learned in this technical deep dive.
Introducing Faction - A Modern, Powerful, Multiplayer C2 Framework
Explore Faction, a modern multiplayer C2 framework. Learn its modular design, accessibility, and key features through live demos and in-depth explanations of its components and functionality.
A Diet of Poisoned Fruit - Designing Implants and OT Payloads for ICS Embedded Devices
Explore designing implants and payloads for ICS embedded devices, covering discovery, attack design, and damage stages in cyber-physical attacks on industrial control systems.
Hardware Side Channel Attacks on the Cheapest
Explore side channel attacks on low-cost hardware, covering power analysis, encryption vulnerabilities, and practical demonstrations. Learn acquisition techniques and countermeasures.
Hitting the Gym - The Anatomy of a Killer Workout
Explore security vulnerabilities in smart fitness equipment, focusing on treadmills. Learn about potential risks, attack surfaces, and implications for both users and corporate environments.
Is 2019 Finally the Year of Linux on the Desktop? And What About v6-Only in WiFi Networks?
Explore IPv6-only networks, their benefits, and challenges through real-world case studies and application testing, including popular gaming and communication platforms.
Vehicle Alarms' Insecurity and Something Else
Explore vulnerabilities in vehicle alarm systems, including signal transmitters, deactivation methods, and remote control weaknesses. Learn about code knocking and motion detector flaws.
Sneaking Past Device Guard
Explore techniques to bypass Device Guard, focusing on lateral movement, trusted locations, and ActiveScript vulnerabilities in Windows environments.
Medical Device Security - Please Don't Be Patient
Explore medical device security challenges, classifications, and vulnerabilities in healthcare organizations. Learn about regulatory guidelines and real-world examples of device defects and potential exploits.
HackDMI
Explore HackDMI: Learn about HDMI protocols, CEC messaging, and ARC. Discover vulnerabilities in HDMI implementations and gain insights into fuzzing techniques for digital media interfaces.
Comparing WAF and RASP - Why?
Explore the differences and complementary roles of WAF and RASP in application security, understanding their strengths and limitations for comprehensive protection.
API Security - Is it the New Application Attack Surface and How to Secure at Enterprise Scale
Explore API security challenges, threats, and enterprise-scale solutions. Learn about modern attack surfaces, recent breaches, and effective strategies for protecting sensitive data in API-driven architectures.
Privacy Impact Assessments - How Much Privacy Is Enough?
Explore privacy impact assessments, their methodologies, and how they differ from security risk assessments. Learn to model and measure privacy impacts for effective Privacy by Design implementation.
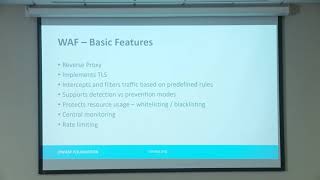
Your Frontier Defense - Understanding Web Application Firewalls
Explore WAF options, features, and challenges across cloud providers and self-managed solutions for enhanced web application security and defense-in-depth strategies.
Doing This One Crazy Thing Will Change Your AppSec Program Forever
Discover how to revolutionize your AppSec program through effective communication, prioritization, and innovative strategies for securing software development.
Developing and Managing an OWASP Project - Projects 101
Learn to create, manage, and grow an OWASP project. Explore naming, sponsorship, levels, services, and resources for successful open-source security initiatives.
Writing Policies That Aren't Miserable for Everyone Involved
Innovative approach to creating effective security policies that are easy to understand, implement, and comply with, improving overall organizational security and employee engagement.
Using the Threat Modeling Manifesto to Build an Enterprise Threat Modeling Program
Learn to build an enterprise threat modeling program using the Threat Modeling Manifesto. Discover key principles, benefits, and practical tips for implementing effective security practices across your organization.
The Final Frontier - Automating Dynamic Security Testing
Automating dynamic security testing: strategies for efficient, scalable DAST integration in software delivery pipelines, addressing challenges and trade-offs for seamless DevSecOps implementation.
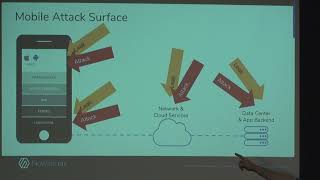
Insiders Guide to Mobile AppSec with OWASP MASVS
Explore mobile app security essentials using OWASP MASVS, covering data storage, network issues, authentication, and anti-tampering. Learn practical tools and tactics for effective mobile pen testing and security assessment.
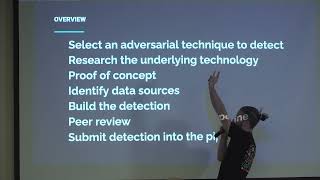
Detection Engineering Methodologies
Comprehensive methodology for engineering effective threat detections, covering structure, processes, and technologies for a successful detection program.