Conclusions & Key Takeaways from Black Hat Asia 2017
Explore key cybersecurity insights from Black Hat Asia 2017, covering topics like attacker specialization, machine learning, digital nations, and biometrics.
Bypassing Clang's SafeStack for Fun and Profit
Explore SafeStack's vulnerabilities and potential bypasses in Clang compiler, analyzing implementation weaknesses and demonstrating practical exploitation techniques for memory corruption.
Anti-Plugin - Don't Let Your App Play as an Android Plugin
Explore Android plugin technology's security risks and learn defensive strategies to protect your app from unauthorized loading and execution as a plugin.
Cross the Wall - Bypass All Modern Mitigations of Microsoft Edge
Explore techniques to bypass ASLR, DEP, and CFG exploit mitigations in Microsoft Edge on Windows 10, even with arbitrary address read/write capabilities.
Daily-Life Peeper - Bug Hunting and Exploit Techniques in IoT
Explore IoT security vulnerabilities, bug hunting techniques, and exploit methods. Learn to identify and address risks in everyday connected devices for improved cybersecurity.
Cyber Judo - Offensive Cyber Defense
Learn offensive techniques to enhance your organization's cyber defense against advanced, targeted attacks from security experts Itai Grady and Tal Be'ery.
What's on the Wireless - Automating RF Signal Identification
Explore automated RF signal identification techniques for monitoring diverse wireless technologies in organizational environments, enhancing security and management capabilities.
Evilsploit - A Universal Hardware Hacking Toolkit
Innovative method for hardware hacking using connection matrix, enabling arbitrary analog-alike connections and versatile bus interfacing for comprehensive hardware exploitation.
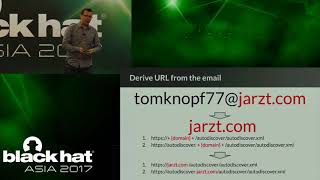
All Your Emails Belong to Us - Exploiting Vulnerable Email Clients via Domain Name Collision
Explore email vulnerabilities and domain name collisions as potential security threats, focusing on protecting email accounts from advanced persistent threats and exploitation techniques.
Mobile-Telephony Threats in Asia
Explore the mobile-telephony cybercrime ecosystem in Asia through a 7-month honeypot study, revealing SMS scams, fraudulent calls, and VoIP phishing attempts. Gain insights into real threats facing mobile users.
Securely Implementing Network Protocols - Detecting and Preventing Logical Flaws
Explore model-based testing techniques to detect logical bugs in SSL/TLS and Wi-Fi implementations, enhancing network protocol security and implementation.
Orange is the New Purple - How and Why to Integrate Development Teams with Red - Blue Teams to Build More Secure Software
Explore a new paradigm for integrating development teams with offensive and defensive teams to enhance software security throughout the development lifecycle, fostering knowledge sharing and strengthening defenses.
Myth and Truth About Hypervisor-Based Kernel Protector - The Reason Why You Need Shadow-Box
Explore hypervisor-based kernel protection, its limitations, and the need for higher-privilege solutions like Shadow-Box to combat rootkits and kernel exploits effectively.
Hack Microsoft Using Microsoft Signed Binaries
Explore advanced hacking techniques using Microsoft-signed tools, including PowerShell and debuggers, to achieve various attacks and persistence on Windows systems.
Never Let Your Guard Down - Finding Unguarded Gates to Bypass Control Flow Guard with Big Data
Explore techniques to bypass Control Flow Guard in Windows using big data analysis, focusing on unguarded gates and indirect branches for enhanced security understanding.
Betting Against the House - Security and Stability When the Odds are Against You
Insights on designing and securing enterprise networks under constraints, drawing from Black Hat's network experiences. Covers evolution, challenges, and future directions in network management.
MASHaBLE - Mobile Applications of Secret Handshakes Over Bluetooth LE
Explore cryptographic secret handshakes for mobile devices using Bluetooth LE, enabling mutual authentication between untrusted parties in virtual secret communities.
CTX - Eliminating BREACH with Context Hiding
Explore advanced techniques to mitigate BREACH attacks in web applications using compression and encryption. Learn about Context Hiding and its implementation in practical scenarios.
Delegate to the Top - Abusing Kerberos for Arbitrary Impersonations and RCE
Explore Kerberos delegation vulnerabilities in Windows networks, learning techniques for unauthorized impersonation and remote code execution. Gain insights into potential security risks and mitigation strategies.
Detach Me Not - DoS Attacks Against 4G Cellular Users Worldwide from Your Desk
Explores DoS attacks on 4G cellular networks, revealing vulnerabilities in mobile communication systems and their potential for user tracking and manipulation. Discusses implications for security and privacy in telecommunications.
Open Sourcing Automotive Diagnostics
Explore automotive diagnostic protocols, their applications in research and repair, and learn about open-source tools for interacting with vehicle systems.