Rough and Ready - Frameworks to Measure Persistent Engagement and Deterrence
Explore frameworks for assessing U.S. cybersecurity policy effectiveness, focusing on measuring persistent engagement and deterrence strategies in national defense.
Managing for Success - Maintaining a Healthy Bug Bounty Program Long Term
Strategies for maintaining an effective bug bounty program, focusing on incentives, communication, and researcher relationships to ensure high-value vulnerability reports and long-term success.
Ghidra - Journey from Classified NSA Tool to Open Source
Explore NSA's journey in developing and open-sourcing Ghidra, a powerful software reverse engineering framework. Learn about its features, impact, and future developments.
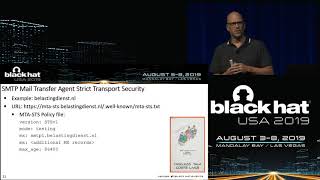
How to Detect that Your Domains are Being Abused for Phishing by Using DNS
Learn to protect your domains from phishing attacks using DNS and email security protocols like SPF, DKIM, and DMARC. Discover advanced techniques for detecting and preventing domain abuse.
Bounty Operations - Best Practices and Common Pitfalls to Avoid in the First 6-12 Months
Insights from experienced bug bounty managers on program operations, triage strategies, and common vulnerabilities. Learn best practices and avoid pitfalls for successful bounty programs.
The Future of ATO
Exploring the evolving landscape of Account Takeover (ATO) attacks, focusing on emerging threats, sophisticated techniques, and strategies to protect user accounts in the digital age.
Zombie Ant Farming - Practical Tips for Playing Hide and Seek with Linux EDRs
Explore techniques to evade Linux EDRs, including using approved executables as decoys and leveraging dynamic ELF loader primitives for stealthy post-exploitation capabilities.
Debug for Bug - Crack and Hack Apple Core by Itself
Explore Apple kernel vulnerabilities through fuzzing, including double free and out-of-bounds issues. Learn about debugging and fuzzing techniques for uncovering security flaws in Apple's core systems.
Operational Templates for State-Level Attack and Collective Defense of Countries
Explore templates for nation-level cyber attacks and defense strategies, examining various time horizons, attribution levels, and collective approaches to protect countries in cyberspace.
Infighting Among Russian Security Services in the Cyber Sphere
Explore the complex dynamics of Russian security agencies in cyberspace, examining conflicts, international campaigns, and their implications for global cybersecurity.
Exploring the New World - Remote Exploitation of SQLite and Curl
Discover new methods for finding vulnerabilities in SQLite and Curl through fuzzing and manual auditing, including insights on "Magellan" and "Dias" vulnerabilities.
Critical Zero Days Remotely Compromise the Most Popular Real-Time OS
Explore critical vulnerabilities in VxWorks, a popular real-time OS, and their potential for remote network breaches and device exploitation. Includes live demonstrations on various devices, including medical equipment.
How We Created the First SHA-1 Collision and What it Means for Hash Security
Explore the creation of the first SHA-1 collision, its implications for hash security, and the challenges faced in developing a meaningful payload and scaling computation.
Behind the Plexiglass Curtain - Stats and Stories from the Black Hat NOC
Insider insights into Black Hat's network operations: statistics, anecdotes, and revelations from the Network Operations Center team's annual debrief.
An ACE Up the Sleeve - Designing Active Directory DACL Backdoors
Explore Active Directory DACL backdoors, their offensive potential, and stealth techniques. Learn about control relationships, elevation paths, and persistence methods in AD objects.
Cracking the Lens - Targeting HTTP's Hidden Attack-Surface
Explore hidden attack surfaces in modern web infrastructure, focusing on transparent systems for performance and analytics. Learn to identify and exploit overlooked vulnerabilities.

Broadpwn - Remotely Compromising Android and iOS via a Bug in Broadcom's Wi-Fi Chipsets
Explore a critical Wi-Fi vulnerability affecting millions of Android and iOS devices, its technical details, and potential for remote exploitation without user interaction.
Man-in-the-SCADA - Anatomy of Data Integrity Attacks in Industrial Control Systems
Explore data integrity attacks in industrial control systems, focusing on attacker perspectives and strategies for unauthorized access to control networks and equipment.
Conclusions and Key Takeaways from Black Hat Europe 2016
Insightful discussion on critical InfoSec trends and their impact on future strategies, featuring industry experts at Black Hat Europe 2016's closing session.
Drop the ROP - Fine-Grained Control-Flow Integrity for the Linux Kernel
Explore fine-grained Control-Flow Integrity for Linux kernel security, addressing ROP attacks and dynamic kernel modules. Learn advanced mitigation techniques and implementation challenges.
Exploiting USB-IP in Linux
Explore USB/IP vulnerabilities in Linux, including buffer overflow and data injection. Learn about architecture, protocol, and security implications of this USB device sharing framework.