A New Criterion for Avoiding the Propagation of Linear Relations Through an Sbox
Explore a novel criterion for preventing linear relation propagation in cryptographic Sboxes, enhancing security in symmetric encryption algorithms.
Towards Secure Distance Bounding
Explore secure distance bounding protocols, their applications in relay attack prevention, and key concepts like interactive distance measurement and noise considerations in cryptographic systems.
Full Plaintext Recovery Attack on Broadcast RC4
Cryptographic analysis of RC4 cipher vulnerabilities, focusing on plaintext recovery techniques in broadcast scenarios.
Attacks and Security Proofs of EAX-Prime
Explore attacks and security proofs of EAX-Prime, a cryptographic algorithm, in this technical presentation from FSE 2013 by leading researchers in the field.
Higher-Order Side Channel Security and Mask Refreshing
Explore advanced techniques for enhancing side channel security in cryptographic implementations, focusing on mask refreshing strategies and higher-order protections.
Security Analysis of PRINCE
Comprehensive analysis of PRINCE cipher's security, exploring vulnerabilities and strengths in cryptographic design for lightweight applications.

Reflection Cryptanalysis of PRINCE-Like Ciphers
Explore reflection cryptanalysis techniques for PRINCE-like ciphers, examining vulnerabilities and potential attacks on these symmetric encryption algorithms.
On Symmetric Encryption with Distinguishable Decryption Failures
Explore symmetric encryption with distinguishable decryption failures, examining implications for cryptographic security and practical applications in modern systems.
A Low Data Complexity Attack on the GMR-2 Cipher Used in the Satellite Phones
Explore a cryptographic attack on the GMR-2 cipher in satellite phone communications, examining its low data complexity and implications for security.
Impossible Plaintext Cryptanalysis and Probable Plaintext Collision Attacks of 64-Bit Block Ci
Explores cryptanalysis techniques for 64-bit block ciphers, including impossible plaintext and probable plaintext collision attacks, with applications to real-world scenarios and countermeasures.
Failures of Secret Key Cryptography
Explore failures in secret key cryptography, including vulnerabilities, attacks, and optimization challenges, with insights from Daniel Bernstein's expert analysis.
Constant Round MPC with Fairness and Guarantee of Output Delivery
Explore advanced cryptographic protocols for secure multi-party computation, focusing on fairness and guaranteed output delivery in constant rounds.
Links Among Impossible Differential, Integral and Zero Correlation Linear Cryptanalysis
Explore connections between advanced cryptanalysis techniques: impossible differential, integral, and zero correlation linear methods. Gain insights into their relationships and applications.

Tweaking Even Mansour Ciphers
Explore modifications to Even-Mansour ciphers, examining their impact on security and efficiency in cryptographic systems.
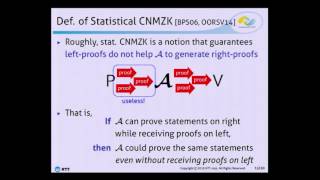
Statistical Concurrent Non-Malleable Zero Knowledge from One-Way Functions
Explore advanced cryptographic concepts: statistical concurrent non-malleable zero-knowledge proofs derived from one-way functions in this concise theoretical presentation.
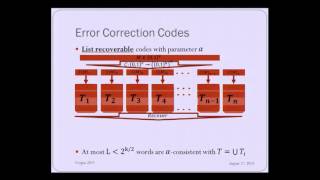
Parallel Hashing via List Recoverability
Explore parallel hashing techniques, focusing on list recoverability and its applications in cryptographic constructions like Merkle trees and domain extension schemes.
Multi Key Security - The Even Mansour Construction Revisited
Explore block cipher design, key scheduling, and multi-key security in cryptography, focusing on the Even-Mansour construction and its advantages in frequent rekeying scenarios.
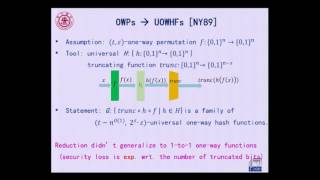
Almost Optimal Constructions of UOWHFs from 1 to 1, Regular One Way Functions and Beyond
Explore advanced cryptographic constructions, focusing on Universal One-Way Hash Functions (UOWHFs) derived from regular one-way functions, with insights into optimal implementations and extensions.
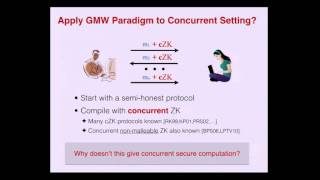
Concurrent Secure Computation with Optimal Query Complexity
Explore concurrent secure computation, focusing on optimal query complexity, circumventing impossibility results, and improving simulation techniques in cryptographic protocols.
A Simpler Variant of Universally Composable Security for Standard Multiparty Computation
Simplified approach to universal composability in multiparty computation, addressing complexity issues and offering a more accessible framework for secure protocols.
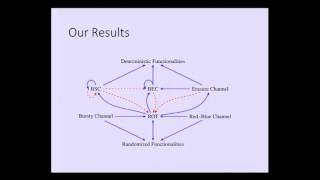
Cryptography with One Way Communication
Explore noise in cryptography, one-way communication models, and applications like BEC self-transformation. Discover results, impossibilities, and open problems in this field.