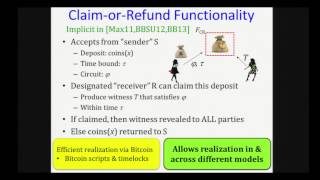
How to Use Bitcoin to Design Fair Protocols
Learn to design fair protocols using Bitcoin, exploring concepts like fair exchange, claim-or-refund functionality, and secure computation with penalties in this cryptography-focused talk.
On the Implausibility of Differing-Inputs Obfuscation and Extractable Witness Encryption with Auxiliary Input
Explore cryptographic challenges in differing-inputs obfuscation and extractable witness encryption with auxiliary input, presented by experts at Crypto 2014.
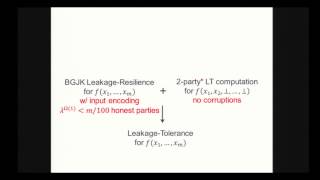
Leakage-Tolerant Computation with Input-Independent Preprocessing
Explore leakage-tolerant computation techniques with input-independent preprocessing, focusing on multi-party computation models and innovative encoding methods for enhanced security.
On the Wrong Key Randomisation and Key Equivalence Hypotheses in Matsui's Algorithm 2
Explores cryptographic hypotheses in Matsui's Algorithm 2, focusing on Wrong Key Randomisation and Key Equivalence, providing insights for cryptanalysts and researchers.
Related-Key Attacks Against Full Hummingbird-2
Explore cryptographic vulnerabilities in Hummingbird-2 through related-key attacks, as presented by Markku-Juhani Olavi Saarinen at FSE 2013.
Masking Tables - An Underestimated Security Risk
Explore masking tables in cryptography, their security risks, and countermeasures. Learn about AES, load index masking, and random table techniques for enhanced data protection.
Rotational Cryptanalysis of Round-Reduced Keccak
Explore rotational cryptanalysis of Keccak, focusing on round-reduced variants. Learn about innovative techniques, representation methods, and complexity analysis in this cryptographic research.
A Framework for Automated Independent-Biclique Cryptanalysis
Explore automated independent-biclique cryptanalysis, a framework for enhancing cryptographic security analysis through efficient algorithmic techniques.
Complementing Feistel Ciphers
Explore complementation in Feistel ciphers, its applications, and implications for cryptography. Learn about generalization, key scheduling, and practical complexities in cipher design.
Secure Message Authentication Against Related-Key Attack
Explore message authentication techniques resilient to related-key attacks, enhancing cryptographic security in modern communication systems.
Cryptanalysis of Round-Reduced LED
Explore cryptanalysis techniques for round-reduced LED cipher, including differential characteristics, complexity analysis, and advanced attack methods.
Towards Understanding the Known-Key Security of Block Ciphers
Explore known-key security of block ciphers, covering differentiability, nonkey settings, and general indifference. Gain insights into cryptographic concepts and their implications.
Time-Memory Trade-Offs for Near-Collisions
Explore time-memory trade-offs in near-collision attacks on hash functions, analyzing complexity and discussing practical applications in cryptography.
Partial-Collision Attack on the Round-Reduced Compression Function of Skein-256
Explore a cryptographic analysis of Skein-256's compression function, examining partial-collision attacks and their implications for the algorithm's security.
Tweakable Blockciphers with Asymptotically Optimal Security
Explore asymptotically optimal security in tweakable blockciphers, covering parameter hash functions, inquisition questions, and random permutation distribution views.
Exhausting Demirci-Selçuk Meet-in-the-Middle Attacks Against Reduced-Round AES
Explore advanced cryptanalysis techniques for AES, focusing on meet-in-the-middle attacks and their implications for reduced-round variants of the algorithm.
ALE - AES-Based Lightweight Authenticated Encryption
Explore an innovative AES-based authenticated encryption scheme designed for resource-constrained environments, offering enhanced security and efficiency.
Collision Attacks on Up to 5 Rounds of SHA-3 Using Generalized Internal Differentials
Explores collision attacks on SHA-3 using generalized internal differentials, presenting novel techniques to compromise up to 5 rounds of the cryptographic hash function.
Improving Key Recovery to 784 and 799 Rounds of Trivium Using Optimized Cube Attacks
Optimized cube attacks enhance key recovery for Trivium cipher, pushing boundaries to 784 and 799 rounds. Explore advanced cryptanalysis techniques and their implications for stream cipher security.
Smashing WEP in a Passive Attack
Explore passive attacks on WEP encryption, analyzing vulnerabilities and advanced techniques for breaking wireless security protocols.
Near Collision Attack on the Grain v1 Stream Cipher
Explore a cryptographic analysis of the Grain v1 stream cipher, focusing on near collision attacks and their implications for cipher security.