The State of Morello Software and Projects - POCL'24
Explore the current landscape of Morello software and ongoing projects, gaining insights into the latest developments and advancements in this field.
Morello Cerise - Proving Secure Encapsulation - Work in Progress
Explore Morello Cerise's approach to proving secure encapsulation in this work-in-progress presentation on cutting-edge computer security research.
Lifting Compiler Security Properties to Stronger Attackers: The Speculation Case
Explore compiler security properties against speculative execution attacks, focusing on lifting guarantees to stronger attacker models and developing a formal framework for well-formedness conditions.
Systemd and TPMs: Updates on Disk Encryption, PCR Policy Management, and More
Explore systemd's latest TPM-related features, including disk encryption, PCR policy management, measurement APIs, and event logging.
Address Space Isolation
Explore address space isolation techniques and their implementation in Linux systems for enhanced security and process isolation.
Rage Against The Machine Clear
Explore new root causes of transient execution attacks, including machine clears, and discover novel attack primitives like Floating Point Value Injection and Speculative Code Store Bypass.
Low Level BootROM Protocol Fuzzing Secure Memory Regions
Explore low-level protocol fuzzing for secure microcontrollers, uncovering vulnerabilities in BootROM USB drivers. Learn about a custom fuzzing framework for SPI, I2C, USB, and UART, and its application in hardware security research.
Injectyll-HIDe - Hardware Implants at Scale
Explore hardware implants at scale, focusing on innovative techniques and potential security implications in this cutting-edge presentation on advanced technological vulnerabilities.
Path to Software-Defined Cryptography via Multi-Party Computation
Exploring software-defined cryptography through multi-party computation, addressing enterprise key management challenges and enabling innovation in data protection and privacy.
Non-Crypto Constant-Time Coding
Explore cache attacks, SGX technology, and tools for writing constant-time code to protect confidential data from side-channel vulnerabilities in various computing contexts.
Function Overrides - From a Security Mitigation to a Full-Fledged Performance Feature
Explore Function Overrides in Windows 11, from its origins as a security mitigation to its evolution as a performance feature. Learn about implementation, compiler modifications, and real-world applications.
Getting Physical with USB Type-C - Windows 10 RAM Forensics and UEFI Attacks
Explore embedded microcontrollers in modern devices, focusing on the Surface Aggregator Module. Learn about security, firmware updates, and potential hardware implants in this deep dive into low-level system architecture.
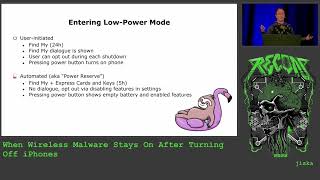
When Wireless Malware Stays on After Turning Off the Phone
Explore iPhone's wireless capabilities after shutdown, including Find My and Digital Car Key. Learn about potential security risks and firmware modifications for low-power Bluetooth malware.
Building Hardened IoT Implementations With LangSec
Explore Language-theoretic security for IoT, focusing on input recognition and processing separation. Learn about parser combinators, test case generation, and implementation in AMQP protocol for robust IoT systems.
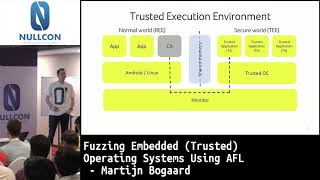
Fuzzing Embedded - Trusted Operating Systems Using AFL
Explore fuzzing techniques for Trusted Execution Environments using AFL, focusing on OP-TEE. Learn about challenges, coverage tracking, and creating initial inputs for effective embedded system security testing.
The Windows Sandbox Paradox
Explore Windows Sandbox security with James Forshaw, uncovering paradoxes and vulnerabilities in Microsoft's isolation technology. Gain insights into logical flaws and potential exploits.
A Kernel Hacker Meets Fuchsia OS
Explore Fuchsia OS from a security perspective as a Linux kernel expert examines its architecture, design principles, and potential vulnerabilities, offering insights for both developers and security professionals.
Hardware Security - Foundational Block of Cyber Battlefield
Panel discussion on hardware security as a foundational element of cybersecurity, featuring experts from healthcare, research, and defense sectors exploring challenges and strategies in this critical field.
Hardware Attack Vectors
Explore hardware-based attack vectors including HID, IR, radio, and bus protocol attacks, with demonstrations for each technique in computer security.
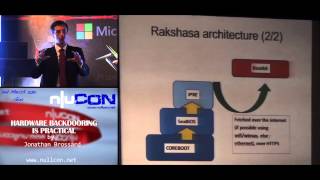
Hardware Backdooring is Possible
Demonstration of permanent hardware backdooring using Rakshasa malware, exploring BIOS vulnerabilities and implications for computer security and forensics practices.
The Quest to Memory Safety
Exploración de vulnerabilidades de memoria y estrategias para prevenirlas, enfocándose en limitaciones de lenguajes de programación y mejoras necesarias para desarrollar código más seguro.