CyberPhysical Systems Security - Trends, Challenges & Opportunities
Expert panel discusses trends, challenges, and opportunities in cyberphysical systems security, focusing on industrial control systems and IIoT in automotive and manufacturing sectors.
Rapid Threat Model Prototyping - Threat Modeling for Agile & DevOps
Learn rapid threat model prototyping for Agile and DevOps environments. Explore security architectural analysis and design techniques to enhance your secure software development lifecycle.
Securing ICS-SCADA Systems
Explore vulnerabilities in ICS-SCADA systems for critical infrastructure, comparing IT and OT security approaches. Learn from an expert about protecting industrial control systems against sophisticated cyber attacks.
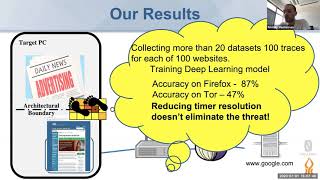
Robust Website Fingerprinting Through Cache Occupancy Channel
Explore website fingerprinting attacks using cache side-channel techniques to compromise user privacy, even on secure networks like Tor. Learn about this novel approach from cybersecurity researcher Anatoly Shusterman.
Building a Security Platform with Elastic Stack - Part 1
Learn to build a security platform using Elastic Stack. Explore basic components, data ingestion tools, data management, and cluster security. Gain insights from an experienced developer on leveraging SIEM for effective security monitoring.
Secrets Management Using Hashicorp Vault
Explore Hashicorp Vault for secure secrets management with expert Rohit Salecha. Learn key concepts, implementation strategies, and best practices for protecting sensitive data in your applications and infrastructure.
Hacking Automatically - Applying Program Analysis to IoT
Discover how program analysis can uncover vulnerabilities in IoT devices. Learn about firmware analysis challenges, memory corruption patterns, and see 20 real-world examples of security flaws identified through automated techniques.
Cloud as an Attack Vector
Explore how cybercriminals exploit cloud services as attack vectors, including shadow IT risks and malware delivery. Learn about emerging threats and security implications in the rapidly evolving cloud landscape.
Dissecting Rotten Apples - macOS Malware Analysis
Comprehensive exploration of macOS malware analysis, covering system architecture, common malware behaviors, and real-world sample demonstrations. Ideal for security researchers and IT professionals.
Hardware Backdooring is Possible
Demonstration of permanent hardware backdooring using Rakshasa malware, exploring BIOS vulnerabilities and implications for computer security and forensics practices.
Career Opportunities in Information Security
Explore diverse career paths in information security with insights from a seasoned professional. Learn about key roles, skills, and opportunities in this rapidly evolving field.
Reverse Engineering Satellite Based IP Content Distribution
Reverse engineering satellite IP content delivery: from reception to packet analysis, error correction, and high bitrate handling. Culminates in creating a Linux-based client mimicking commercial versions.
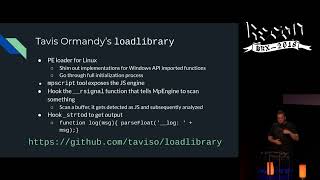
Reverse Engineering Windows Defender's JavaScript Engine
Reverse engineering Windows Defender's JavaScript engine: analysis, functionality, tooling, and potential vulnerabilities in MpEngine.dll's core antivirus system.
#Eko2020 BSDar: Instalación, configuración y administración de OpenBSD en una VM (hands-on)
Guía práctica para instalar, configurar y administrar OpenBSD en una máquina virtual, con comandos y recursos adicionales proporcionados por la comunidad BSDar en #Ekoparty 2020.
Introducción al Mundo BSD
Introducción a los sistemas operativos BSD, sus variantes y aplicaciones. Presentación de la comunidad argentina BSDar para entusiastas y profesionales interesados en esta familia de sistemas.
Security Open Source Tools in Cloud Native
Explora vulnerabilidades en contenedores y herramientas de código abierto para DevSecOps en entornos cloud native. Aprende mejores prácticas y técnicas para detectar errores de configuración y mejorar la seguridad.
Pivoting and Exploitation in Docker Environment
Demostración de técnicas de pivoting, explotación y escalada de privilegios en entornos Docker con múltiples redes. Incluye metodologías de pentest y superación de obstáculos en diferentes configuraciones de red.
AudioNet - A Deep Learning Convolutional Approach to Audio Spoofing Detection
Explore deep learning techniques for audio spoofing detection in biometric security systems, addressing the rise of online fraud and the need for robust anti-spoofing tools.
Lemon Booster - Automatizando desde la UI
Automatización del reconocimiento en programas de Bug Bounty con Lemon Booster: herramienta con interfaz visual para ejecutar, analizar y monitorear resultados, agilizando el proceso de búsqueda de vulnerabilidades.
Keep Calm and Play with Qubits
Desmitificación de la computación cuántica y su impacto en la ciberseguridad. Demostración en vivo del funcionamiento real de las computadoras cuánticas, alentando a investigadores a explorar y crear con esta tecnología.
#Eko2020 Workshop | Felipe Duarte: Threat Intelligence, the Malware Analysis Way
Aprende a automatizar el análisis de malware utilizando herramientas como debuggers, disassemblers y sandboxes. Construye tus propias herramientas para detectar y analizar amenazas de forma eficiente.