Put a Socket in It - Understanding and Attacking Sockets on Android
Explore Android socket programming, security implications, and techniques for identifying and analyzing sockets. Learn about different socket types and their uses in Android development.
Analyzing DNS Traffic for Malicious Activity Using Open Source Logging Tools
Learn to detect malicious DNS activity using open-source logging tools. Gain practical skills for network security and threat analysis.
Analyzing DNS Traffic for Malicious Activity Using Open Source Logging Tools
Explore DNS traffic analysis for malicious activity using open-source logging tools. Learn about log processing, indexing, and visualization to detect threats like DNS amplification and data exfiltration.
The Attackers Dictionary
Explore attacker strategies, password security, and honeypot research. Gain insights into credential attacks, RDP vulnerabilities, and ethical considerations in cybersecurity research.
I Got You - Using Honeypots for Network Security Monitoring
Explore network security monitoring with honeypots, learning effective techniques to detect and analyze potential threats in your digital infrastructure.
Micro Segmentation and Security - The Way Forward
Explore micro-segmentation and zero trust principles for enhanced network security, reducing attack surfaces and lateral movement in modern cybersecurity landscapes.
The Domain Name System - DNS Operation, Threats, and Security Intelligence
Explore DNS operation, threats, and security intelligence. Learn about amplification attacks, proper server configuration, domain hijacking prevention, and leveraging DNS data for threat intelligence and forensic investigations.
DNSSUX - Why DNSSEC Makes Us Weaker
Explore DNSSEC's vulnerabilities, zone enumeration risks, and alternative approaches to DNS security in this critical analysis of current protocols and future solutions.
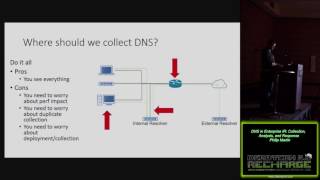
DNS in Enterprise IR Collection Analysis and Response
Explore DNS logging techniques for enterprise incident response, covering data collection, analysis, and response strategies to enhance network security and threat detection.
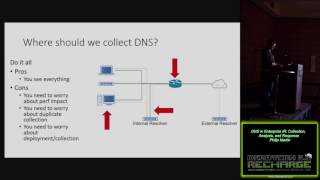
DNS in Enterprise IR Collection Analysis and Response
Explore DNS analysis techniques for enterprise incident response, covering collection tools, infrastructure, and common attack patterns. Learn to leverage RPZ for effective threat mitigation.
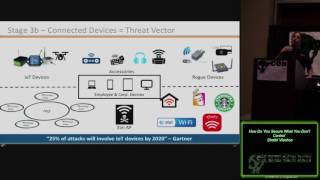
How Do You Secure What You Don't Control
Explore strategies for securing uncontrolled devices in BYOD environments and IoT ecosystems. Learn about the challenges and solutions for managing security risks in modern interconnected systems.
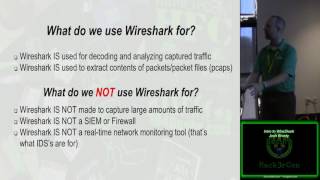
Intro to WireShark
Comprehensive introduction to Wireshark network protocol analyzer, covering packet capture, filtering, and analysis techniques for effective network troubleshooting and security monitoring.
So You've Inherited a Security Department - Now What
Practical strategies for new security department leaders: asset management, information gathering, vulnerability assessment, and team building for effective cybersecurity operations.
Alert All the Things - Network Baselines and Alerts with Bro Scripts
Network monitoring and alerting using Bro scripts to establish baselines and detect anomalies. Learn to enhance security through customized, automated threat detection.
Current State of Virtualizing Network Monitoring
Explore the current state of virtualizing network monitoring, covering prototypes, hardware architecture, logging, and new technologies like containers and Intel X79 XL7.
Stories through Logging - It Was the Best of Logs, It Was the Worst of Logs
Explore effective logging practices for better storytelling and troubleshooting in IT systems. Learn to extract valuable insights from log files and improve system monitoring.
EDNS Client Subnet ECS DNS CDN Magic or Security
Explore EDNS Client Subnet (ECS) and its impact on DNS, CDNs, and security. Learn about the magic and potential risks of this technology in modern networking.
Detecting DNS Anomalies with Statistics
Explore statistical methods for detecting DNS anomalies, including letter analysis, unique queries, and outlier identification. Learn practical tools and techniques for enhancing network security.
Measuring the Efficacy of Real Time Intrusion Detection Systems
Explore techniques for evaluating real-time intrusion detection systems, covering protocols, monitoring, best practices, and data classification to enhance network security effectiveness.
DIY Spy Covert Channels With Scapy And Python
Learn to create covert communication channels using Scapy and Python. Explore techniques for hiding data, constructing protocols, and implementing command and control systems in network traffic.
PANDA Walking Loud in the Cloud - Logan Hicks
Explore PANDA, an open-source cloud networking solution, covering its objectives, features, and architecture. Learn about its performance stack, traffic flow, and global layout.