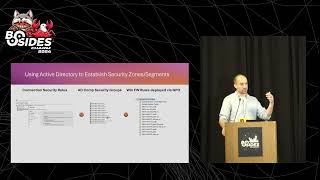
Network Segmentation Using Windows Host-Based Firewall and Group Policy
Master Windows network segmentation using Group Policy to deploy host-based firewall rules, control communication between security zones, and manage endpoints through Active Directory security groups.
Bug Bounty Recon: Bypassing Geographic DNS with Ensemble
Discover how Ensemble revolutionizes bug bounty hunting by bypassing GeoDNS limitations, enabling comprehensive scanning across multiple geographic regions through a distributed cluster of nodes and user-friendly web interface.
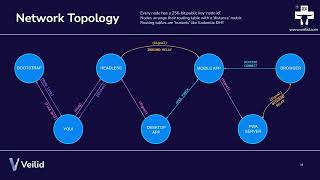
The Internals of Veilid - A New Decentralized Application Framework
Explore the architecture and capabilities of Veilid, an open-source P2P framework enabling secure messaging and decentralized applications through private routing, strong encryption, and cross-platform compatibility.
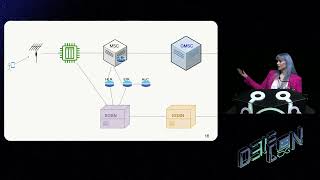
Evolution of Cellular Networks: From 2G to 5G - Understanding Attack Surfaces and Security
Explore the evolution of cellular networks from 2G to 5G, understanding network vulnerabilities, attack surfaces, and security mitigations across each generation of mobile telecommunications.
Unparalleled RDP Monitoring to Reveal Attackers' Tradecraft
Dive into advanced RDP attack monitoring techniques and threat actor behaviors through a unique D&D-themed analysis of cybersecurity tradecraft and defensive strategies.
Malware Design: Abusing Legacy Microsoft Transports and Session Architecture
Explore advanced malware design techniques and covert communication frameworks, focusing on Windows architecture exploitation and maintaining persistent access while evading detection systems.
Leveraging macOS Networking Frameworks to Heuristically Detect Malware
Discover advanced techniques for detecting macOS malware through network monitoring, exploring low-level APIs, private frameworks, and user-mode extensions for comprehensive threat detection.
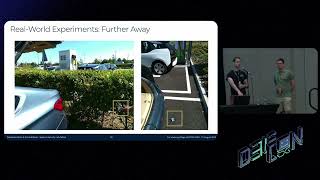
Exploiting Wireless Side Channels in EV Charging Systems - Security Vulnerabilities in CCS and NACS
Explore wireless security vulnerabilities in EV charging systems, focusing on CCS technology, eavesdropping risks, and potential attack vectors through power-line communication signals.
Nine Years of Overlooked MikroTik Pre-Authentication Remote Code Execution Vulnerabilities
Delve into RouterOS's overlooked attack surfaces and discover critical pre-auth RCE vulnerabilities that affected MikroTik devices for 9 years, with insights on detection methodology and security patterns.
Exploiting Cloud Connectivity to Compromise Network-Attached Storage Devices
Uncover critical security vulnerabilities in NAS devices through cloud connectivity exploitation, focusing on WD and Synology systems' authentication weaknesses and remote access vulnerabilities.
Civil Cyber Defense - Protecting Vulnerable Organizations Against Advanced Threats
Discover how civil cyber defenders protect vulnerable organizations, journalists, and activists using OSINT skills and open-source tools while combating human trafficking and surveillance threats.
Defeating VPN Always-On: Security Control Analysis and Bypass Methods
Discover security vulnerabilities in VPN Always-On implementations, exploring bypass techniques and hardening strategies for better network protection and data leak prevention.
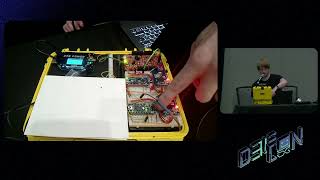
Abusing CAN Bus Specifications for DoS Attacks in Embedded Systems
Explore CAN bus protocol vulnerabilities in automotive systems, focusing on how attackers can exploit metadata fields and protocol specifications to create denial-of-service attacks in embedded systems.
Exploiting Bluetooth Vulnerabilities: From Car Systems to Bank Account Security
Discover how to identify and exploit Bluetooth vulnerabilities in modern vehicles and flight systems, using BlueToolkit framework for testing, with practical tips and new attack vectors for security research.

Measuring the Tor Network - Understanding Network Health and Security Analysis
Dive into the mechanics of Tor's network infrastructure, exploring metrics collection, attack mitigation, and community management strategies for maintaining this vital privacy ecosystem.
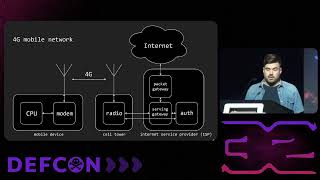
Leveraging Private APNs for Mobile Network Traffic Analysis and Security
Discover how to monitor and control mobile device network traffic using private APNs, enabling affordable security testing and traffic analysis for IoT and mobile devices on 4G/5G networks.
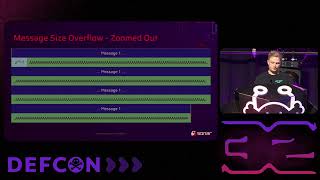
SQL Injection Isn't Dead: Smuggling Queries at the Protocol Level
Explore advanced SQL injection techniques through protocol-level query smuggling, revealing how attackers can bypass security measures and exploit database connections for authentication breaches and data theft.
Vehicle-to-Game: Using Your Car as a Game Controller
Discover how to transform your car into a unique game controller using Python, exploring vehicle networks, CAN bus communication, and diagnostic interfaces for an innovative gaming experience.
Signature-Based Detection Using Network Timing - Malware Traffic Analysis
Explore advanced malware detection techniques using network timing patterns and Python, learning to identify malicious behavior through transaction intervals rather than traditional code signatures.
WPAD Domain Exploitation: Understanding Man-in-the-Middle Attacks Through DNS
Uncover how a single domain purchase can exploit WPAD vulnerabilities, leading to massive-scale man-in-the-middle attacks and compromising hundreds of thousands of internet clients through DNS manipulation.
MaLDAPtive: LDAP Query Obfuscation and De-Obfuscation Techniques
Dive into advanced LDAP query obfuscation techniques and defense strategies, exploring a comprehensive framework for detecting and preventing directory services attacks through custom tokenization and parsing.