How Do You Know You're Done After a Security Fix - Leveraging SBOM Data
Explore approaches for leveraging SBOM data to improve automation and confidence in safety analysis after applying vulnerability fixes in systems with safety considerations.
DevSecOps Best Practices in Cloud Native Computing - CMCC Case Study
探索中国移动通信公司的DevSecOps最佳实践,了解如何将安全无缝集成到云原生开发和运维流程中,提高效率和安全性。
Path to Production: Sustainable Compliance in Strict Environments
Discover strategies for achieving sustainable compliance in highly regulated environments, focusing on DoD practices using Big Bang, Iron Bank, and Kyverno for faster, secure-by-default Kubernetes deployments.
SBOM is Coming - Why You Should Care and How You Can Help
Explore the importance of Software Bill of Materials (SBOM) in cloud-native ecosystems, its impact on security, and how you can contribute to its implementation and adoption.
SBOM: The Rest of the Story - Understanding Software Bill of Materials
Experts discuss Software Bill of Materials (SBOM), addressing misconceptions, sharing challenges, and exploring implementation strategies for enhanced software supply chain security.
Application Security for Better Business Value - Expert Insights
Experts discuss how application security practices in cloud-native environments can reduce risks, enhance compliance, and drive innovation, leading to improved business value.
Real World SPIFFE Scenarios and Outcomes
Explore real-world scenarios and outcomes of deploying SPIFFE across infrastructure, including benefits for security, interoperability, compliance, and audibility in distributed systems.
Attacking and Defending Kubernetes TEE Enclaves in Critical Infrastructure
Explore Kubernetes TEE enclaves for critical infrastructure security. Learn attack and defense strategies, threat modeling, and compliance benefits for various regulations.
AI and Data Security Innovation Showcase
Experts discuss risks and benefits of generative AI in companies, focusing on compliance, privacy, and security. Includes presentations from emerging AI and data security firms.
Understanding the Sec in DevSecOps: Beyond Just Shifting Left
Explore attack vectors, preventive measures, and compliance strategies in DevSecOps. Learn innovative approaches to enhance software security beyond shifting left.
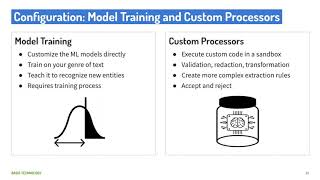
Customizing Rosette Entity Extractor to Remove PII
Demonstration of customizing Rosette Entity Extractor to redact personally identifiable information, showcasing practical application of PII removal techniques.
RAFIA - A Roadmap for Certifying Open Source in Safety-Relevant Systems
Explore RAFIA methodology for certifying open source in safety-critical systems. Learn risk analysis, automated testing, fault injection, mitigation, and compliance steps for embedded Linux-based operating systems.
OWASP ZAP and DeepFactor - Continuous AppSec Observability for DevSecOps
Explore how DeepFactor's observability enhances OWASP ZAP for comprehensive DevSecOps, detecting security risks in modern cloud-native applications through advanced event monitoring.
Loom Security Journey - Getting Over the Finish Line
Explore the security journey of a startup, from building essential functions to navigating a smooth acquisition. Gain insights into critical security measures during rapid growth and M&A processes.
Cyber Resilience Act Impact on Device Manufacturers
Explore the Cyber Resilience Act's impact on device manufacturers, focusing on cybersecurity requirements, vulnerability management, and compliance strategies.
Understanding the Cyber Resilience Act - Key Obligations and Compliance
Explore the EU's Cyber Resilience Act and its impact on IT industry compliance. Learn key obligations and prepare your organization for upcoming regulatory changes.
Looking at Security with Cat Eyes - The OpenKAT Project
Explore integrated security projects bridging technical checks, compliance, automated warnings, and non-repudiation in the OpenKAT initiative.
Building a Security Audit Logging System on a Shoestring Budget
Learn to build a robust, security-focused audit logging system for fast-growing companies with limited resources. Discover cost-effective strategies and lessons from combining software engineering and hacker culture.
Perimeter Security is Dead: Moving Towards Zero Trust Networks
Explore why perimeter security is outdated and dangerous, and learn how to implement a zero trust approach in company networks for improved information security.
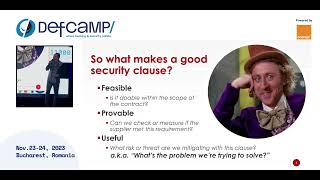
AppSec Contractual Sins - Identifying and Addressing Security Issues in Contracts
Explore common AppSec contractual pitfalls and best practices for securing software development agreements in this DefCamp 2023 presentation by Canon's EMEA Information Security Manager.
Hacking Trains - Remote Access Vulnerabilities in Railway Systems
Exploring railway cybersecurity vulnerabilities through OSINT, assessing potential remote access risks, and evaluating the ease of exploiting these weaknesses for malicious purposes.