Embedding GDPR into the Software Development Lifecycle
Practical guide to integrating GDPR requirements into software development lifecycle, covering privacy awareness, risk analysis, secure coding, threat modeling, and breach notification processes.
What Shall We Do With a Vendor SBOM? - Understanding Software Bill of Materials
Explore the practical applications of Software Bill of Materials (SBOM) in cybersecurity, covering procurement, vulnerability disclosure, threat intelligence, and forensics.
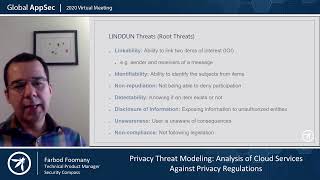
Privacy Threat Modeling - Analysis of Cloud Services Against Privacy Regulations
Learn to analyze cloud services for privacy threats and regulatory compliance using threat modeling techniques, enhancing your ability to protect sensitive data.
A Risk-Based Approach to API Security
Explore a risk-based approach to API security, focusing on threat modeling, vulnerability assessment, and mitigation strategies to enhance your organization's API protection.
2013 AppSec Guide and CISO Survey - Making OWASP Visible to CISOs
Insights from OWASP's 2013 AppSec Guide and CISO Survey, focusing on application security governance, risk management, and investment strategies for Chief Information Security Officers.
How to Govern and Maintain Compliance Using Open Source Identity Management Components
Explore open-source identity management with midPoint for efficient governance, compliance, and automation. Learn integration, role-based access control, and advanced features through practical scenarios and demos.
Building a Security Culture - Digital Transformation and Breach Prevention
Explore strategies for creating a robust security culture amid digital transformation, addressing cloud risks, BYOD challenges, and persistent breaches despite technological investments.
Design Approaches for Security Automation
Explore criteria for designing and evaluating security automation tools, including build vs. buy decisions, deployment strategies, and effective implementation for organizational needs.
Best Practices for Structuring Effective Bug Bounty Programs
Explore best practices for structuring effective bug bounty programs, addressing concerns like security, privacy, and legal issues while maximizing vulnerability identification.
PCI DSS and Secure Applications - Best Practices for Compliance
Explore best practices for developing secure applications compliant with PCI DSS requirements. Learn key practices, testing procedures, and evidence needed to meet compliance standards in payment card environments.
OWASP CISO Survey Report 2013 - Tactical Insights for Application Security Managers
Insights from OWASP-CISO Survey 2013: Application security risks, best practices, and management strategies for CISOs. Covers threat sources, investment plans, and security frameworks.
Can AppSec Training Really Make a Smarter Developer?
Explores the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and its impact on application security strategies.
Shift-Left to Address OS Vulnerabilities and Compliance for Cloud Native Applications
Inject security early in software development to address vulnerabilities before production, focusing on OS vulnerabilities and compliance for cloud-native apps.
Engineering Privacy and User Identity Protection from the Start
Discover essential guidelines for prioritizing privacy and user identity protection in project development, ensuring compliance with regulations and safeguarding sensitive information.
Composing the Ultimate SBOM - Creating Accurate and Modular Software Bill of Materials
Explore a modular approach to creating accurate Software Bills of Materials (SBOMs) using Micro-SBOMs, enhancing software security and compliance tracking beyond traditional post-build methods.
Uncovering Software Provenance in Embedded Systems
Explore techniques for tracing software origins in embedded systems, enhancing security and compliance in IoT and edge computing environments.
Curating and Securing Open Source for GovCloud
Explore automated workflows for curating and securing open-source libraries in air-gapped environments, enhancing developer experience while maintaining strong controls over third-party packages.
SLSA in Action: Securing the Software Supply Chain
Live demonstration of securing software supply chain and achieving SLSA compliance using sample repo. OpenSSF SLSA group showcases tooling developed to meet SLSA 1.0 Build Specification, offering practical insights into implementation.
Managing Audits for Critical Open Source Projects
Learn strategies for managing audits of critical open source projects, focusing on security, quality assurance, and best practices for maintaining project integrity.
Rising Threat - Securing Your Open-Source Pipeline
Explore strategies to secure open-source pipelines, addressing vulnerabilities, dependencies, and best practices for robust cybersecurity in software development.
Addressing Cybersecurity Challenges in Open Source Software
Insights on addressing cybersecurity challenges in open source software, including organizational priorities, improvement strategies, and policy drivers. Live panel discussion of key findings from Snyk and Linux Foundation research.