Securing Container Delivery with TUF
Explore TUF's architecture for secure container delivery, protecting against attacks and mitigating risks in software distribution, even after security breaches.
Deep Dive - Runtime Security With Falco in Userspace
Explore runtime security with Falco in userspace, covering eBPF, kernel modules, and ptrace. Learn about tradeoffs, performance impacts, and alternative approaches for cloud-native security.
Deep Dive - What's New With TUF?
Explore new features in The Update Framework (TUF) for secure software updates, including its adoption by PyPI. Learn about flexibility improvements and get involved in cloud native security.
No More Moats - Protecting Your Cloud Native Infrastructure with Zero Trust
Explore Zero Trust security for cloud native infrastructure using SPIFFE, SPIRE, and open-source tools. Learn practical architectures and implementation strategies from Fortune 500 examples.
Bypass Falco
Explore techniques to bypass Falco's runtime detection capabilities, challenging its effectiveness as a security tool. Learn potential vulnerabilities and improve your cloud-native defense strategies.
SAFE - A Cloud Native Security Working Group
Explore cloud native security with SAFE, a working group addressing access controls and safety concerns in modern architectures, presented by Liz Rice from Aqua Security.
An Introduction to Cloud Native Security
Explore cloud native security with CNCF's SIG Security. Learn about ongoing projects, efforts to improve security in cloud native environments, and how to contribute to this evolving field.
The State of Vulnerability in Cloud Native Security
Análisis de vulnerabilidades en herramientas nativas de la nube, presentando resultados de auditorías de seguridad y ofreciendo recomendaciones para mejorar la seguridad en proyectos de código abierto.
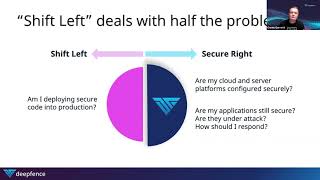
Open Source Cloud Native Security with ThreatMapper
Explore cloud-native security with ThreatMapper, an open-source tool for identifying vulnerabilities and threats in containerized environments. Learn its features, tiers, and deployment strategies.
Security in Cloud-Native
Explore cloud-native security approaches, focusing on data protection, infrastructure trustworthiness, and common vulnerabilities. Learn strategies for securing both Linux and Windows deployments in the cloud.
What We've Learned from Scanning 10K+ Kubernetes Clusters
Insights from analyzing 10K+ Kubernetes clusters: common misconfigurations, vulnerabilities, and RBAC violations. Learn to calculate risk scores, discover weak spots, and improve cloud native security posture.
Implementing Zero Trust Security in MLOps for Intelligent Energy Storage Systems
Discover how to implement Zero Trust security within MLOps for Energy Storage Systems, integrating Kubernetes and OpenStack environments for enhanced cybersecurity in critical energy infrastructure.
Argus - MLOps Platform for Secure and Scalable Data Products in Regulated Environments
Explore how architectural decisions, user-centric design, and business value focus led to a successful data and engineering platform in a regulated enterprise environment.
Unlocking Security Policies and Guardrails - The Bridge Between Dev, Sec and Ops in Kubernetes Deployments
Explore security policies and guardrails in Kubernetes deployments, bridging the gap between development, security, and operations teams for enhanced collaboration and protection.
Secure Kubernetes Manifests with Cosign and Kyverno
Explore open-source tools Cosign and Kyverno to secure container images and Kubernetes manifests. Learn implementation strategies for production clusters and essential use cases.
Kubernetes Goat - Interactive Kubernetes Security Learning Playground
Explore Kubernetes security through hands-on scenarios, attack simulations, and real-world vulnerabilities. Learn to identify and mitigate risks using open-source tools for secure code and container deployment.
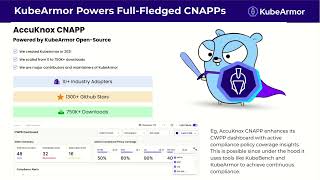
Continuous Compliance in Kubernetes Environments with KubeArmor
Explore continuous compliance in Kubernetes using KubeArmor. Learn to enhance security, maintain regulatory standards, and automate compliance checks in cloud-native environments.
Security in the Open - How Industry and Community Benefit When Security Thrives in Open Source - Keynote
Explore the symbiotic relationship between cloud-native security and industry, highlighting benefits of open-source collaboration for product discovery, developer growth, and establishing security standards.
TAG Security - Enhancing Cloud Native Technology Security
Explore cloud native security with TAG Security leaders. Learn about their work, best practices, and how to contribute to enhancing security in cloud native technologies.
Cloud Native Security for the Rest of Us
Explore key areas of Cloud Native security: platform protection, user management, and software supply chain. Gain insights into best practices and threat mitigation strategies.
Cloud Agnostic or Devout - How Cloud Native Security Varies in EKS - AKS - GKE
Explore security variations in Kubernetes across major cloud providers, empowering teams to implement consistent controls for truly cloud-consistent applications.