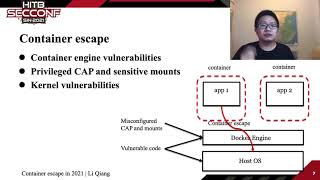
Container Escape in 2021
Explore new methods for escaping privileged runc containers, focusing on cloud security vulnerabilities and innovative exploit techniques in container environments.
The Unbelievable Insecurity of the Big Data Stack
Explore new attack vectors in Big Data infrastructure layers, addressing the lack of security assessment methodologies and technical resources for this rapidly growing field.
BeyondProd- The Origin of Cloud-Native Security at Google - Brandon Baker - USENIX Enigma - 2020
Exploring Google's BeyondProd: A cloud-native security model emphasizing service trust, workload isolation, and automated vulnerability management for microservices-based architectures.
Running at Light Speed - Cloud Native Security Patterns
Explore cloud native security patterns for containerized microservices, covering multi-tenancy, authentication, authorization, and encryption. Learn architectural guidance for secure software design in cloud environments.
Running at Light Speed - Cloud Native Security Patterns
Explore cloud-native security patterns, including container isolation, control plane hardening, and network segmentation. Learn about authentication, authorization, and secrets management in cloud environments.
Open Source Security Tools for Kubernetes Applications
Explore open-source tools for securing Kubernetes applications, covering image scanning, runtime security, and anomaly detection. Learn practical strategies for maintaining a secure cloud-native environment.
Controlled Mayhem With Cloud Native Security Pipelines
Explore cloud-native security pipelines, comparing traditional and modern approaches, while addressing challenges in container orchestration, access control, and CI/CD processes.
Container Security 101
Aprende sobre amenazas, vulnerabilidades y mejores prácticas de seguridad en contenedores, incluyendo herramientas para proteger imágenes y entornos de ejecución.
Deep Dive - Kubernetes Policy WG
Explore Kubernetes Policy WG's progress, KEPs, and future plans for unified policy objects and cloud-native policy white paper in this comprehensive overview.
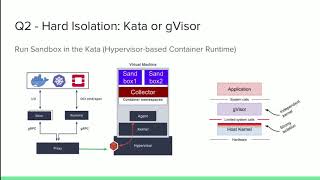
Cloud-Native Sandboxes for Microservices - Understanding New Threats and Attacks
Explore redesigned sandboxing for container environments, improving detection of microservice-oriented attacks and addressing performance challenges in contemporary systems.
Cloud-native Security in Rust with Keylime
Explore Keylime's scalable remote boot attestation and runtime integrity measurement solution, focusing on the recent port of a key component from Python to Rust for enhanced cloud-native security.
Security Nutrition Labels for Cloud Native Projects
Explore a framework for creating security nutrition labels in open-source projects, enabling users to quickly understand potential risks and security implications of software.
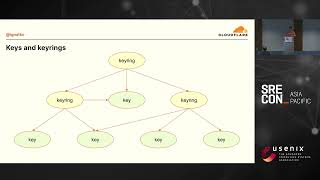
What Is Linux Kernel Keystore and Why You Should Use It in Your Next Application
Explore Linux Kernel Keystore's secure credential management for applications, integrating with security hardware and protecting secrets from memory vulnerabilities in cloud environments.
Protect Against Unknown Security Vulnerabilities
Explore NeuVector's open-source solution for securing cloud-native applications throughout the software development lifecycle, focusing on protection against unknown vulnerabilities in Kubernetes environments.
Your Infrastructure Needs to D.I.E.
Explore how Distributed, Immutable, and Ephemeral (D.I.E.) infrastructure enhances cloud-native security, integrating controlled chaos for continuous improvement and increased resilience against modern threats.
Navigating the Cloud Native Security Landscape
Explore cloud-native security challenges, acronyms, and attack surfaces. Learn about real-world exploits, research data, and see a demonstration of attacks like Log4Shell in relation to different security layers.
What is Linux Kernel Keystore and Why You Should Use It in Your Next Application
Explore Linux kernel keystore's secure credential management, integration with hardware security modules, and benefits for application development in cloud-native environments.
Getting Started With Cloud Native Security
Comprehensive tutorial on Kubernetes security basics, covering threat modeling, attack vectors, and practical techniques for securing deployments using open-source tools and best practices.
How Many CPU Cycles I Need to Invest in Cloud Native Security?
Explore TLS performance in cloud-native environments, comparing implementations, cryptographic suites, and deployment models to optimize security and efficiency in microservices communication.
Kubernetes and Cloud Native Security - A State of the Union
Explore cloud native security challenges, tools, and best practices for Kubernetes and microservices. Learn holistic approaches to harden security during development and deployment in this expert panel discussion.
How to Work in Cloud Native Security - Demystifying the Security Role
Explore cloud native security with Docker's Security Lead. Learn about transitioning from ops/dev to security, key skills, and why it's an exciting field. Gain insights on threat modeling and quality-focused security practices.