Enabling Autonomous Teams With Policy Enforcement at Yubico
Explore Yubico's approach to enabling autonomous teams through policy enforcement, leveraging Open Policy Agent for scalable, flexible, and performant solutions in Kubernetes environments.
Argo - Real Enterprise-Scale with Kubernetes
Explore enterprise-scale Kubernetes with Argo, covering continuous delivery, automated canary deployments, workflows, and security testing in this comprehensive overview.
Implementing Authorization
Explore implementing robust authorization systems using Open Policy Agent, decoupling from authentication for fine-grained control and easier maintenance in various software environments.
Nabla Containers - A New Approach to Container Isolation
Explore Nabla Containers, a novel approach to enhance container isolation by reducing syscall exposure, improving security for cloud environments and container-native applications.
Access Policies for Hybrid Cloud Environments
Explore challenges and solutions for managing access policies across diverse systems in hybrid cloud environments, aiming for a secure and consistent experience.
Deep Dive - Falco
Explore Falco's extended capabilities for ingesting and analyzing diverse event streams, including Kubernetes audit events, to enhance security monitoring and create custom rules for threat detection.
Who Else Is in Your Pod?
Explore pod networking in Kubernetes, including communication between containers, services, and external traffic routing.
Integrating Security in the Build Pipeline
Discover how to integrate security into your build pipeline, addressing vulnerabilities early and making deployment decisions based on artifact security status.
Reducing Attack Surface Using Network Policies
Explore cloud security strategies and learn to implement network policies in Kubernetes to reduce attack surface and enhance system protection.
Strengthening Your Kubernetes Security - Cloud Native Way
Explore Kubernetes security threats, misconfigurations, and defense mechanisms. Learn to detect vulnerabilities, prevent attacks, and secure cloud environments using tools like Kubestriker.
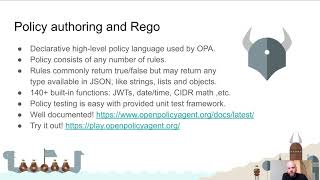
Cloud Native Policy Enforcement with Open Policy Agent
Explore Open Policy Agent for cloud-native policy enforcement, covering deployment options, Rego language, and Kubernetes integration.
Secure Your Cluster-to-Cluster Traffic, the Agnostic Way
Explore secure cluster-to-cluster communication in multi-cloud environments using Kubernetes, Istio, and Consul. Learn strategies for cloud-agnostic data migration and traffic routing across different providers.
Introduction to Open Policy Agent
Explore Open Policy Agent (OPA), a versatile policy engine for Kubernetes, microservices, CI/CD, and cloud. Learn about its features, integrations, and applications in cloud-native security.
Cloud & Cloud Native Identity and Access Management - Challenges & Opportunities
Explore challenges and solutions for identity and access management in hybrid cloud native environments, focusing on achieving continuous identity assurance and zero trust.
Helping One of Europe's Banks Re-platform with Declarative, Self-healing, Multi-cloud WasmCloud Clusters on Kubernetes
Explore next-gen platforms using WebAssembly and wasmcloud for multi-cloud, self-healing clusters. Learn about improved developer productivity, lightweight services, and seamless failover across cloud providers.
AuthN and AuthZ at Cruise - Crawl, Walk, Run
Explore Cruise's journey in implementing authentication and authorization within Kubernetes clusters, from basic approaches to advanced solutions for zero trust security at scale.
Zero Trust Cloud VPN Based on VPP and WireGuard
Explore a Zero Trust Cloud VPN solution using VPP and WireGuard, addressing industry challenges and showcasing innovative architecture for enhanced security and performance.
Sensitive Data in the Cloud? You Can't Do That!
Explore secure handling of sensitive medical data in the cloud, challenging traditional views and discussing practical solutions using Microsoft Azure principles applicable across platforms.
Everything You Always Wanted to Know About Azure Security But Were Afraid to Ask
Comprehensive guide to Azure security features, covering administrative control, data protection, perimeter security, application-level hardening, and monitoring. Includes practical examples and a security checklist for Azure solutions.
Protecting Encryption Keys with Azure Key Vault
Learn to secure cloud data using Azure Key Vault. Protect encryption keys, manage secrets, and implement robust security patterns for regulated industries. Gain practical skills for enhanced data protection.
Protecting Encryption Keys with Azure Key Vault
Learn to protect encryption keys and secrets using Azure Key Vault. Covers setup, configuration, coding patterns, and best practices for secure cloud-based data management in regulated industries.