Secure Your Systems Using Policy-as-Code
Discover how policy-as-code bridges the gap between development and security teams, improving developer experience while maintaining robust system security. Learn implementation best practices and overcome common challenges.

Edge for Business - Safeguarding Against Cyber Threats and AI Risks
Discover how Edge for Business combines enterprise-grade security with AI-powered productivity tools to protect organizations while enabling seamless workflow optimization and innovation.
Extending Network Security to Microsoft Azure Cloud with Next-Generation Firewalls
Discover how to implement robust cloud security using Palo Alto Networks' solutions for Azure, including VM-Series Firewall, Cloud NGFW, and AI Runtime Security for comprehensive protection.
Open Policy Agent (OPA) Introduction and Deep Dive with V1.0 Update
Dive into Open Policy Agent (OPA), exploring policy decision-making across cloud native stacks, from application authorization to Kubernetes admission, with insights into v1.0 features and updates.

Challenges and Opportunities in Storage Security - Data Center Security and Sustainability
Explore evolving storage security trends, from quantum computing challenges to data sanitization requirements, while understanding implementation strategies for secure and sustainable datacenter operations.

SPDM and Post Quantum Cryptography - Security Protocol Updates and Storage Bindings
Explore DMTF's SPDM security protocol updates, including post-quantum cryptography implementation, storage bindings for NVMe/SAS/SATA, and TCP encryption strategies for enhanced data protection.
Introduction and Deep Dive: Kubernetes Infrastructure Maintenance and Security
Dive into Kubernetes infrastructure maintenance, security enhancements, and collaborative development strategies while exploring key achievements and future directions in cloud-native technologies.
Cloud Native's Next Decade: Stable, Secure, and Ready for Disruption - The Future of Cloud Security
Explore the future landscape of cloud native security, examining emerging challenges like AI system protection while understanding why current stability might precede a new wave of innovation.

Open Policy Agent (OPA) Introduction and Deep Dive with V1.0 Updates
Dive into policy decision-making with Open Policy Agent (OPA), exploring its role in cloud-native environments from application authorization to Kubernetes admission control and recent v1.0 updates.
From Silicon to Service: Ensuring Confidentiality in Serverless GPU Cloud Functions
Dive into advanced cloud security concepts, focusing on confidential computing, hardware-based TEEs, and GPU-accelerated workloads for building secure serverless functions with complete stack attestation.
Securing with Love: A Philly Style Approach to Cloud Safety
Discover how security and development teams can collaborate effectively on cloud applications, focusing on practical steps like threat modeling, risk assessment, and maintaining robust security practices.
Building Authorization at Scale with SpiceDB on Amazon EKS
Discover how to implement scalable authorization systems using SpiceDB within Amazon EKS environments, focusing on cloud-native security and access control mechanisms.
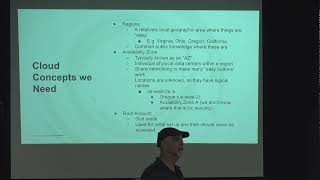
AWS Account Security Best Practices - A DIY Guide
Learn essential AWS security practices and cost-effective strategies to protect your cloud infrastructure without relying on expensive consultants. Gain practical insights for small and medium businesses.
Interesting Vulnerabilities from Public Penetration Testing Reports
Explore real-world security vulnerabilities discovered in mobile, web, VPN, and cloud applications through public penetration testing reports, with focus on critical risks in highly sensitive systems.