Brewing the Kubernetes Storm Center - Open Source Threat Intelligence for Cloud Native Ecosystems
Explore open-source threat intelligence for cloud-native ecosystems. Learn to validate threat models, quantify risks, and make informed defensive decisions using Kubernetes-based environments and real-world data.
Federated IAM for Kubernetes with OpenFGA
Explore federated IAM for Kubernetes using OpenFGA. Learn to centralize and propagate access policies across applications and infrastructure, enhancing security and simplifying administration in cloud environments.

Secret Store CSI Driver Tutorial for Kubernetes and AWS Secrets Manager
Comprehensive guide to Secret Store CSI Driver for Kubernetes security. Learn its importance, comparison with alternatives, and setup process. Includes demos on AWS Secret Manager integration and practical implementation.
Securing a Managed Jupyter Notebook Platform Using Istio and OPA
Learn how to secure a managed Jupyter notebook platform using Istio and OPA. Discover techniques for user isolation, traffic segmentation, and access authorization in multi-tenant ML environments.
(Almost) Secure by Default - Next Steps for Hardening Istio in Production Environments
Explore advanced security measures for Istio in production, including mTLS, certificate management, and integration with network policies and cloud security services for a robust zero-trust architecture.
Bridging Trust Between Multi-Cluster Meshes
Explore secure communication between Kubernetes clusters using SPIFFE, SPIRE, and Istio. Learn to establish trust, manage identities, and configure seamless inter-cluster interactions in multi-cluster mesh architectures.
Enhanced Security for Multi-Tenant Architectures: Key Components and Best Practices
Explore Zero-Trust architecture for securing multi-tenant Kubernetes clusters. Learn best practices, access control, network isolation, and runtime security to fortify against threats and breaches.
The Right Feature at the Right Place - Authorization Example
Explore moving authorization from code to a readable, accessible place using Open Policy Agent and Apache APISIX API Gateway for improved system auditability.
Secret Scanning - Unmanaged Secrets Discovery with HCP Vault Radar
Discover unmanaged secrets, understand risks of not rotating credentials, and learn how HCP Vault Radar detects exposed data to enhance security and reduce attack surface.
OpenHCL: A Linux-Based Paravisor for Confidential VMs
Explore Linux-based paravisor OpenHCL for Confidential VMs, enhancing security and isolation in virtualized environments.
AWS Advanced Networking - Full Course - Part 1
Explore AWS advanced networking concepts, from VPC essentials to SSL/TLS with ACM. Master load balancers, security features, and efficient network architectures for cloud computing.
Continuous Security and Governance in the Cloud Using a Graph-Based CMDB
Explore Reddit's implementation of a graph-based CMDB for cloud security governance, including visibility gains, implementation journey, and the power of centralized configuration data aggregation.
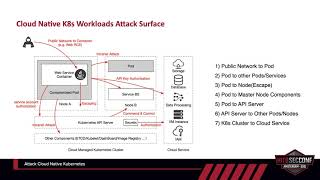
Attacking Cloud Native Kubernetes With CDK
Exploración detallada de técnicas avanzadas para comprometer clústeres de Kubernetes en la nube, incluyendo escape de contenedores y ataques de red. Demostración práctica usando la herramienta CDK.
Attacking Storage Services - The Lynchpin of Cloud Services
Explore cloud storage vulnerabilities and attack techniques, focusing on enumeration, identification, exploitation, and post-exploitation strategies for various cloud services.
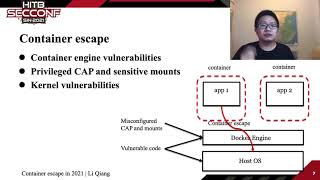
Container Escape in 2021
Explore new methods for escaping privileged runc containers, focusing on cloud security vulnerabilities and innovative exploit techniques in container environments.
Pacu - Attack and Post-Exploitation in AWS
Explore AWS attack and post-exploitation techniques using Pacu, an open-source tool for penetration testing and security assessments in cloud environments.
All Your Cloud Are Belong To Us - Hunting Compromise in Azure
Explore techniques for detecting and investigating compromises in Azure cloud environments, focusing on security best practices and threat hunting strategies.
Secure Your AWS Accounts Without Breaking the Bank
Learn cost-effective strategies to enhance AWS account security, covering essential practices and tools for robust protection without excessive spending.
Understanding, Abusing and Monitoring AWS AppStream 2.0
Explore AWS AppStream 2.0's functionalities, potential vulnerabilities, and effective monitoring strategies for enhanced cloud security and application streaming management.
I'm a Little Bit - FedRAMP - Country, I'm a Little Bit SOC2 'n Roll
Explore the intersection of FedRAMP and SOC2 compliance frameworks, comparing their requirements, implementation challenges, and best practices for organizations seeking certification.
The Northern Virginia Shuffle - Lateral Movement and Other Creative Steps Attackers Take in AWS Cloud Environments and How to Detect Them
Explore lateral movement techniques and creative attack strategies in AWS environments, along with effective detection methods for enhanced cloud security.