The Difference Between Screwing Around (DevOps) and Science (GitOps) - Writing It Down
Explore GitOps principles and their implementation at The New York Times, showcasing how writing down configurations enhances DevOps practices, improves deployment velocity, and ensures standardization.
Automating Enterprise and Industry Regulation Enforcement During Software Delivery
Learn to automate compliance with industry regulations during software delivery using OPA policies integrated with Spinnaker, enhancing CI/CD processes for enterprise development teams.
Salesforce Status Report - Enhancing Spinnaker for Security and Performance
Explore Salesforce's enhancements to Spinnaker, focusing on security, performance, and efficiency improvements. Learn about vulnerability fixes, caching optimizations, and data compression techniques.
Deploying Policy-as-Code with Readable Rego Policies and Open Policy Agent
Learn to implement Policy-as-Code using Open Policy Agent and Rego language. Explore deployment strategies, centralized management, and best practices for writing clear, effective policies in cloud-native environments.
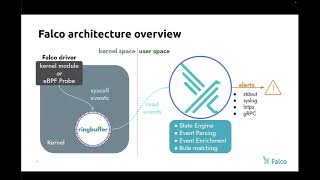
Detecting Five Famous Exploits with Falco
Explore real-world cybersecurity threats and learn to detect them using Falco, enhancing your ability to protect cloud-native environments from sophisticated attacks.

Encrypting Secrets in Kubernetes Clusters Using KMS
Explore robust encryption for Kubernetes secrets using KMS, addressing security concerns and demonstrating live implementation for enhanced cluster protection against potential compromises.
Enabling Sidecar in KEDA for Serverless Security with Azure AD Workload Identity
Explore implementing the sidecar pattern in KEDA with Azure AD Workload Identity for enhanced security and access control in serverless architectures on Kubernetes.
Container Security: Supply Chain, Authorization, and Runtime Protection
Explore container security: supply chain integrity, deployment authorization, and runtime protection. Experts discuss in-toto, TUF, Open Policy Agent, and container escape prevention.
Breaking Out of the Container Without Zero Day - Security Risks in DevOps
Explore container security risks in DevOps environments, focusing on potential vulnerabilities and attack vectors beyond zero-day exploits. Learn strategies to enhance container security and protect your infrastructure.
OWASP Docker Top 10 Security Risks
Explore critical security risks in Docker environments and learn essential mitigation strategies to protect containerized applications from vulnerabilities.
Can Kubernetes Keep a Secret? - Secure Secret Management in Kubernetes
Explore secure secret management in Kubernetes, including native secrets' limitations and alternative solutions like Kamus for encrypting sensitive data accessible only by your app at runtime.
Securing Your Infrastructure as Code Pipeline
Explore techniques for securing Infrastructure as Code pipelines, including static analysis, RBAC, and open-source tools like Open Policy Agent and Sigstore, to enhance productivity and compliance.
Hack My Mis-Configured Kubernetes
Explore common Kubernetes misconfigurations and learn practical hacking techniques to identify and exploit vulnerabilities, enhancing your understanding of container security.
Dynamic Authorization and Policy Control for Kubernetes Clusters
Learn dynamic authorization and policy control techniques for Kubernetes clusters using Open Policy Agent, focusing on admission control and effective policy management.
Container Registries - Beyond Containers in Cloud-Native Environments
Explore the evolving role of container registries in cloud-native environments, their impact on infrastructure, and potential future applications beyond container management.
Designing and Securing Multi-Tenant Runtime Environment at The New York Times
Explore how The New York Times designed a secure, isolated environment for engineering teams using Kubernetes, OPA Gatekeeper, and Cilium, solving multi-tenancy challenges at scale.
Secure Container Deployments - Time for Refresh
Explore modern container security practices, focusing on pod security, policy implementation, and admission controllers for enhanced protection in Kubernetes environments.
Rethinking Compliance in a Containerized World
Explore innovative approaches to compliance in containerized environments, addressing challenges and opportunities in modern infrastructure management.
Kubernetes Risk Assessment - Going One Level Deeper
Explore Kubernetes security risks, dynamic components, and assessment methodologies using MITRE ATT&CK framework to enhance cluster protection and mitigate vulnerabilities.
GitHub Actions Security Landscape
Explore the security landscape of GitHub Actions, uncovering potential vulnerabilities and best practices for safeguarding your CI/CD pipelines.
Navigating the Complexity of Kubernetes and Cloud Native Technologies
Insights on Lens Autopilot's capabilities for managing cloud-native applications, including monitoring, security, and CI/CD automation to streamline Kubernetes adoption and enhance developer productivity.