Applications, Cloud, and Hackers - Security Challenges in Modern Computing - Lecture 1
Explore cloud application security challenges and solutions in this talk, covering threat landscapes, attack vectors, and defensive strategies for modern cloud environments.
Winter is Coming - Cloud Security in Dark Ages
Explore top cloud security concerns, control panels, reliability, APIs, firewalls, redundancy, encryption, logging, and monitoring in this comprehensive overview.
Public Cloud PCI Compliance - Challenges and Solutions
Explore cloud security challenges, PCI compliance in public clouds, and innovative approaches to enhance security posture and meet regulatory requirements.
Hunting for Amazon Cognito Security Misconfigurations
Explore Amazon Cognito security misconfigurations, learn testing techniques for audits and bug bounty hunting, and discover mitigation strategies through a real-world account takeover case study.
Introduction to Confidential Computing - Protecting Sensitive Workloads
Explore confidential computing techniques for protecting sensitive data during processing, focusing on encryption, secure enclaves, and hardware-based isolation in cloud environments.

AWS Security - Shared Responsibility Model, Compliance, and IAM
Explore AWS security essentials: shared responsibility model, compliance, and IAM. Learn how to secure your cloud resources and understand AWS security best practices for developers and IT professionals.
Cloud-Squatting - The Never-ending Misery of Deleted and Forgotten Cloud Assets
Explore the risks of abandoned cloud assets and learn strategies to prevent cloud-squatting attacks, enhancing your organization's cybersecurity posture in the cloud environment.
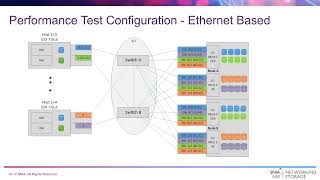
NVMe/TCP - Performance, Deployment and Automation in Enterprise Storage Networks
Explore NVMe/TCP protocol's enterprise features, performance characteristics, deployment strategies, and automation capabilities for modern storage networks and infrastructure management.
KubeHound - Identifying Attack Paths in Kubernetes Clusters at Scale
Discover how to efficiently identify and analyze attack paths in Kubernetes clusters using KubeHound, focusing on scalable security assessment and threat detection techniques.
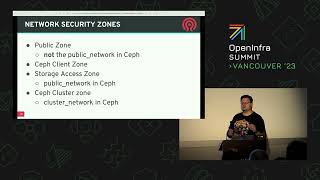
Data Security and Storage Hardening in Rook and Ceph
Explore comprehensive security strategies for Ceph storage systems, from threat modeling and encryption to access controls, focusing on practical hardening techniques for robust data protection.
Why AI Makes Us All Safety Engineers - Building Safety into AI Systems from the Start
Discover how AI's unique nature demands a new approach to software development, integrating safety and security considerations from the earliest stages of planning and design.
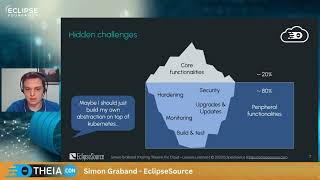
Hosting Theia in the Cloud - Lessons Learned: Building and Securing Cloud-Based IDEs
Discover practical insights and best practices for hosting web-based IDEs and tools in cloud environments using Kubernetes, covering security, monitoring, testing, and deployment workflows.
Falco and eBPF: Optimizing Large-Scale Tracing Tools
Explore eBPF's potential in high-throughput scenarios, focusing on Falco's syscall tracing. Learn about challenges, mitigations, and future enhancements for large-scale tracing tools.
Managing Secrets in GitOps - Best Practices and Tools
Explore strategies for managing sensitive assets in GitOps, including encryption, integration with secrets engines, and leveraging GitOps tools to enhance security in cloud-native environments.
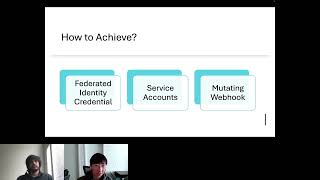
Advancements in Kubernetes Workload Identity for Azure
Explore Azure Workload Identity for Kubernetes, covering simplified architecture, limitations, federated identity, and mutating webhook, with a practical demo on federated credentials.
GitOps for Everything - Automating Microservices, Infrastructure, and SaaS
Explore GitOps implementation for microservices, infrastructure, and SaaS solutions. Learn how AppsFlyer automates 850+ services using Terraform, FluxCD, and Open Policy Agent for safe, manageable deployments.
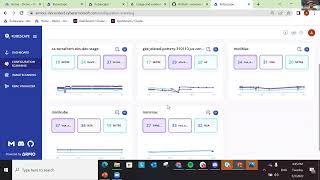
Kubescape: New Features, Improvements, and Future Developments
Explore Kubescape's latest updates, improvements, and future plans for enhanced Kubernetes security and compliance management.
Cloud Native Live: Workload Misconfiguration - The #1 Security Threat When Using Kubernetes
Explore workload misconfiguration, the primary security threat in Kubernetes environments, and learn effective strategies to mitigate risks and enhance cloud-native security.
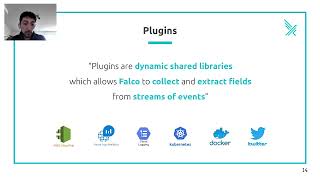
Extend Falco with Plugins - Trigger Alerts with Any Stream of Events
Learn to extend Falco's capabilities with plugins, enabling custom event streams and alerts. Explore architecture, plugin types, SDK usage, and real-world applications for enhanced cloud-native security monitoring.
Your Kubernetes Single-Pane of Glass with Kubescape
Explore Kubescape, a comprehensive tool for Kubernetes security and compliance management, offering a unified view of cluster health and vulnerabilities.
Optimizing Secrets Management - From Integration to Deletion
Improve secrets management lifecycle: integration, creation, rotation, and deletion. Learn strategies for enhancing security and efficiency in handling sensitive information.