Generating Software Bill of Materials (SBOM) Using AWS Inspector
Learn how to generate and utilize Software Bill of Materials (SBOM) through AWS Inspector, covering both console and CLI approaches for effective software component tracking.
Unlocking Security Insights for Everyone with AI - Using Large Language Models
Discover how AI and Large Language Models democratize cloud security by simplifying complex data analysis, enabling plain-language queries, and fostering better organizational collaboration.
Storage Sanitization Standards and Evolution in Data Security
Explore modern data sanitization standards and methodologies for storage devices, including updates to ISO/IEC 27040, IEEE 2883-2022, and emerging guidelines for secure data erasure.
Breaching AWS Through Shadow Resources - Critical Vulnerabilities and Security Implications
Uncover critical AWS vulnerabilities and security insights through real-world examples of shadow resource exploitation, featuring detection methods, privilege escalation techniques, and best practices for cloud security.
GhostToken - Exploiting Google Cloud Platform to Create Unremovable Trojan Apps
Uncover a critical GCP vulnerability that enables malicious apps to become invisible and unremovable from Google user accounts, exploring OAuth 2.0, exploitation techniques, and security implications.
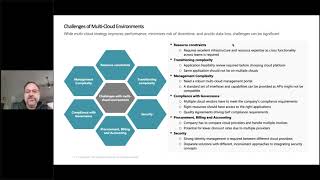
Building Multi-Cloud Success for Cross-Database Usage
Explore strategies for successful multi-cloud implementation, focusing on critical software layers between clouds, security challenges, and optimizing data management across heterogeneous environments.
Reining in Cloud Chaos: Best Practices for CIOs
Learn how to centralize, secure, and manage information flow between on-premises systems and cloud applications. Discover best practices for successful cloud integration strategies and innovative IT models.
Data Protection at AWS - Securing Cloud Applications
Discover essential strategies for securing AWS-based applications, including network protection, encryption, key management, and storage architecture. Learn from real-life examples to avoid common pitfalls and ensure data safety.
Moving to the AWS Cloud - Strategies for Successful Migration
Comprehensive guide to AWS migration, covering key services, strategies, and best practices for successful cloud adoption. Ideal for those considering alternatives to data center operations.
Mitigating Log4Shell and Similar Vulnerabilities Using Cloud Services
Explore how cloud services mitigate vulnerabilities like Log4Shell by blocking attacks, preventing data exfiltration, protecting sensitive information, and enabling forensic analysis in Java applications.
AWS IAM - Identity Access Management Crash Course
Master AWS IAM essentials: account creation, policy assignment, and best practices for secure and efficient identity management in Amazon Web Services.
Cloud Engineering: Developers and Infrastructure Teams Collaborating for Cloud-Native Architectures
Explore cloud engineering practices for developers and infrastructure teams to collaborate effectively, tame cloud complexity, and innovate through cloud-native architectures and modern software development techniques.
Provable Security at AWS - Automated Reasoning for Cloud Security
Exploring AWS's provable security: Using automated reasoning to detect misconfigurations and provide absolute assurance in cloud security, protecting customers in an evolving threat landscape.
InfoSecurity 2015 - Building Data Protection in the Cloud
Explore cloud data protection strategies, including ownership, security measures, and emerging threats, with insights from Google's Director of Security.
How Security Can Keep Pace with Continuously Evolving Cloud-Native Applications
Explore dynamic security approaches for cloud-native apps, aligning with modern development lifecycles and infrastructure-as-code to ensure security evolves alongside rapid architectural changes.
Cloudy with a Chance of Persistence - 2019
Explore cloud persistence techniques and their impact on security in modern computing environments.
The FaaS and the Curious - Exploring AWS Lambda Security in 2018
Explore AWS Lambda's attack surface, including function hijacking, cloud environment access, and runtime reverse engineering. Learn about FaaS security risks and potential exploits.
Poking Holes in the Cloud: Auditing AWS Security - 2018
Explore tools and techniques for penetration testing AWS-hosted systems, covering reconnaissance, exploitation, and key insights for enhancing cloud security.
Serverless Security: A Pragmatic Primer for Builders and Defenders - 2017
Explore serverless security challenges and practical approaches in software supply chain, delivery pipeline, data flow, and attack detection. Learn serverless basics and adoption patterns.
Architecting for Security in the Cloud - 2017
Discover strategies to identify and close security gaps in cloud applications, building robust architectures that can withstand Internet attacks while maintaining scalability and agility.
Cloud Security at Scale: The Chaos Continues - Part 2
Explore real-world cloud security implementations in finance and regulated industries, with insights on improvements and challenges faced by organizations.