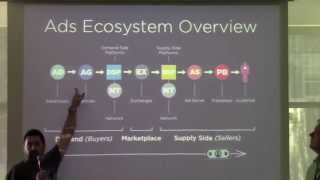
Modern Malvertising and Malware Web-Based Exploit Campaigns
Explore modern malvertising and web-based exploit campaigns, including top malware types, real-world attack breakdowns, and emerging threats in this technical presentation on cybersecurity.
Security and Modern Software Deployment - AppSec EU 2015
Explore modern software deployment security challenges, including trust issues, dependencies, and repository vulnerabilities. Learn strategies to mitigate risks and enhance deployment security.
Malware and Defense Techniques - OWASP AppSec Europe 2014
Explore cutting-edge malware detection, web security, and network defense techniques from industry experts at OWASP AppSec Europe 2014. Gain insights on cloud-based solutions, botnet detection, and advanced web application protection.
OWASP AppSecUSA 2014 - Defenders Track Sessions
Explore cutting-edge cybersecurity topics including secure software design, memory scraping malware, cloud security, phishing detection, and attacks on in-memory platforms in this OWASP AppSecUSA conference.

Cloud-based Detection Techniques for Botnets and Malware - AppSecEU 2014
Explores cloud-based techniques for detecting botnets and malware, highlighting limitations of traditional methods and discussing traffic analysis for pre-infection detection in cloud environments and virtual infrastructures.
How to Spy with Python - Understanding PRISM and Cloud Security
Explore PRISM's impact on cloud services and learn strategies for securing data and preserving privacy in the cloud, with insights on leveraging cloud-based software while maintaining confidentiality.
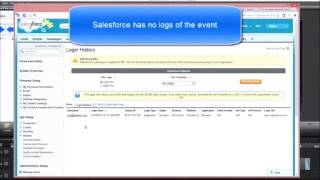
The Rise of SaaS-Targeted Malware - Zeus Variant Attacking Salesforce Users
Demonstration of a new Zeus malware variant targeting Salesforce users, showcasing its stealthy data exfiltration capabilities and discussing implications for SaaS security.
State of Intel SGX in Linux
Comprehensive overview of Intel SGX support in Linux, covering kernel interface, features, and confidential computing run-times. Explores the maturing SGX ecosystem and its status as a mainline kernel technology.
Improving Bootup Performance of Containers with Overlay Images in TEE Environments
Optimizing container bootup in TEE environments: Accelerating image downloads, reducing key negotiation overhead, and offloading image decryption for improved performance and security.
Future of CVE - Challenges and Developments in Vulnerability Identification
Exploring CVE's evolution, challenges, and future directions in cybersecurity, including ID reservation, counting methods, new services, and emerging issues like cloud vulnerabilities.
Cloud Native Storage Solutions for Ransomware Protection
Explore cloud-native storage solutions to protect against ransomware attacks, featuring insights from Red Hat experts on enhancing data security in modern IT environments.
Throw Away Your Passwords - Trusting Workload Identity
Explore modern workload identity solutions for enhanced security, eliminating password vulnerabilities in cloud-native environments.
Supply Chain Security: From Infrastructure to Application, Code to Cloud
Explore best practices for securing the entire software supply chain, from infrastructure to application, covering code, cloud, dependencies, and deployment.
Introduction to Threat Modeling in the Cloud
Learn essential techniques for identifying and mitigating security risks in cloud environments through threat modeling, with practical insights from the Argo Project Threat Model.
HashiCorp's Multicloud Zero Trust Platform
Explore HashiCorp's innovative platform for implementing zero trust security across multicloud environments, enhancing data protection and access control.
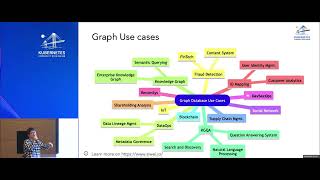
Graph Driven DevSecOps in Practice
Explore graph-driven DevSecOps implementation strategies, enhancing security integration in cloud-native development pipelines for improved efficiency and risk mitigation.
What Can Go Wrong When You Trust Nobody? Threat Modeling Zero Trust
Explore Zero Trust principles and threat modeling for cloud-native systems. Learn to implement secure architectures using Istio, Kubernetes, SPIRE, and OPA for robust, distributed workload protection.
Software Bill of Materials (SBOM) in Kubernetes - Best Practices and Approaches
Explore SBOM implementation in Kubernetes, comparing approaches and best practices. Learn how Paketo Buildpacks embeds SBOMs in application images using Syft, enhancing software supply chain security.
Securing Open Source Software Supply Chain - Continuous Secure Software Ingestion
Explore secure OSS ingestion in enterprises using Continuous Secure Software Ingestion (CSSI) application, built on Tekton & Open Policy Agent, for automated artifact grooming and policy-driven security checks.

Secure CI/CD Using JSON Web Token (JWT)
Explore how GitLab leverages JWT for secure access to secret management solutions, enhancing DevSecOps practices and addressing challenges in retrieving sensitive data across cloud providers.
Identity Based Segmentation for Zero Trust Architecture
Explore Zero Trust Architecture implementation using identity-based segmentation, focusing on cloud-to-premises communication through DMZs with identity-aware proxies and service mesh.