
Setting Up AWS VPC: Public and Private Subnets, NAT, Internet Gateway, and Route Tables - Part 5
Set up a secure AWS VPC with public and private subnets, NAT, Internet Gateway, and route tables. Learn to launch EC2 instances and manage VPC components effectively.

Bastion Host and Its Importance - Step-by-Step Tutorial - Part 6
Explore bastion host setup for secure remote access to private network servers. Learn VPC creation, subnet configuration, and SSH key management in this hands-on tutorial.

AWS Lambda: Function URL, Environment Variables, and Lambda Layers - Step-by-Step Tutorial
Master AWS Lambda: create functions, deploy via zip/S3, update, enable Function URLs, set environment variables, and utilize Lambda Layers in this comprehensive tutorial.

Mastering AWS Network Load Balancer - ALB vs NLB Tutorial - Part 18
Explore AWS Network Load Balancer creation, compare with Application Load Balancer, and learn path-based routing. Gain hands-on experience in setting up scalable cloud infrastructure.
EC2 Essentials: Setting Up VPC, Subnets, Gateways, and Jump Host - Part 14
Aprenda a configurar EC2, VPC, subredes, tablas de enrutamiento, gateways de Internet y NAT, y host de salto en AWS. Domine la infraestructura de red esencial para implementaciones seguras en la nube.
AWS EC2 Auto Scaling Explained - Ultimate Tutorial and Live Demo - Part 18
Master AWS EC2 Auto Scaling: Learn to automatically adjust EC2 instances based on demand. Explore components, scaling types, and best practices through a comprehensive tutorial and live demonstration.

Ultimate AWS EBS Volume Guide - From Zero to Hero - Part 20
Master EC2 EBS volumes: create, attach, resize, snapshot, and understand volume types. Learn crucial mounting commands for optimal AWS storage management.
Master EC2 Spot Instances: Ultimate Guide to Massive Savings - Part 21
Optimize cloud costs with EC2 Spot Instances. Learn to create Spot Fleet requests, launch templates, and combine with On-Demand instances for high availability and performance.
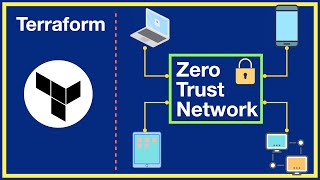
How to Automate Zero Trust: Step-by-Step Twingate and Terraform Guide
Automate Zero Trust implementation using Twingate and Terraform on AWS. Learn to set up secure remote access, configure resources, and test connectivity from mobile and laptop to EC2 instances.
AWS S3 and Terraform Guide - Part 23: Advanced S3 Features
Master AWS S3 with Terraform: Create buckets, upload objects, encrypt data, set IAM policies, enable versioning, configure lifecycle rules, set up logging, and implement object lock for robust cloud storage management.
Serverless TOP 10 Security Issues and Protection Patterns for AWS - 2023
Explore top 10 serverless security issues and protection patterns for AWS, covering event injection, denial of wallet attacks, and cloud misconfigurations in this comprehensive guide.

AWS AI Services Transforming DevSecOps - Amazon Q Insights
Explore how AWS AI services like CodeGuru, Amazon Q, and GuardDuty revolutionize DevSecOps, enhancing code quality, extracting insights, and bolstering security in AWS environments.
Additional Microsoft Cloud Data Sets for Enhanced Security Visibility
Explore additional Microsoft cloud datasets beyond standard logging to enhance visibility, detect suspicious activity, and defend against tools like GraphRunner exploiting Graph API vulnerabilities.
Cluster and Application Lifecycle Management with k0smotron and ArgoCD
Discover how k0smotron and ArgoCD streamline multi-cluster Kubernetes and application lifecycle management. Learn to implement a fully declarative stack using open-source tools for agile, lock-in-free operations.
Terraform: Stand Up Test Environments Fast with AWS
Learn to rapidly deploy test environments on AWS using Terraform. Explore GitLab repos, CloudWatch alerts, S3 buckets, Lambda functions, and ECS deployment pipelines for efficient proof-of-concept testing.
COCONUT-SVSM on KVM: Progress, Plans, and Challenges
Explore COCONUT-SVSM's evolution to a paravisor layer, recent achievements, and challenges in KVM integration. Learn about proposed solutions for AMD SEV-SNP VMPLs and Intel TDX partitioning support.
Empowering Confidential VMs to Use Custom Firmware in Cloud Environments
Empower confidential VMs to use custom firmware, enhancing security and control. Learn a method for supplying UEFI firmware via VM disk images, enabling user-controlled updates without disrupting workloads.
The Confidential Computing Story: Early Development Across the Stack - Part II
Explore early development challenges in Confidential Computing, focusing on Kata and Confidential Containers projects. Learn about building upper stacks on moving pieces and collaborative solutions.
Coconut-SVSM - Early Attestation to Unlock Persistent State - KVM Forum
Explore early attestation for unlocking persistent state in Coconut-SVSM, enabling stateful services like vTPM and secure UEFI variable store for Confidential VM guests on AMD SEV-SNP platforms.
Is OVMF too Slow for Serverless Confidential Computing?
Explore OVMF performance in serverless confidential computing, analyzing benchmarks, overheads, and potential solutions for SEV and SNP guests.
Managing Infrastructure as Code at Scale With env0
Explore common IaC challenges and learn how env0 simplifies infrastructure automation through a hands-on demonstration of managing Infrastructure as Code at scale.