Kubernetes Security Implementation Landscape
Explore Kubernetes security implementation strategies and best practices with expert Zhang Jintao, gaining insights to enhance your cloud-native infrastructure protection.
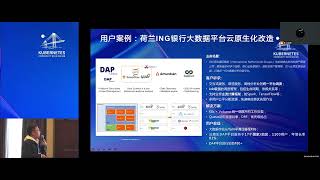
Volcano for FinTech Big Data on Kubernetes
Explore how Volcano enhances FinTech BigData operations on Kubernetes, optimizing resource management and workflow efficiency for financial technology applications.
Lessons Learned from Building Kubernetes for Small Edge Devices
Explore challenges and solutions in adapting Kubernetes for resource-constrained edge devices, covering CNI, CSI, updates, and conformance testing for MicroShift.io.
Fractional GPU Allocations with MetaGPU Device Plugin for Kubernetes
Explore fractional GPU allocation in Kubernetes using MetaGPU, an open-source project enabling dynamic GPU sharing, memory enforcement, and efficient resource utilization for AI/ML workloads.
Is Istio Ambient Mesh Secure - Exploring Service-to-Service Security
Explore Istio Ambient Mesh's security features, including mTLS, workload identity, and infrastructure-application boundaries in a sidecarless data plane architecture for zero-trust service mesh.
Scaling GitOps Using ArgoCD Application-Sets - Lessons Learned
Discover how ArgoCD ApplicationSets revolutionize GitOps, simplifying deployment across multiple repositories and enhancing scalability. Learn from real-world implementation challenges and best practices.
ArgoCD as the Engine for Brownfield Migration to Kubernetes
Learn how a small team used ArgoCD to migrate to Kubernetes, integrating CNCF products like Istio, Helm, and Prometheus. Discover strategies, pitfalls, and resources for successful implementation and developer self-service.
Argo Workflows in Action: Rabobank's Journey to Cloud Native Banking
Rabobank's transition to cloud-native banking using Argo Workflows: challenges, solutions, and best practices for managing complex job dependencies in a financial institution.
Scaling Argo Security and Multi-Tenancy in AWS EKS at The New York Times
Explore NYT's approach to scaling Argo security and multi-tenancy in AWS EKS, focusing on architectural patterns, IAM integration, and solutions for scaling challenges in a multi-cluster environment.
Calling OPA from eBPF Through WASM in the Kernel - Exploring Unconventional Technology Integration
Explore the integration of eBPF, WASM, and OPA in kernel space, showcasing innovative approaches to cloud-native technologies and their potential impact on system performance and security.
Running Istio in Production as a Small Team
Discover how a small team implemented Istio for efficient traffic management during a Kubernetes migration, overcoming challenges and enabling seamless transition of 300+ microservices.
Kubernetes v1.27 Release Overview
Explore the latest features and improvements in Kubernetes v1.27, enhancing container orchestration and cloud-native application deployment.
Container Patching: Making It Less Gross Than the Seattle Gum Wall
Explore strategies for efficient container patching, including prevention, detection, fixing, and monitoring. Learn about opensource tools and best practices to streamline the process and meet security requirements.
Hands-on Hacking Kubernetes and Ways to Prevent It
Hands-on workshop exploring Kubernetes vulnerabilities and prevention strategies. Demonstrates remote code execution exploit and teaches mitigation techniques for enhanced container security.
Solving Multi-Service Communication Without a Service Mesh
Explore Kubernetes primitives for secure microservices communication without service mesh. Learn about NetworkPolicy, token projection, API gateways, and more for authentication, encryption, and compliance.
Cloud Cost Monitoring with OpenCost and Kubernetes Optimization Strategies
Explore OpenCost for Kubernetes cost monitoring and learn optimization strategies for workloads, infrastructure, and operating systems to enhance cloud efficiency.
Avoiding IAC Potholes with Policy and Cloud Controllers
Discover how to secure self-serve cloud infrastructure for Kubernetes teams using policy engines and cloud controllers. Learn to enforce compliance while enabling application teams to provision resources efficiently.
Unpacking Open Source Security in Public Repositories and Registries
Explore security risks in popular open-source projects and public registries. Learn about common misconfigurations, vulnerabilities, and best practices to safeguard your systems when using public resources.
Securing Self-Hosted GitHub Actions with Kubernetes and Actions-Runner-Controller
Explore secure deployment of self-hosted GitHub Actions runners using Kubernetes and actions-runner-controller. Learn about cluster settings, controller configurations, and runner pod security for regulated environments.
From the Cluster to the Cloud: Lateral Movements in Kubernetes
Explore techniques for lateral movement from Kubernetes containers to cloud resources, covering RBAC misconfigurations, authentication methods, and real-world incidents. Learn prevention and detection strategies.
Beyond Cluster-Admin - Getting Started with Kubernetes Users and Permissions
Learn to implement users and permissions in Kubernetes clusters, covering user provisioning methods, RBAC for fine-grained access control, and strategies for both managed and self-hosted environments.